pete
-
Posts
7,810 -
Joined
Content Type
Forums
News
20th
EduGeek EDIT Conference
Blogs
Everything posted by pete
-
Defend the network perimeter As you've already guessed, if the county/RBC is your service provider, they should be able to describe (in technical detail) how they secure your router and the firewalling between you and the Internet. This (for a value of Lincolnshire/EMBC/KCOM at least) is readily available once you find a technical person or have a login to the correct portal. Ask to speak to the security team at the RBC. But equally, if you provide BYOD access to students/guests/teachers, you need to ensure that's appropriately secured and fenced off from the rest of the network. It's also worth pointing out that while defending the network perimeter is great, if the inside is soft and mushy then anything that gets past the perimeter will have an easy time of it. Internally you should have controls such as VLANs to segregate traffic. Monitor and test Security Controls You make sure patches are installed? That firewall configs work in the way you intend and are appropriate? That mail filtering works properly? That permissions are appropriate and access is set up in a way (using permission groups rather than assigning individual users to folder structures, for example) that makes it simple to audit this? etc. TLDR: What do you do you ensure your network is secure and access is appropriate? How do you test/review this? What proof do you have? Filter out unauthorised and malicious content You already do this. Antivirus, mail filters, web filtering, esafety software (if you use it). You review security permissions to ensure they're appropriate and if someone changes roles you adjust their access accordingly. You (presumably) restrict executable content running from temporary locations, you've got file server filters to give early warnings of cryptolocker-type malware. Log analysis I'll preface this by saying it takes time to set up and tune the signal-to-noise ratio. Pick one low-traffic server to begin with. Internally, you should be monitoring logs on your servers, network devices, etc for anomalies and have some way of presenting those anomalies to yourselves in order of important. Windows natively lets you forward particular events of your choosing to (for example) another Windows server acting as a logserver. You should be flagging up things like invalid login attempts, invalid login attempts followed by a success, changes made to AD, odd webserver requests, changed files on servers etc (list not anywhere near exhaustive). Most log analysis software will already have filters to flag these events up. For log analysis we use a combination of Wazuh (wazuh.com), which is a fork of OSSEC integrated with Elasticsearch, Logstash and Kibana. We supplement that with Observium for network traffic and device monitoring and we also use Icinga for up/down alerting. Icinga automatically creates tickets for our attention if certain things happen and Wazuh automatically filters alerts by priority.
-
Paxton Net2 Pro - any known annoyances/design issues from an IT POV?
pete replied to pete's topic in Physical Security
Yup, I brainfarted and completely missed that. I blame insufficient coffee. -
Terry Pratchett's unpublished works crushed by steamroller
pete replied to elsiegee40's topic in IT News
^ Yeah - IIRC, Terry had sufficient monitors on his desktop to put a decent-sized NOC to shame. I'd have expected SSDs or at least SATA.
-
Terry Pratchett's unpublished works crushed by steamroller
pete replied to elsiegee40's topic in IT News
I suspect the river police vetoed burning them in a longboat down the Thames? -
Yeah, point your DCs to a known-good source (I use uk.pool.ntp.org) and then point everything else to your DCs (Windows PCs on a domain should get time from the DCs automatically). While you're at it, point your switches/routers to the DCs so your log timestamps sync up. Rather than writing out the steps, I'm going to point you to this recent thread: http://www.edugeek.net/forums/windows-server-2016/187267-set-external-ntp-dc.html
-
Paxton Net2 Pro - any known annoyances/design issues from an IT POV?
pete replied to pete's topic in Physical Security
For those of you with the software on a server (presumably virtual and/or in a remote server room), how did you get the token info from the Paxton reader > Net2 software? Did you sling a local install on a PC, import/create the users and then export the CSV to the server? Poking around with RDP options, the reader doesn't present to the remote server using the "smartcard" or "other pluggable devices" options, which is annoying if not entirely unexpected. -
In SIMS, it's trivial to notify HOY, Form Tutor and SLT (named individual option) about behaviour incidents. If, however, the Head of Maths would like to keep an eye on things happening in Maths lessons, there doesn't seem to be an easy way to script/report on this such that the HOD doesn't have to go poking around to find the info. How do you automatically (without a human have to faff about) report behaviour incidents to heads of faculty / dept in SIMS?
-
I know the Netbotz can be quite granular, but I don't think our main UPS is. Assuming it's sending via a mailserver you control, sling a transport rule in that looks for a word/phrase that only exists in the messages you want and just forwards those on?
-
It also depends on how much whoever's paying for the SAN is (or was) willing to spend on service contracts, out-of-hours in-house support and a host of other things. Unfortunately, sometimes that money only gets spent after it hits the fan and $person_who_saved_money loses a lot of face.
-
[sims] SIMS Report Macros and protecting against Cryptolocker
pete replied to 5tu's topic in MIS Systems
There's a patch out for the same thing - 23191, IIRC. -
^ Yeah, the two I'm looking at both have foam and 120mm (eyeballing it) fans to shift air left > right in the case. The more expensive one is quietier if you buy the extra top and bottom baffles according to a company rep, but there's apparently not a lot in it between the cabinets.
-
Is the previous incumbent contactable and on agreeable terms with the school? This is when I'd be nudging SLT / LM to chase them with sticks (albeit politely) for not providing access to systems when they left the job.
-
It's not the system used to send them that's the issue. It's taking information recorded/processed for one reason (informing them about their kid) and using it for another reason (marketing some random event at school). Processing the data for marketing purposes requires consent. And a method in the system to ensure you don't email/txt marketing bumpf to people who haven't opted in.
-
[android] Smartphone - up to £300 - replacing a Nexus 5?
pete posted a topic in Mobile Devices & Tablets
As I suspect my Nexus 5 is on it's last legs, I'm in the market for an Android smartphone. I've been considering: Moto G5 (£169) / G5 Plus (£250) Nokia 6 (£200). I've ruled out: WileyFox - inconsistent build quality Samsung - had one before - decent hardware, terrible cruft and patching schedule. Anything that requires rooting - my phone's used for 2FA on too many things for this to be viable. Need: Regular security updates Fairly stock Android 32GB space Dual SIM NFC Decent camera Decent battery life Not a phablet - should fit in a trouser pocket Reasonably nippy Will last for 3yrs or so - Gorilla glass or equivalent and good build quality. What else is worth looking at in the sub-£300 price range? -
I'm doing it on Linux, but adding "> results.txt" on the end of a command should redirect the output to a text file called "results.txt". That works on Windows for other applications, so I don't see why Nmap would be different. Lose the "> results.txt" part for now. You adjusted the IP range (10.0.0.1-255) for one appropriate to your network/VLAN, right? When you ran nmap it checked 255 hosts but didn't find anything with ports 22,80 or 443 open, then whined because it decided ">" and "results.txt" were also hosts. If you're really finding nothing on the IP ranges at your school, maybe check to see if the previous person was using telnet (port 23)?
-
I forsee a console cable in your future. Fire up nmap or similar and start port scanning? I assume if the previous incumbent wasn't diligent enough to write documentation they also weren't diligent enough to configure a management VLAN, so you should find likely candidates. Look for devices listening on port 22/80/443 that aren't things you recognise and go from there. nmap --open -p 22,80,443 10.0.0.1-255 > results.txt That would scan the IP range and report if ports 22, 80 or 443 were open. From there you can whittle the list of candidates down. Once you have some candidates, use (nmap -A 10.0.0.1) to provide a bit more detail about what the host could be, based on service info. CDP or LLDP (show lldp info remote-device e2) might give you some clues too, if you have a login to at least one switch (that supports lldp/cdp).
-
What happens if you sling a " /reliable:yes" in there? Like: w32tm /config /manualpeerlist:timeserver(s) /syncfromflags:manual /reliable:yes /update
-
I'm looking at the Orion Acoustic wall mount cabinet range: Acousti Products - Orion Acoustic Wall Mountable Rack Range (£300) and the UCoustic 7250 wall cabinet range: Quieter Switches and Routers with the UCoustic 7250 Acoustic Wall Box (£460) To replace a 12U wallmount that's in a location soon to become an office. It's got a 1U 48 port switch and a 24port PoE+ switch and ~90 copper runs and 4 fibre runs. Does anyone have either or a similar product? I'm wondering how much more "quiet" the extra £160 earns me or whether it's just fit and finish improvements.
-
It's in the public interest for schools to communicate with the legal guardian about how the kid is (or isn't) doing at school. If the parents are a safeguarding concern (insert crazy/violent parent example), then issues may be discussed with social services instead, but ultimately the person under discussion is the shared responsibility of the school, parents and government. They need to communicate with each other about the person they're looking after.
-
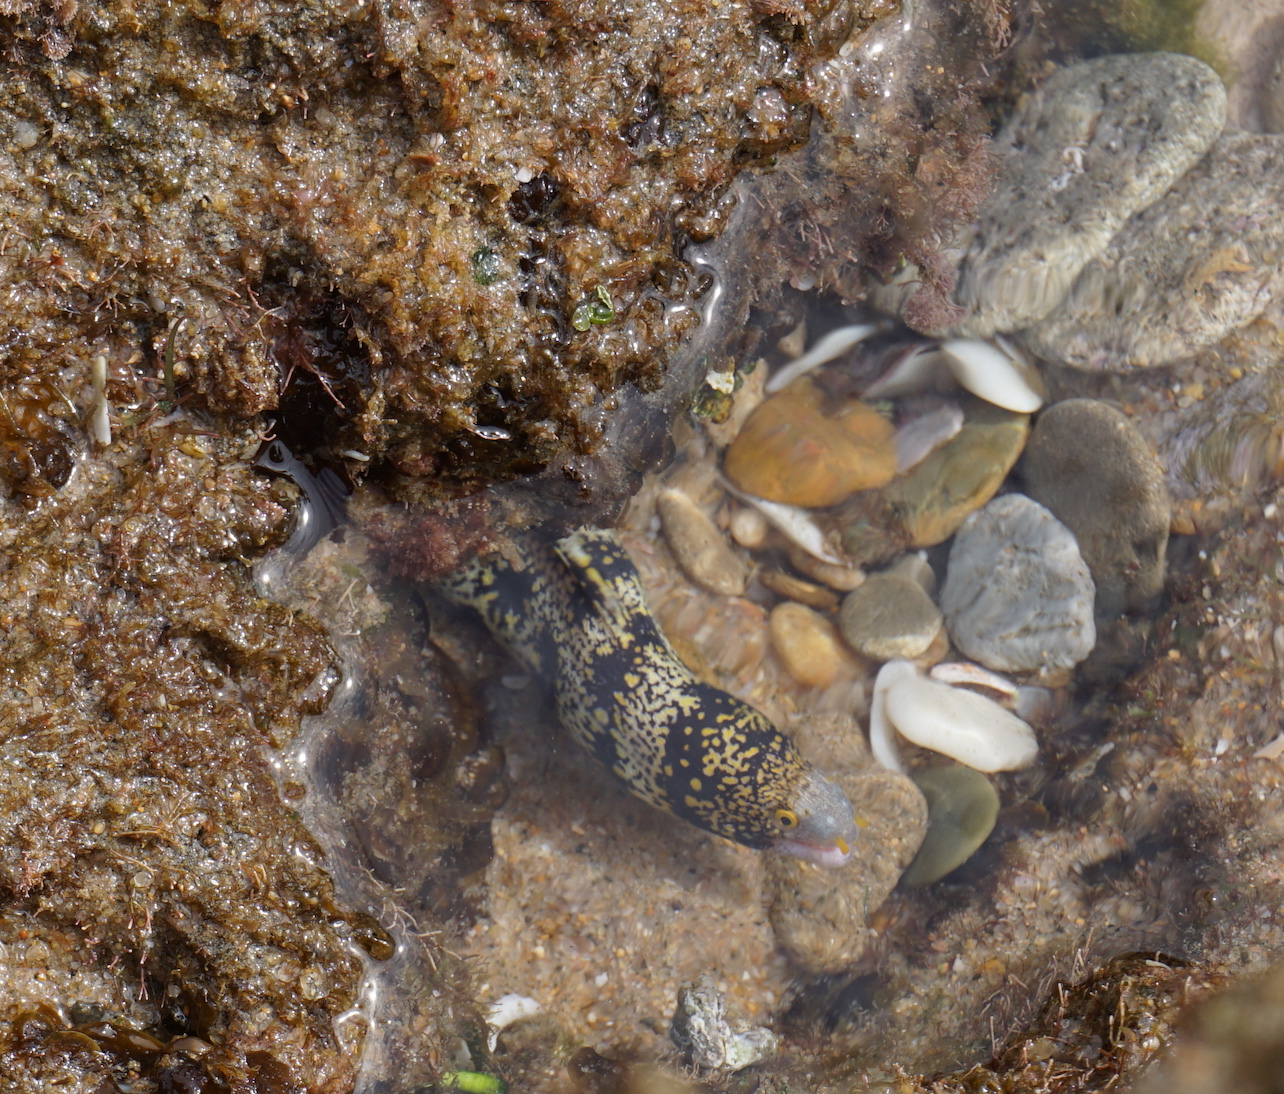
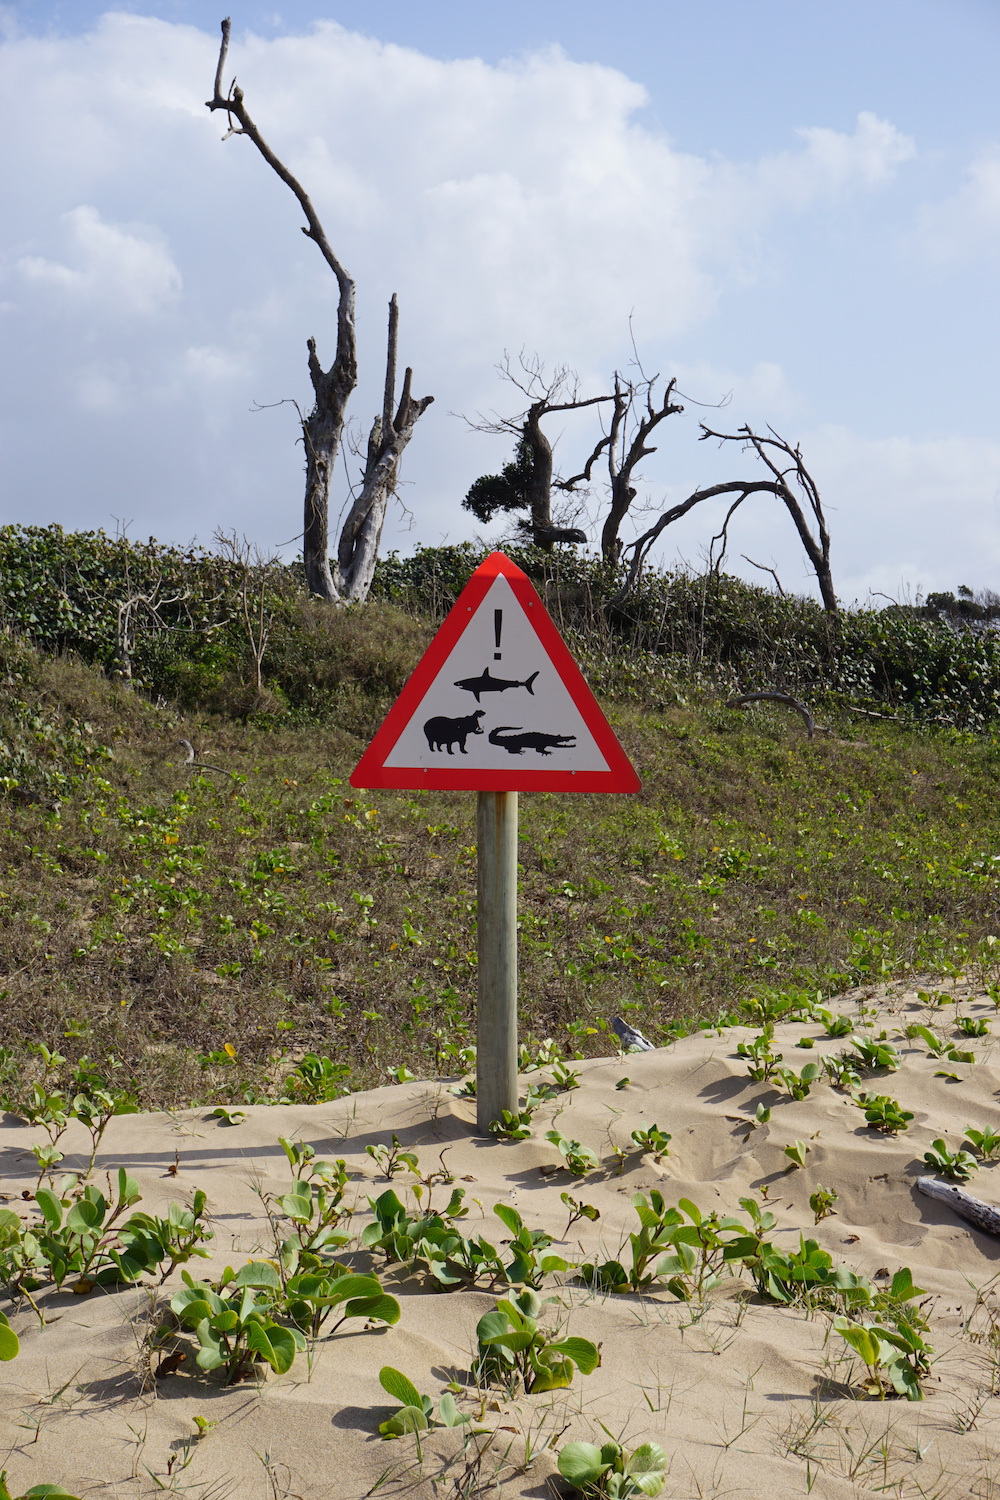
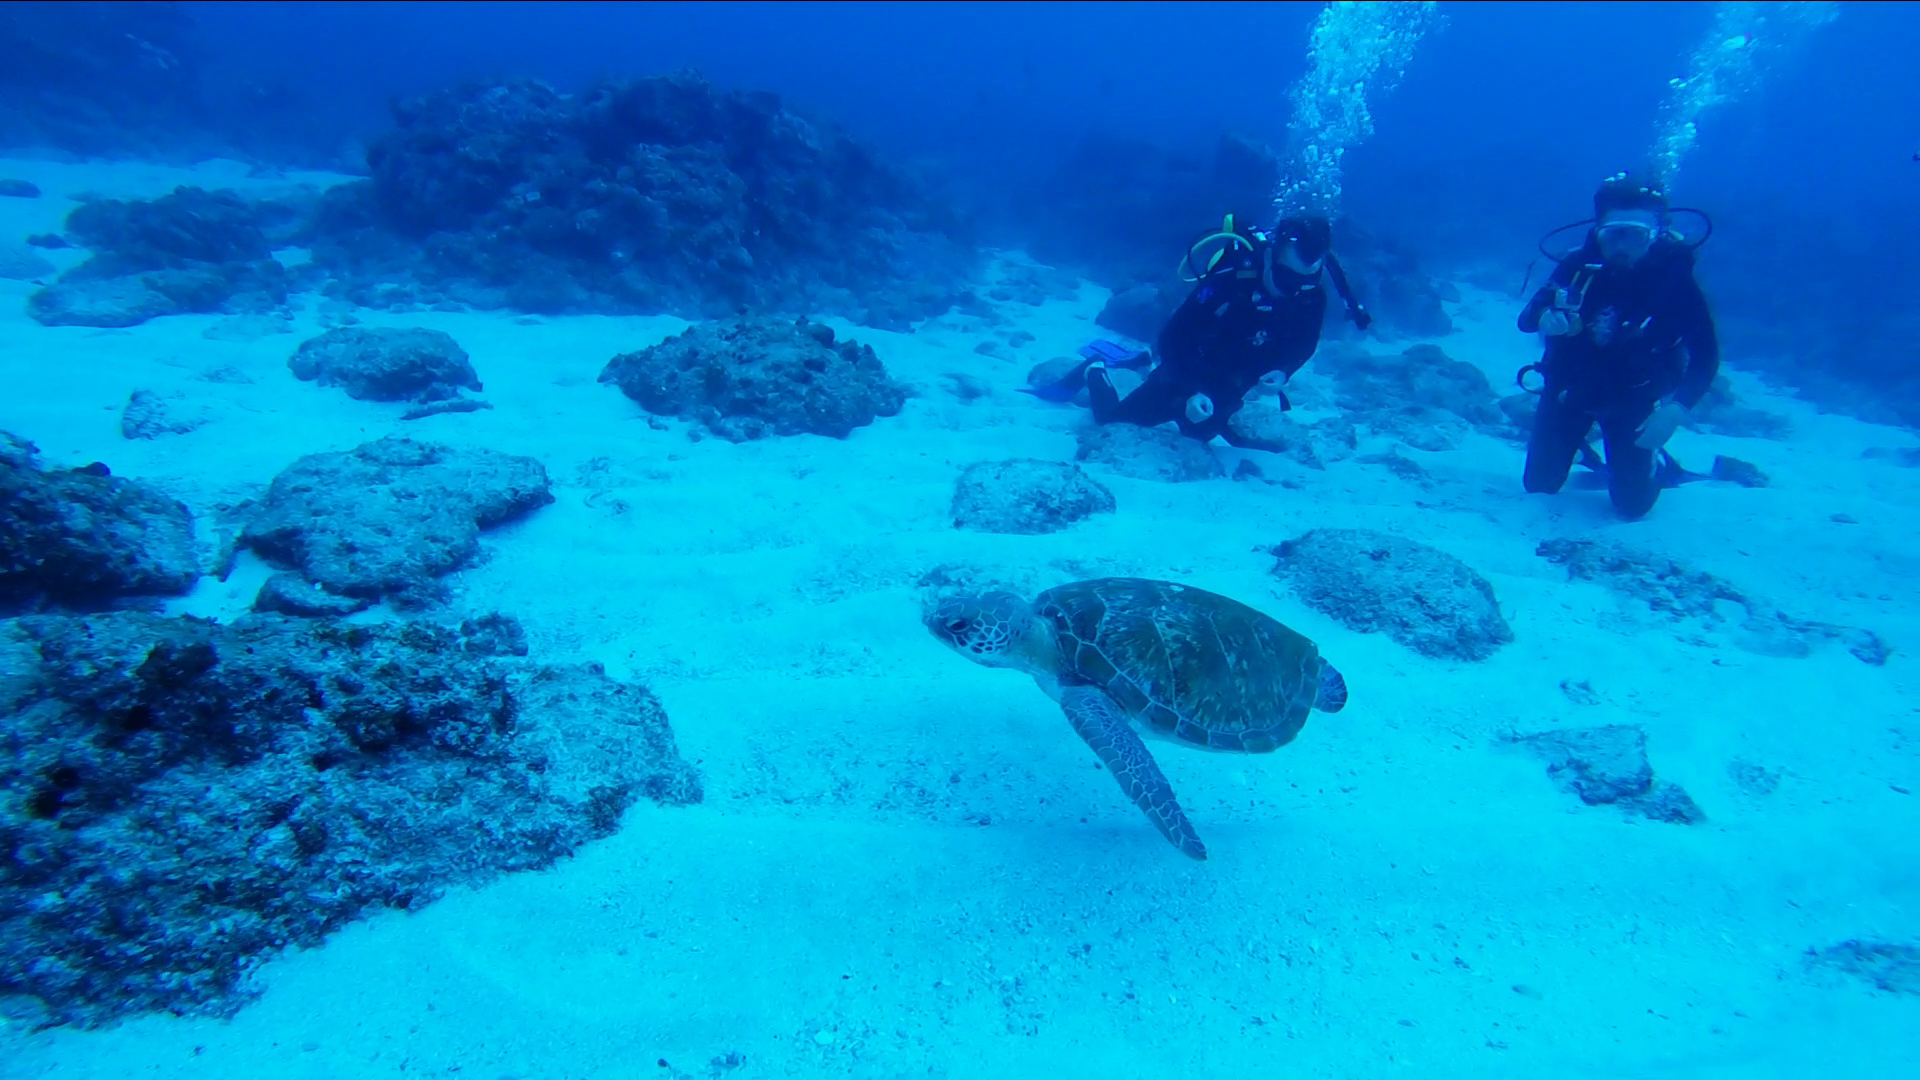
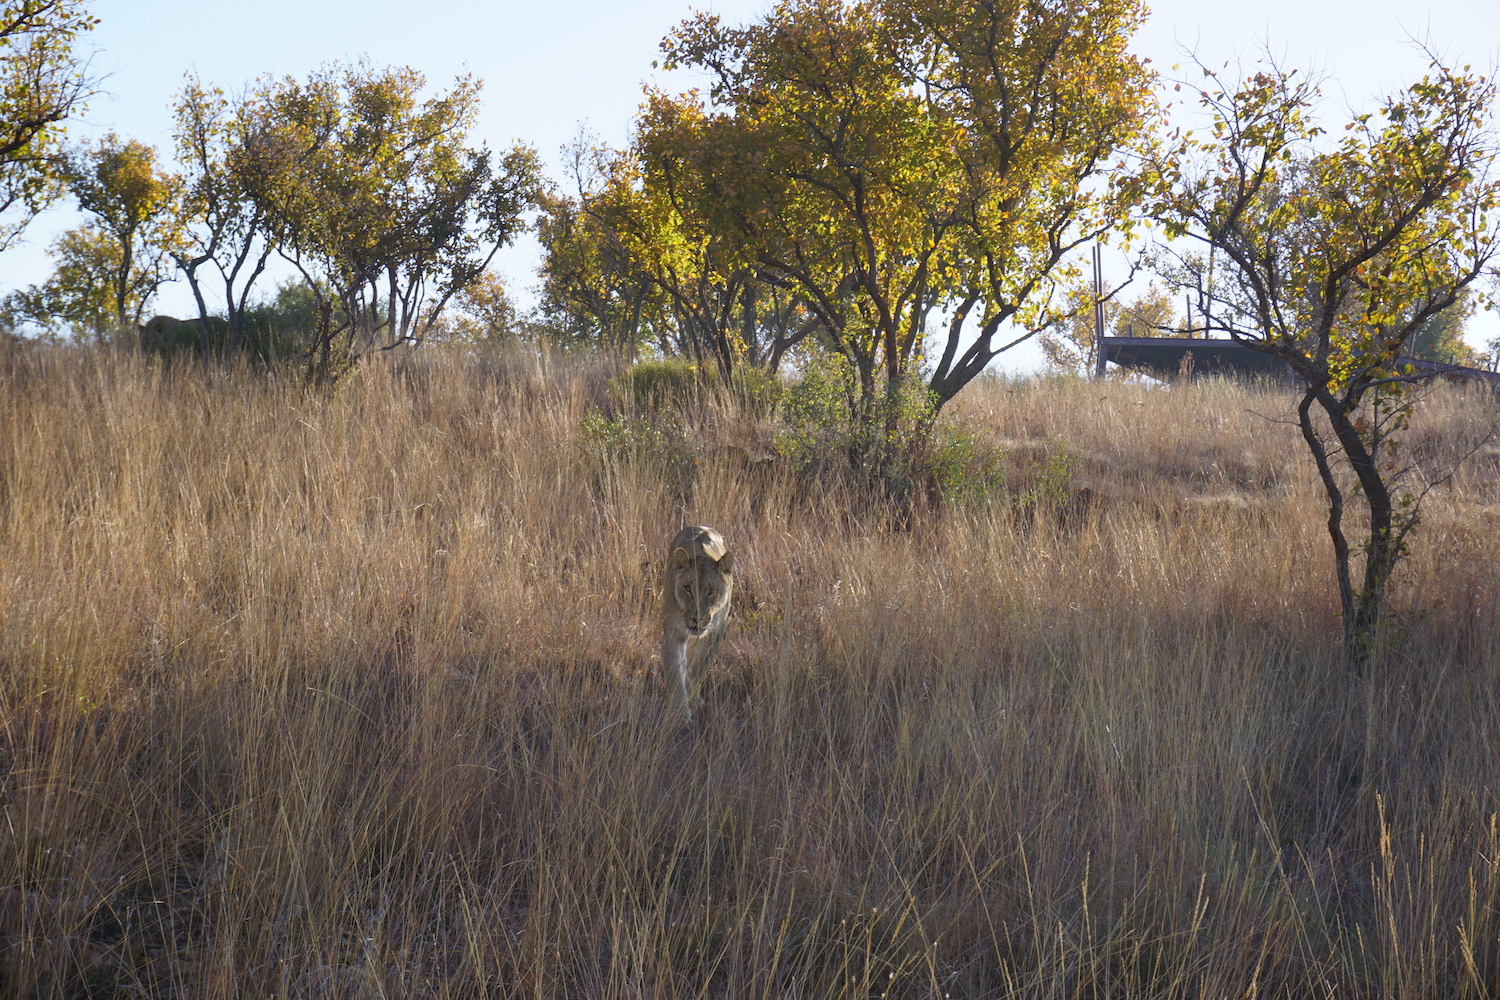
Some more from South Africa. Baby Honeycomb Moray in a rock pool, beach sign, hanging with a green turtle and a lion coming towards us.
-
What're your cookie settings set to in Safari? Can third-party websites read cookies set by other websites?
-
We have many mailing lists with various levels of granularity. However, people aren't great at using the appropriate list and the S/N ratio is a bit rubbish.
-
Krystal.co.uk here (mainly 'cos we're hosting with them too). Alternatively I've used Namecheap without issue.
-
Forgot to mention - after changing the SSH configuration (/etc/ssh/sshd_config) on the server, you'll need to restart the SSH service in order for it to pick up the configuration change. typing service sshd restart as root (or sudo service sshd restart if you're using sudo) should do that. The SSH service might be called something different (ssh, openssh-server), but you should be able to tab-complete the command to find the correct one.
-
tmux is a terminal multiplexer - you may need to install it (it's there by default on Ubuntu). Alternatively you can use "screen" (which I'm pretty sure should be installed on Centos). You SSH to the server, type "tmux" or "screen" and you're then in a pseudo-terminal session (or sessions) that still exists even if the SSH connection drops. screen -r will re-attach disconnected screen sessions. I prefer tmux to screen, but that's mainly because it's got a few more features. For what you're doing (making your working session recoverable if it disconnects), either will do the job. typing man screen will give you more info on usage.