mrbios
-
Posts
4,317 -
Joined
-
Last visited
Content Type
Forums
News
20th
EduGeek EDIT Conference
Blogs
Everything posted by mrbios
-
Two minutes after i typed that thunder started on a more regular basis. I called and Thor listened!
-
This has been such a disappointing day. Weather said thunderstorms from like 11am until 5pm. So far i've heard one rumble and not a drop of rain. I love a good thunderstorm, this has just been one sticky humid cloudy snoozefest of a day.... to top it off i've spent it making DR policies so I could have done with the odd flash of lighning to keep me awake.
-

KCSIE 2023 - updates that may impact IT
mrbios replied to Ditto's topic in Internet Related/Filtering/Firewall
I think I'm achieving this with Senso. Senso flags keywords and phrase detections, and then anything flagged as "Urgent" or "Critical" emails the DSL and he reviews the event which has a corresponding screenshot. Presumably the screenshot covers the needs of the KCSIE without the DSL needing to review an actual website, as they have a screenshot? Actually had an incident the other day where a class were doing something where they had to talk about a subject for 60 seconds, and one girl for example was doing "rape culture" which obviously meant tons of hits to the senso keyword lists. The DSL got so many hits he went to the room and talked to the teacher, the student overheard, and was surprised by the whole thing....but her response was "that actually makes me feel really safe" which i thought was amazing. So wonderful to see the system working as intended, and a student feel protected by it. Only downside is, that monitoring isn't in any way connected to filtering really... -
The ever increasing regulatory burden in education IT
mrbios replied to localzuk's topic in General Chat
Anyone got a TL;DR for the new KCSIE guidance? What's changing from 1st September? (Is there a document that outlines changes only?) -
Had a reply from IAMCloud today, their next-gen client is due out July/August apparently.... sadly that is a little too close to september for comfort for me to depend on that route this year. Worth knowing though for those of you who've known it was "coming" for years.
-
Ah ok i took this line from their CDM page "and with some major upgrades coming in 2023, it keeps getting better." and this from their blog release for 2.15 "Cloud Drive Mapper 2.15 add a number of bug fixes and improvements, and we expect it to be one of the last major stable releases until we move to our new next generation client." I took those to mean this year, we'll see what they say when they reply to my email i guess
-
Thanks Pete, excellent information. I've emailed IAMCloud to ask them about their "next gen" client features and expected release time. Hopefully get some information on that soon, as i type this i've just had an email from burconix as i downloaded their trial yesterday..... need to have a play with it today. Regarding folder redirection, which is likely to take precedence if a GPO exists, the GPO or the settings from the client? Having to sort out my GPOs is likely to be my most frustrating part of the whole process Also i assume even when you use Burcanix/IAMCloud the OneDrive native client is still left there to auto-sign in and show in file explorer, or do you override/hude that in some way to force people to use the mapped drive?
-
What does cloud connect do? Similar to the iAM cloud mapper? or the onedrive mapper script from libensraum? I'm looking at doing a similar thing this year, rather than migrating existing users, just starting from Y7 and overriding GPOs that point to H drive to instead point at OneDrive. Already done a test OU with redirects and it works really well, however one of the CDM/cloudconnect/onedrive mapper tools look like they might solve problems before they arise. Also interested to hear what hurdles other schools have come across with onedrive and what tools have made their lives easier.
-
Playing at 1080p a 3060ti or 3060 would last years playing games pretty much maxed out. My son has my old 3060Ti in his, he plays everything maxed out at 1080p. Prior to that he had a 1060 and that struggled in a few more modern games. DLSS helps too. Looking at a members market on a popular forum i frequent, i can see people selling 3080FE for £400, 3070 for £300 and 3060Ti sold back in April for £240. So definitely don't rule out second hand! EDIT: oh the thread is really old didn't notice the OPs date.
-
Coconnect. Had three horror providers in a row before them, been with them for nearly 6 years now, both times i've been quoted they've been the cheapest, and their support is really good from the experiences i've had with them. They also offer a bunch of other services such as hosted smoothwall etc if that's your thing.
-
Yes. The broadcast module is useless. Thankfully I only have one teacher that uses it, i setup Veyon for that teacher to use broadcast instead. Senso were working on an alternative to their broadcast system but it didn't work out.
-
Domain machines for me. Drivers only install via print deploy for direct print deployments though. I do also deploy a shared print queue (secure print) from our print server still to all staff, but the driver still trys to pull from the server when you deploy that way...... so what i did to get around that was make a fake printer with the same driver as the secure print queue, named it "ignore me" and deployed that if i ever need to update the driver on machines.
-
Personally I'm using papercut print deploy with direct print. However i also include the relevant printer drivers (of which we only have two) in my sccm task sequence.
-
Except for Microsoft putting limitations on Windows 11's minimum CPU requirements, i've never had an issue with a CPU that's 8-9 years old. Not for the kind of things students and teachers do anyway. Obviously it's a gamble on Microsoft not doing the same again with windows 12 and beyond, but i've found i get much better value for money out of them, especially being proper business grade devices, when compared to similarly priced brand new devices (which at that price point tend to be consumer grade) 90% of the devices out of my 600 or so windows desktops and laptops are refurbished, and performance isn't something i ever get complaints about. Obviously YMMV, but we're using adobe creative cloud, kids are playing with Unity etc. For the most part a teacher with a laptop is using office and web browser for the majority of their work, for that a 10 year old CPU will still cope absolutely fine. We're only just getting rid of the last of our Dell E6430's, which used 3rd gen intel CPUs, 3rd gen is 12 years old tomorrow. Now those are quite slow now, but they still fulfil a job at a push.
-
Considered refurbs? The HP Elitebook 840 G5's from ICT-Direct are fantastic. 8th gen, 256gb ssd, 16gb ram. Out of the two you've listed though i'd discount the Asus one straight off the bat. Consumer laptops are atrocious to repair and not as sturdy. I wouldn't go back from business grade laptops now.
-
There's a group policy called: Configure authorized password decryptors Add domain\lapsadmingroupname to that policy. Personally I'm using Lithnet Access Manager, so rather than issuing any users as laps admins, i issued the ams service account (which is a gMSA account) access as a decryptor, and just give users access to the AMS service (linked to azure ad for auth + MFA) highly recommend it as a solution. Does mean you can't access LAPS passwords through the AD tab still, but it's much easier through the web interface of AMS....handy when you're out and about and need to pull up a laps password via your phone for something. (rare but, you never know)
-
Sanity Check For Enterprise E3 Licensing
mrbios replied to cheekycharly's topic in Licensing Questions
E3 = Enterprise, A3 = Education. Just different organization applicability, but the same product essentially. If i remember correctly, you pay for staff FTE with that one and get however many students you want alongside. Seem to remember i was paying for 96 staff licenses when i had EM&S and had 1500 student licenses, but you just pay for the staff side. -
Based on you having "Enable local admin password management: Enabled" that's part of the old legacy laps policies. That policy doesn't exist in the new laps policies. Old Laps is under administrative templates > laps, new laps is under administrative templates > system > laps. No idea how that should look in InTune but presumably that's where your issue is?
-
It'd have its own set of limitations in terms of being able to do advanced print functions, but if you create a secure print queue using the papercut global print driver, that might work? EDIT: unless it is a license issue as above of course..
-
No, no Sophos AV here. Only used for firewall purposes for user identification. Also using RADIUS authentication for BYOD/non-domain wireless clients.
-
So this seems to work, although i need to work out what firewall rule was stopping the collector from working because it wouldn't start serving the firewall until i disabled the inbound firewall on the collector machine.... EDIT: Nvm fixed that one, the guide i was using didn't mention udp 6677 inbound on the collector. I've now got three user accounts for my sophos setup: svc_sophosfirewall - The account the firewall uses to read AD, just a typical domain user, nothing special. svc_sophosagent - The domain admin account used on the sophos agent on the DCs - added this to the protected users group, but you have to do that after saving the service credentials otherwise it moans at you. Looks as though it only talks to the collector via kerberos anyway so shouldn't matter that it can't do NTLM. svc_sophoscollector - An account with local admin on all the desktops. Added to a workstation admins group which is deployed via gpp to all desktops local administrators. I still don't like that this has to be an admin on every workstation but it's got "account is sensitive and cannot be delegated ticked" and im going to added it to deny login locally group. It only needs to be able to be used to read WMI. I think that's about as secure as i can make it. Highly frustrating that none of the guides out there describe this way of doing the accounts though, they all just seem to make one account and make it a domain admin which seems very lazy.
-
Do you currently have Agent and Collector running together from the DCs like i do? or have you separated your agent and collector services? I'm fairly certain it'll be a lot more secure with them separated and separate service accounts for each with the collector not having any domain admin rights. Will let you know how i get on with it next week though!
-
Struggling to find a clear answer to this from anywhere, and all the guides online (of which there aren't many) don't seem to go in to any detail for the part I'm looking for information about...I've emailed sophos support, but their T1 support can take an age to reply, want to sort this out this holiday. I've got Sophos STAS installed on my DCs - Currently running both the Agent and Collector on the DCs. However I've made a new member server setup to move the collector service to. On the domain controllers, the service account running the Agent has to have Administrator or Domain admin rights - it reads from the event log of the DC. The service account that runs the collector service needs to be able to read the remote registry or WMI of every workstation to detect logoff events. (as i understand it) I've got two service accounts: svc_stasagent and svc_stascollector At the moment the svc_stasagent is in the Administrators group and a workstation admins group (which is deployed to all workstations as a member of the local Administrators group) and this works. However i don't like using one account for both, hence splitting them. I plan to add both of these accounts to the security group i have that does "deny local login", add both to protected users group, and tick "account is sensitive and cannot be delegated" any reason any of those would cause an issue? When i try and save the stascollector account on the STAS Collector, if it's a member of protected users i get an error. If i remove it from protected users, save the credentials, then add it back in, the service seems to start fine and as far as i can tell it works. The only issue i've spotted is that with protected users added to the account, the test for "Registry read access" fails, while "WMI Verifications" succeeds. So i presume it'll be fine so long as i use WMI Verification. Any thoughts from anyone who has used STAS on the more secure way of configuring this? Am i on the right track? Or any Wave9 chaps want to chip in? as i know you have a service that helps people set this up.
-
No idea what it costs, but this sounds like a really cool solution that i've been curious about for a year or so now: https://www.starwindsoftware.com/backup-appliance Utilises immutable virtual tapes, or something to that effect, negating the need for physical tapes. Would tick all your boxes though. Make sure you add a cloud target to your backup routine perhaps. Backblaze B2 is super cheap, and easy to setup, we pay <£60pm for about 25TB if i rememeber correctly.
-
Cost of living crisis 2022 - what have you cut back on?
mrbios replied to Ditto's topic in General Chat
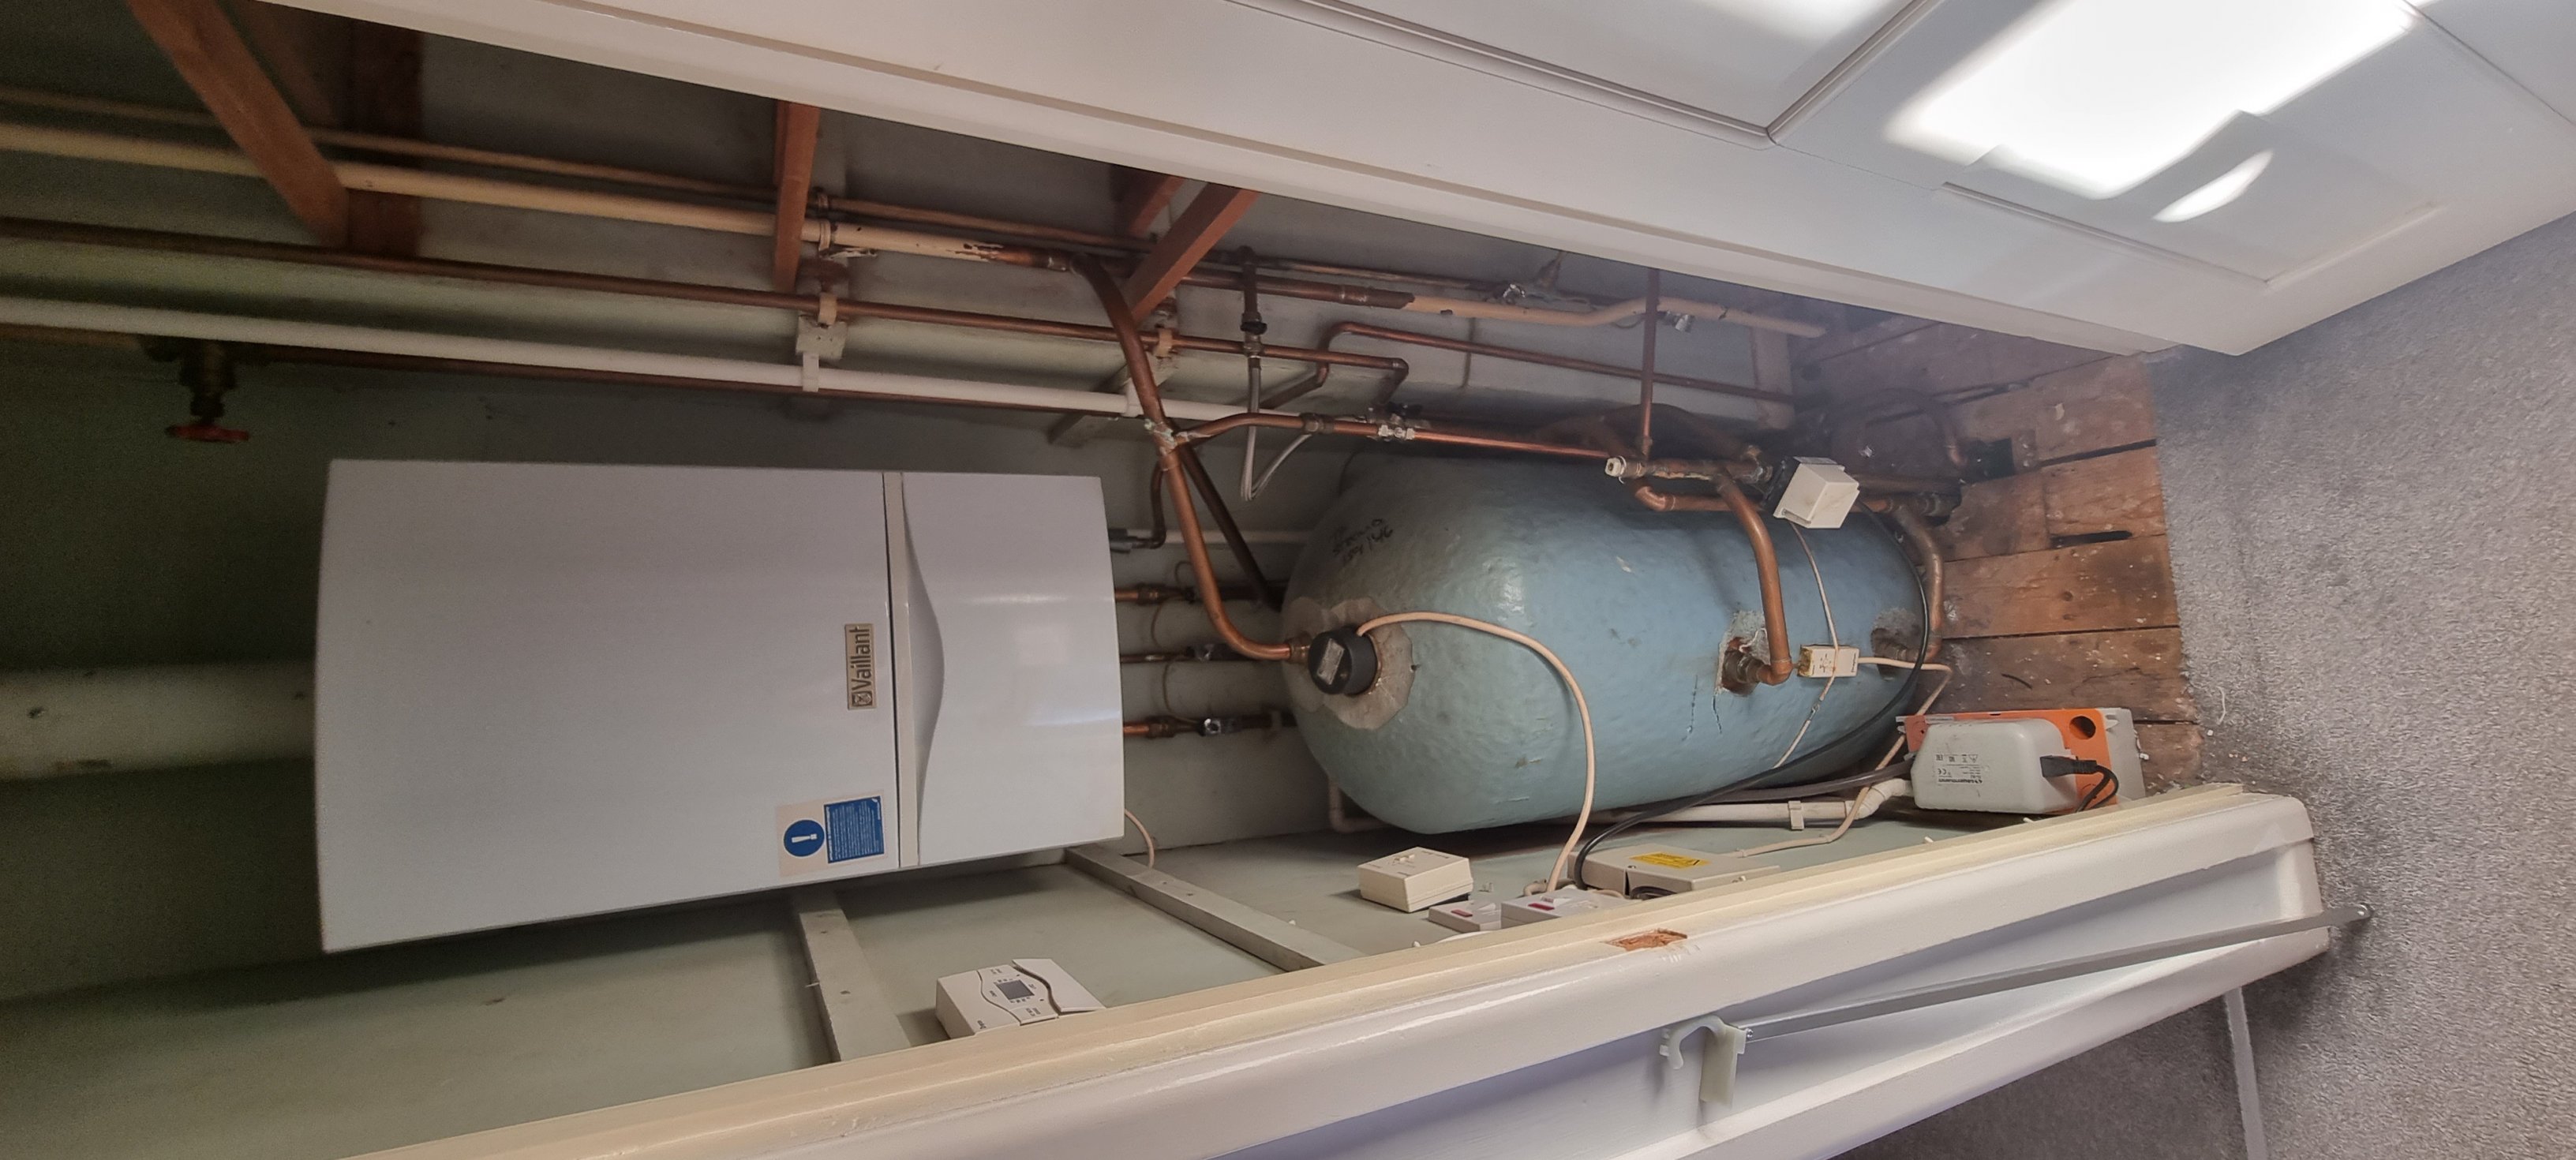
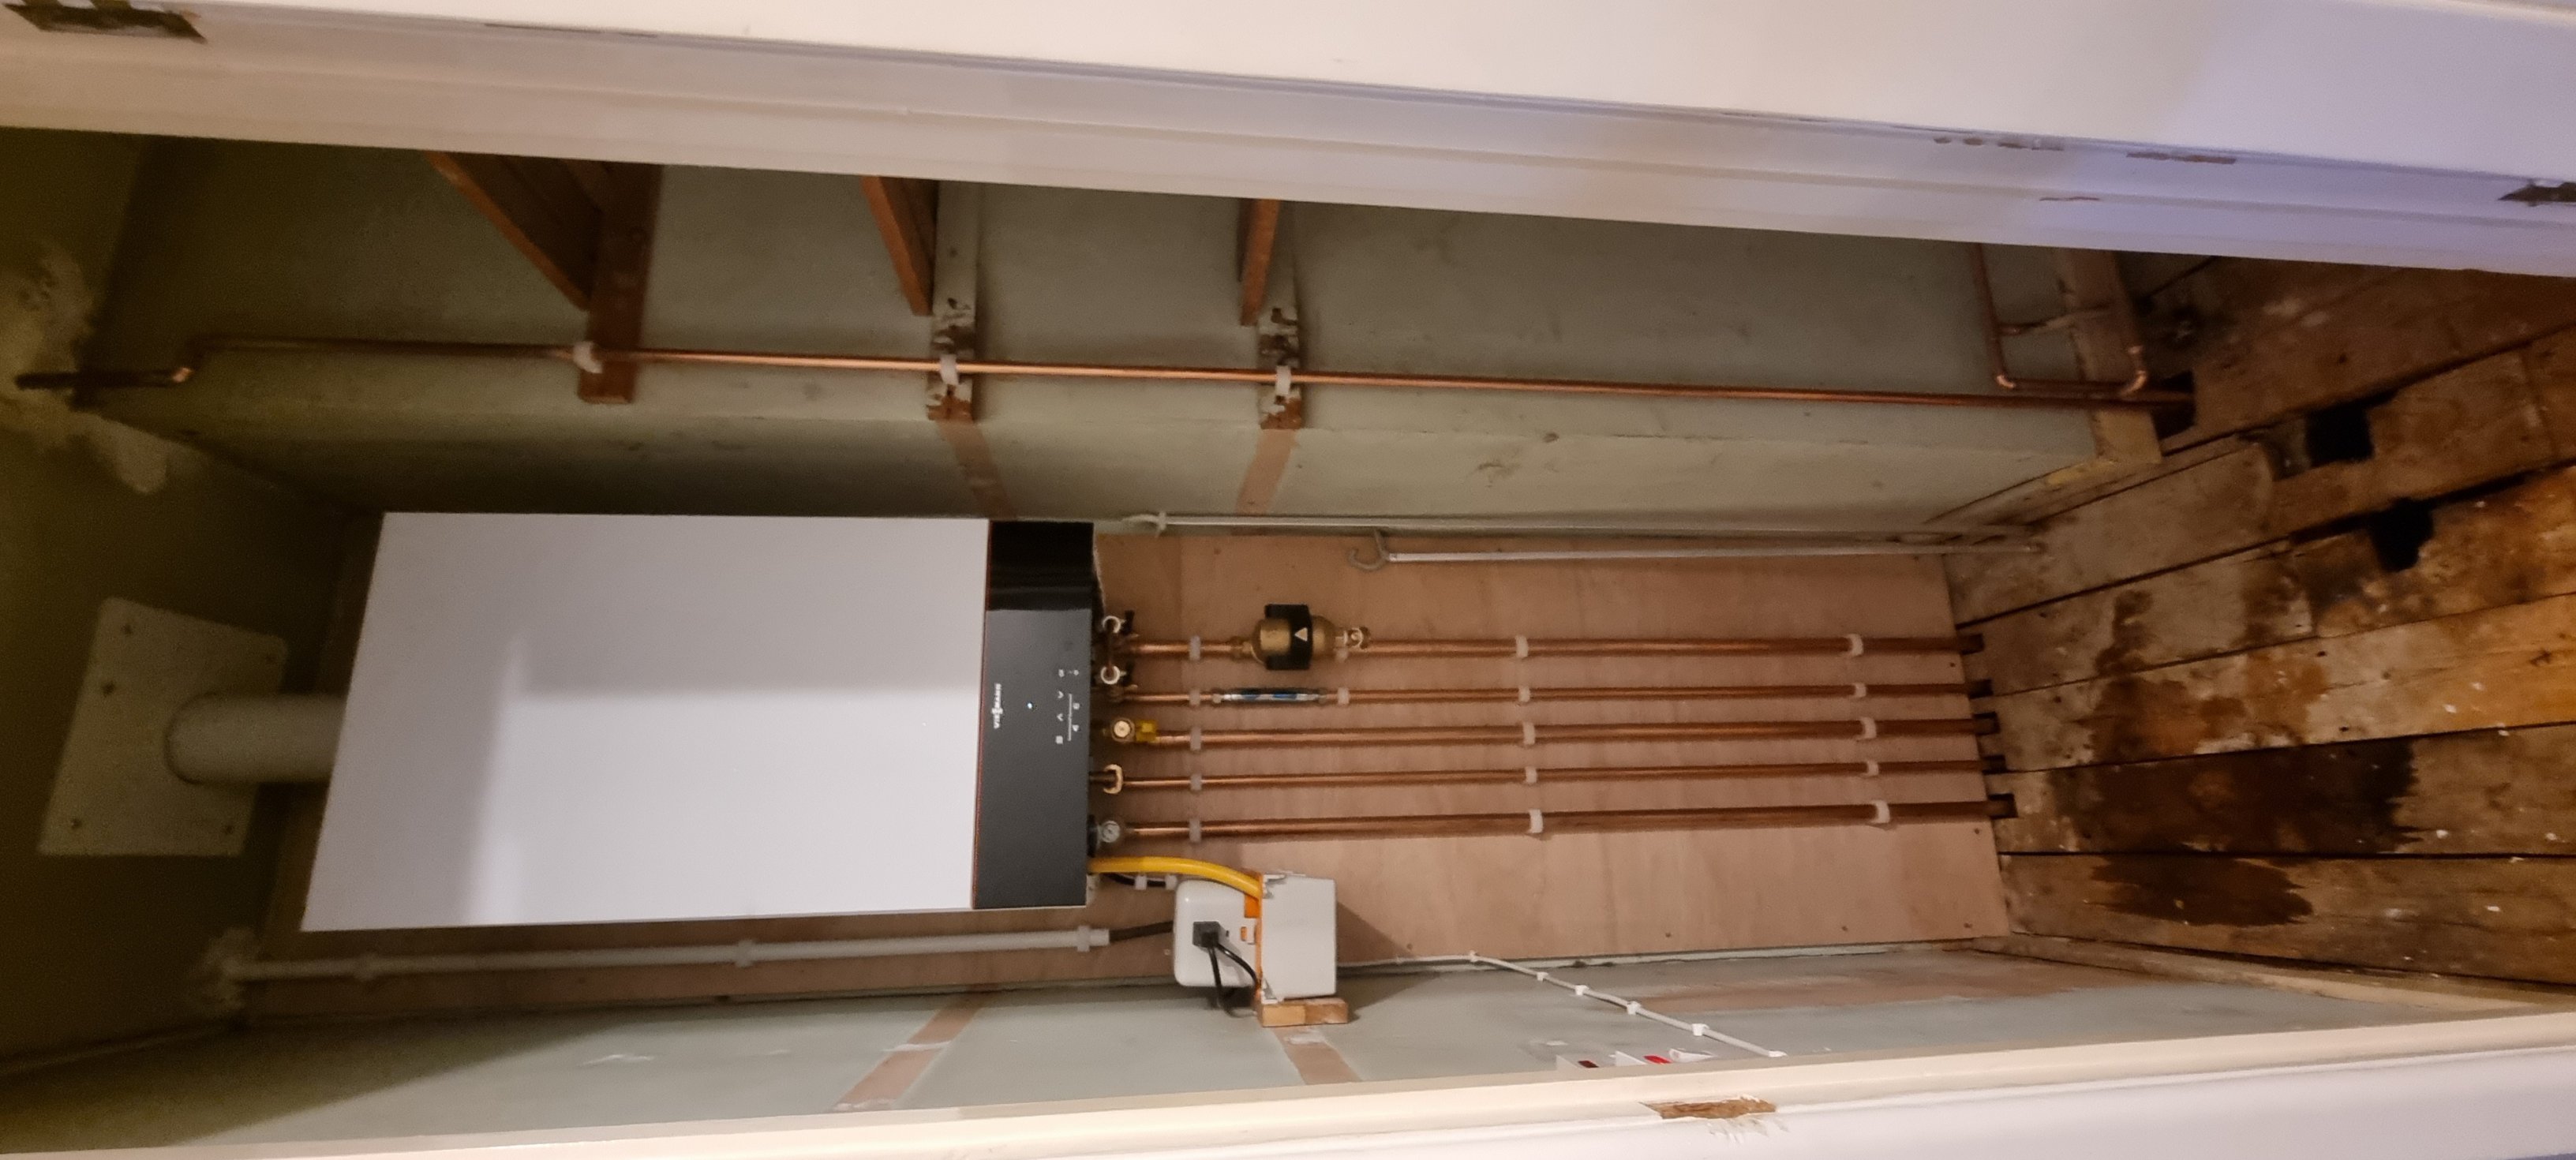
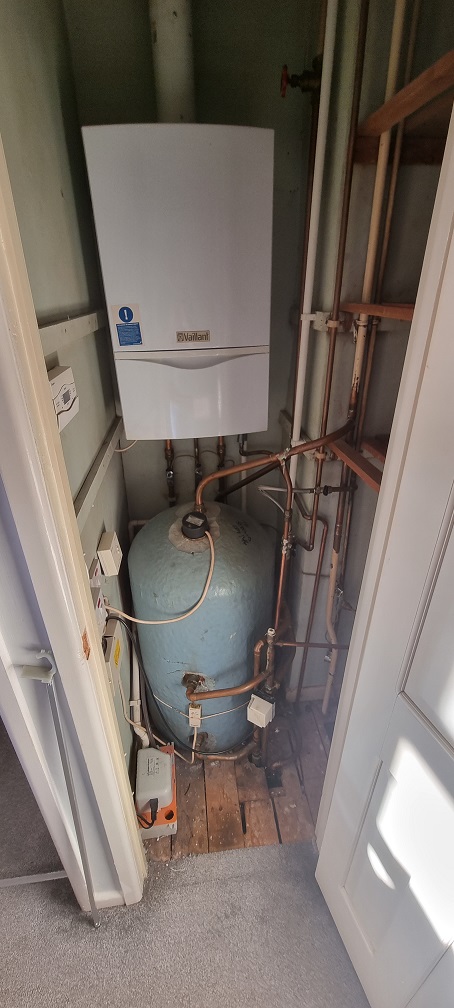
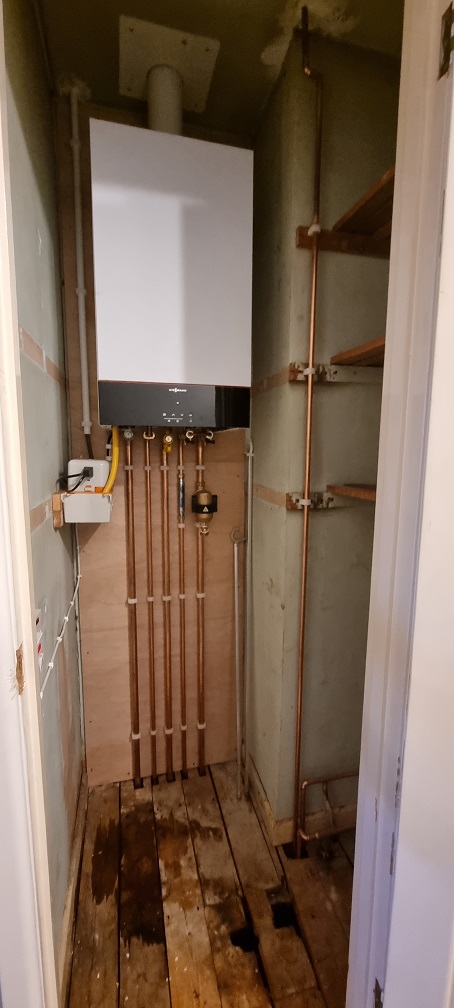
Out with the old (20 year old system boiler): In with the new (Veissman 100W combi): Hopefully that results in a handy energy saving as a worthwhile investment! (I'm aware the airing cupboard is in dire need of a decorating .... bought this house off a HEAVY smoker 4 years ago, it's the last space left to be de-nicotined)