Koldov
-
Posts
5,084 -
Joined
-
Last visited
Content Type
Forums
News
20th
EduGeek EDIT Conference
Blogs
Everything posted by Koldov
-
 Have you made your "new Server 2019 hyper-v VM" a DC at all yet? Someone will correct me if I'm wrong, but I would personally promote it to a DC and get it all replicating nicely for a while, then you can transfer all the roles to it and make it FMSO/PDC, then after another grace period, demote the old one. IIRC once DNS is installed (as creating a DC it will replicate from the original to all DCs) nothing needs to be done to 'transfer it'. I don't think there's much more to it, so it should be relatively straight forward and pain-free. It's been a while since I've done it (and sorry I don't have a list since I basically winged it), the only trouble I had was actually DNS (for the static clients), I couldn't use the previous DC's I.P. address as the new VM DC was on the host which was the original DC (and it was still in service with other roles - I mean I somehow probably could have, but I didn't need extra stress/hassle of an extra thing)!!
-
SIMS > GROUPCALL/WONDE > B2B > LEA
Koldov replied to Koldov's topic in Data Protection & Information Handling
123456
-
Don't know anything about GAM or PS, but I thought bulk changing the password was as easy as uploading a .csv? I'd agree though, disabling/enabling accounts rather than dealing with the aftermath of informing every single pupil that their password has now changed to something else is preferable!
-
Some iPads can join Wifi network, some can't
Koldov replied to Sonic007's topic in Mobile Devices & Tablets
I am probably one of the least 'networky' people on here, so... Can anyone explain what is happening there? Is the iPad actually correct but is it a little over sensitive? Have you run something like inSSIDer to establish what your network looks like (especially near any AP that the iPad can't connect to)? Can you see anything on the WLC about which APs/SSIDs (or hopefully channels) are being connected to by X amount of devices? Running inSSIDer I can see the nearest AP to me shows the following: 3 x MAC ADDRESSES (ending in :A0, :A1 and :A2) 3 x SSID being broadcast (ADMIN, CURRIC and GUEST) CHANNEL: 1 SIGNAL: -50dBm 802.11: a,g,n 2.4GHz Maybe I'm a bit confused by the terminology... Would the iPad saying "Unable to join the network “network name.” This network is operating on Wi-Fi channels in use by several other nearby networks. Restarting your wireless router may allow it to automatically choose the best channel to use, and may resolve this problem." mean that basically as I have 3 'networks' (SSIDs) all being on Channel 1, that is potentially an issue and it might not connect? Would restarting my WLC mean the AP would choose a different channel to broadcast on (if it were set up to detect what other APs around it was using)? Or is it using 'network' or 'channels' to mean the 2.4 or 5 GHz band (seeing as you referenced dual-band)? -
Can't help with OP issue sorry, but am interested in why you aren't using SOLUS to deploy to clients? I have a few off-site clients that can never access SOLUS (and so never update) but can VPN in to the network, I wonder if your solution can help me get around this limitation.
-
Can't help with your current situation OP, but for the future I'm sure I've seen on here various versions of hiding addresses (think it was students > teachers but might be possible the other way round). Or at least stop it auto completing addresses or something along those lines, so that if a teacher wants to email a Year Group/Student, they have to manually type in the address? Others more versed in Google will be able to help with this and the original issue regarding a Google version of the O365 tools I'm sure. With the drama this has caused I'm sure it shouldn't be too difficult to get SLT onboard to make any changes you need!
-
Hopefully if you've gained a certification in a subject you should be able to complete the 'technical' task with the knowledge gained from the qualification, but yeah, can be interesting if you've never actually physically done the thing you've studied (and got qualified/certified for)! Because it's all great in theory, but.... No Plan Survives First Contact With the Enemy!!! Not sure I'd agree with the sheep analogy, but certainly a lot of exams only seem to prove that you are able to absorb, retain and then regurgitate information rather than actually 'understand' it. Sometimes that's not a bad thing, I'd like to be able to retain a lot more information than my brain currently allows me to! Of course I have the 'experience' to be able to obtain it (thanks EDUGEEK/Youtube/the internet!). Actually even worse are degree/coursework exams that rely on submissions being created under no external scrutiny (as some on here freely admit, this can be accomplished just by copying something from a book/on-line and rewriting it in your 'own words' or having AI do it for you). Then of course there are the degrees that have zero application in the real world (but at least you got an 'ology.... dating myself there for those of you old enough to understand). Educated fools (a favourite saying of my Grandfather), although I've heard a more derogatory version too (also 'got a degree, but can't boil an egg' etc.)**. I've said on here before that I used to work in the office (stock control/inventory dept.) of a large distribution warehouse after working my way up from doing many years of hard graft on the shop floor. To progress in your career, that is the way it was done, hard work/experience/provable aptitude. From warehouseman, to supervisor, to shift manager, warehouse manager etc. At one point however they decided that they would stop that progression and only hire warehouse managers, that instead of having many years experience in logistics warehousing/distribution and managing a shift of 30 warehouse staff, just had a degree... I can't tell you how many problems that caused. I seem to recall the police have some sort of 'accelerated detective' program for degree graduates too - this also calls into question what part 5, 10, or 15 years of experience on 'the beat' is now NOT being brought to the role... **Maybe it's something to do with being in education from the ages of 5 - 20+ (this might explain teachers, who never actually leave it)...
-
It is an interesting observation though ("gained through many years of educational I.T. experience" apparently)... As I've said in my previous post, I gained my role from a very similar situation as described there, with the exception that they had minimal 3rd party support (although by the standards set out, I appear to be not much better). Hopefully someone more 'qualified' (see what I did there...) could create a poll, so we can (anonymously) ascertain the amount of 'professionally certified/qualified' employees in the educational I.T. sector and who knows, we may even prove them right... but regardless of the reasons behind it (lack of school funding/lack of employers knowledge of the I.T. field/lack of importance given to I.T., which has and will continue to be discussed in other threads), I for one would be interested in the results. I would vote first (and don't care who knows it) as 'Legacy Qualification'... Maybe we can shed some light on at least the current situation (and not what the educational I.T. sector was in years gone by) instead of vilifying the poster for their observation? What 'qualifies' you for your current role/position/employment (also applicable to those who aren't currently employed but held the role previously), something along these lines...? 1. Absolutely zero 'professional' qualification (but I like computers) 2. No 'professional' certification/qualification but experience in a similar/comparable role (or previous junior tech/apprenticeship) 3. Legacy certification/qualification (should be I.T. related, but not necessarily applicable to the role) 4. Full & current qualification for all aspects (or at least the majority/main part) of the job.. I mean is there a qualification for changing toner...? But seriously if you are a full on Google school (or totally Microsoft) do you have a certified qualification from that provider. Obviously I'm not going to be able to quantify all aspects of previous qualification/experience... Also I have purposefully left out anyone currently studying towards, as although this is important (and may even be a condition/benefit of your employment) it does not 'qualify' you for the role, which is the actual subject in question.
-
Calling @PaddyNewman ...
-
I guess it depends on what involvement you have with the Wonde platform and what you use it for. It doesn't do a great deal for us apart from transfer pupil's details to a cloud learning platform so they have a user account. We were asked to just download and install the WondeSIMSInstaller.exe (although iirc it did have a 'license' key) and the program sits on the server and does just that, we have no other interaction with Wonde. Is your situation like that? I'm just wondering what could have prompted them to email you a demand for payment?
-
Grabs popcorn (and hides 11 year old Comptia A+ certificate)... Everyone really only ever sees things from the veiwpoint they're standing at... but it's safe to say you've got a lot of experience to frame your perspective, so in that way it's a valid statement and as you say, you are obviously entitled to your opinion (what's the saying? It ends something like 'everyone's got one')... It's easy to have a knee-jerk reaction to an apparently insensitive, broad brush stroke comment like that on a forum that caters for those that spend their career working hard to do a good job in educational I.T. Maybe it's a little too close to the bone for some of us, honestly though, I can see both sides to this. I do agree managing a modern school network these days isn't 'really' a job for an amateur (for want of a better word) and I have to admit (as a 'one man band') that having a good 3rd party support team or MSP with the in-depth knowledge of their specialist staff who get regular up to date training on new technologies can be invaluable to some schools (especially those that don't invest in their in-house I.T. support's professional development). There's been plenty of times I wished I had that kind of support, but I've had to ask on here at EDUGEEK, Google something, look at a YouTube video... but for the vast amount of things I have to look after, I wonder if I'd ever have the time to get 'qualified' (and remain current) in everything I have to do (if there is even a qualification for pulling some strange, unknown goo out of an iPad charging port - I jest but it's happens and you know what I mean).... So, even though I've been running this school network for nearly 12 years, going by your standards, I'd have to consider myself an 'unqualified/amateur/imposter', sack myself and tell the school they're better off getting an 3rd party/MSP (or at least employ someone who has got qualifications)... I don't have a lot of experience about how other school's I.T. support works, I've only ever been in one school (and this was a long time ago, although I'm sure it still happens) but I did take over from the Site Agent (actually Caretaker in those days), who had an 'interest' in computers, an I.T. co-ordinator who wasn't particularly I.T. literate and a professional 3rd party support company (half a day, once a week - that never managed to get to the end of the 'issues' list in the time they had, let alone do preventative maintenance (or any of the 'too many to list' jobs I do everyday) etc... But they decided to employ me based on a lot of factors, possibly not relating to my *cough* qualifications *cough* (obviously it was my good looks and winning personality), because really what do they know about I.T. qualifications anyway (and would they have been able to afford the other guy with every cert going? Did he have any experience? Was he going to engage and be part of the school? Or even stay for very long if he got the job?). An average school Head wouldn't know an A+ from a Computing Degree (and actually in a school I know which is more useful)... In that respect a 3rd party support company or MSP would have done all that legwork along with ongoing training, so it has its advantages but I guess the point I'm trying to make is there are very few jobs in the real world that are purely about qualifications. My BM's OH works in a school that has a full time 3rd party support company and they say the 'I.T. guy' (who the 'company' say is very well qualified), was an absolute a$$ that nobody liked, so they got rid of the company... still, that's only one perspective obviously... EDIT: (yes, there's more) Server NT and Windows 2000 may seem 'simple' to you now, but I'd argue it actually took a fair bit more knowledge to keep those systems up and running than the more modern ones (and there were was little information from Google/Youtube videos/Internet forums on how to do it back then either)... EDIT: For the actual OP, Windows is 'suitable' for education, but I think it's less 'necessary' and it depends on your use case scenario and how much of your learning is platform independent (cloud based etc.). I'm afraid I'm a little old school if you'll excuse the pun and say that for the vast majority of current employers, knowing how to use Windows whilst possibly not being a deal breaker could be an advantage. The same for other large well known software suites used in offices/music production/graphic design (although I know a few will disagree and say a spreadsheet is a spreadsheet)... I've used various music and graphic/video editing tools over the years, but the first time I sat down with something professional like Logic, Photoshop, Premiere, it took me longer than I care to admit to do the simplest of tasks... that wouldn't be a good look for a potential employee... Don't get me started on how long it takes me to research the Headteacher's MacBook issues...
-
[closed] bug/error: HUGE banner won't dismiss
Koldov replied to Norphy's topic in EduGeek.net Site Problems
I couldn't close it with the bottom left 'remove this notice' X, but there was a top right X that did the job! EDIT: Sorry didn't see it was a 'closed' thread, you might want to lock it...? -
SIMS > GROUPCALL/WONDE > B2B > LEA
Koldov replied to Koldov's topic in Data Protection & Information Handling
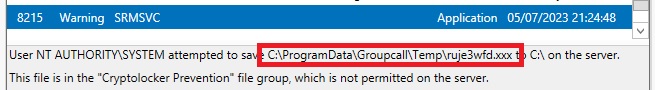
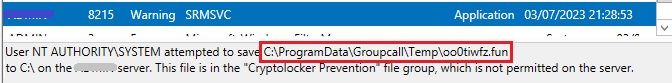
Yet, another 'random' file extension from Groupcall... and yes, I know that the fact it's random means it can actually be anything (even real words or well known Cryptolocker virus extensions) but this is the only software we have that gives me a heart attack on a regular basis! "This is an article that provides specific details on .fun files virus infection. After the detection of several Jigsaw ransomware iterations this month other three versions of the ransomware has been spotted in active attack campaigns. They are all associated with the extension .fun and as typical data locker ransomware all aim to blackmail victims into paying a ransom for decryption of valuable data." "What is the Fun virus? Fun virus is a variant of Jigsaw ransomware that encrypts files, adds the .fun file extension to the end of the file name, and downloads a ransom note on Windows Desktop and in every folder it encrypted files in." What is Jigsaw ransomware? Jigsaw is ransomware that uses the AES algorithm to encrypt various files stored on computers. After encryption, this ransomware displays a window with a message listing the encrypted files and stating that victims can only restore them by paying a ransom. In addition, every sixty minutes, .Fun deletes a certain number of files, thus, putting victims under pressure to pay, since delays result in permanent deletion of more files
-
A slightly more 'manual' way (if it's Excel).... A long (really long) time ago when I used spreadsheets a lot, the way I used to compare lists was with a VLOOKUP, but it doesn't 'automatically' resolve any errors, just errors on them, although there might be a better way now as I think there's new 'lookup' functions. I've tried a while ago as well, comparing the children in SIMS with those in Google and then in Adobe (just to make sure all pupils on roll had those other accounts created), but it was such a pain with legal first/last name vs. preferred first/last name I abandoned it. This calculation 'looks up' the value of the cell E6 in the list B4 to B6 and if it matches exactly returns the value else #N/A: =VLOOKUP(E6,B$4:B$6,1,FALSE)
-
I've just found this post from @BKGarry ... http://www.edugeek.net/forums/office-software/233557-solved-outlook-opening-links-edge.html So, I'm trying this to see whether it will force Outlook to use Chrome and ignore whatever issue is trying to get me to install Edge... EDIT: Probably just an(other) Outlook 2016 issue as I have 2021 installed on my machine (and can't find the settings in Outlook mentioned in that thread). Also, I just sent an email with a link and that opens in Chrome, even though I don't have that GPO set (or the Outlook settings mentioned) and I do have Edge installed as well...
-
Just wondering if there was any setting to separate out any parts of Windows Update using WSUS. I've used WSUS for years and am very happy with it, but I've recently had to install Edge and notice that WSUS gets updates for it almost every other day (also it's not fine grained enough to set it to ignore Dev/Beta/Extended Stable versions let alone ARM andx86 versions too - a bit like I wish I could only set it to get updates for the Windows version we use) so it just means there's an additional management overhead declining/sorting. I could set them to automatic approval, but it still means all the other versions clog up the WSUS console. I had the same issue with Defender (multiple definitions per day) so I have that set to automatic (the only category that is), but as that's Anti-Virus I'm OK with that. I just found that without it set, the other 'general' Windows Update settings (wait to update) seemed to stop it installing, plus I'd have to approve and I thought they needed to be more up to date than just whenever I had time. Does anyone know if I don't manage Edge through WSUS (but still manage Windows Updates through WSUS) is it separate enough to find it's own updates? I mean Edge knows that 'Updates are managed by your organization' (sic), but is that taking it's cue from the fact that Windows Updates are done by WSUS or that I have added the category (so if I took the category out of WSUS would Edge update itself)? Just as a bit of clarification I only use WSUS to 'manage' updates, but it does not download or store them. I have it set so although I can approve/release/recall updates the actual files are downloaded to directly to the machines from Windows Update.
-
I'm going to presume that was also through Chrome? Installing Edge to see if that makes a difference, but I don't really want to as I don't need another browser to configure and secure. EDIT: Sorry just re-read that and if you're 365 maybe you were using Edge, so could be pointless installing it if I'm going to get the same message because it isn't 'really' a problem with an out of date browser and it's just a generic error message because some link isn't getting passed through properly for some other reason.
-
I'm sure something similar has been posted before (specifically I seem to recall one about another thread, 'Netbooks, PDA and Phones' or at least include iPads**) but there was some reason or other it couldn't be done. Don't know if anything has changed now. **other tablets devices available
-
My BM has just asked me what's going on with the emails this morning... but I'm getting all of mine OK so asked them to send a screenshot. Just as a bit of background, this is a legacy email account 'manged' by the LEA, so I don't have any visibility of it or its settings. There is one for the Admin and one for the Head and we have had them for years, we don't use them in general for the majority of staff day to day, but the Admin and Head are still used and they are the two on the website and letters that are sent home, compliment slips etc. They are trying to access the account via Outlook (Office 2016) and I'm guessing this is modern auth or whatever it's called and it's trying to https to an auth page, but the 'browser' is Chrome and it is up to date...
-
Why wouldn't it? SIMS doesn't look or feel like it's had any major update since about 1994 (and it probably hasn't), so it will possibly still work in another 15 years...
-
Also, just to mention the old tried and trusted saying: 'when was it last working, when did it stop working, what happened inbetween?'... Are there any issues about the method used to enter the information in the proxy address field? This might be outdated, but I found this (translated from the original German): https://www.msxfaq.de/exchange/admin/proxyaddresses.htm "You can access the "ProxyAddresses" field in the expanded view via the "Attribute Editor" tab, which is highlighted in green. However, you should definitely refrain from such changes if, for example, Exchange is installed in your environment. The corresponding commandlets from Exchange as well as Skype for Business ensure, for example, that... ... mail addresses are unique and The Active Directory itself does not check whether the address has already been assigned to another object ... mail address is "valid" Mail addresses may only contain certain characters. Everyone will understand that eg two "@" are not allowed. But a period at the beginning or end of the user part is also not allowed. ... Mail and the primary proxy address match The two fields are not linked by the domain controller. Exchange ensures that the primary SMTP address from the ProxyAddresses is also maintained in the "Mail" field without the leading "SMTP:". ... only "Accepted Domains" are used Exchange is responsible for certain SMTP domains and it only makes sense to create email addresses for these domains SIP addresses for voicemail are maintained Skype for Business adds the SIP address with the prefix "SIP:" so that the voicemail works. You would have to implement all these and other checks in your own code if you really didn't want to use the Skype for Business and Exchange commandlets. Irrespective of this, direct modification of Exchange Properties is not supported by Microsoft." HTH
-
There must be a way... Not on a DC at the moment, but is there a way in AD that you can tell at what time an attribute was changed or an account was updated? EDIT: Found something... Would this work? "Each Active Directory object has an uSNChanged attribute that corresponds to a directory-global USN (Update Sequence Number) object. Whenever an Active Directory object is created, modified or deleted, the global sequence object value is increased, and the new value is assigned to the object's uSNChanged attribute."
-
Sorry, don't have an answer for you but are you saying that your AD accounts are automatically created from SIMS by Xporter/IDaaS, then when you 'manually' add an attribute to the user in ADUC, it is then changed/overwritten/deleted overnight (I presume when Xporter runs)? I'm also presuming there isn't there an equivalent field in SIMS that you can populate and have the export fill it for you, so best guess is maybe Xporter/IDaaS is rewriting that field with a blank as it doesn't have the information (bit of a stretch, but might be worth looking at as a possibility)? Maybe something in Azure though, this isn't something I know anything about and you're obviously well up on me, so I'm not trying to 'teach you how to suck eggs', but it seems there's a lot that can go wrong with populating that field and it has a few 'gotchas' and it looks like it won't take much for it to be dropped: https://learn.microsoft.com/en-us/troubleshoot/azure/active-directory/proxyaddresses-attribute-populate "The proxyAddresses attribute in Active Directory is a multi-value property that can contain various known address entries. For example, it can contain SMTP addresses, X500 addresses, SIP addresses, and so on. When an object is synchronized to Azure AD, the values that are specified in the mail or proxyAddresses attribute in Active Directory are copied to a shadow mail or proxyAddresses attribute in Azure AD, and then are used to calculate the final proxyAddresses of the object in Azure AD according to internal Azure AD rules. The logic that populates mail, mailNickName and proxyAddresses attributes in Azure AD is called proxy calculation and it takes into account many different aspects of the on-premises Active Directory data, such as: Set or update the Primary SMTP address and additional secondary addresses based on the on-premises ProxyAddresses or UserPrincipalName. Set or update the Mail attribute based on the calculated Primary SMTP address. Set or update the MailNickName attribute based on the on-premises MailNickName or Primary SMTP address prefix. Discard on-premises addresses that have a reserved domain suffix, e.g. @*.onmicrosoft.com, @*.microsoftonline.com; Discard on-premises ProxyAddresses with legacy protocols like MSMAIL, X400, etc; Discard malformed on-premises addresses or not compliant with RFC 5322, e.g. missing protocol prefix "SMTP:", containing a space or other invalid character; Remove ProxyAddresses with a non-verified domain suffix, if the user is assigned an Exchange Online license. Therefore, the values of the Mail and ProxyAddresses attributes for the object in Active Directory may not be the same as the values of the ProxyAddresses attribute in Azure AD" HTH
-
Just recently had the mobile carrier switch over from 'Virgin' to 'O2'. Seems to have gone smoothly... Unlike Virgin email (which I've had since the NTLWorld days), don't know if anyone has had the same, but apparently they've had some sort of catastrophic failure in their hosting servers (or have been hacked and are not admitting it) and although initially lost all email function. They have now restored send/receive functionality, however seem to be having quite a bit of trouble restoring access to a number of user's historic emails... Luckily for me it isn't a major problem as for years I've only kept it due to it being tied to the account for T.V. & broadband and don't actively use it.
-
[ipad] Guided Access password set on iPad
Koldov replied to Koldov's topic in Mobile Devices & Tablets
I did some more research on this and found that in actual fact.... everybody is right! Seems to be a bit hit and miss, which is why sometimes it works and for others it doesn't as I actually did notice that on some attempts it did turn off Guided Access on a reboot.... But for some reason I couldn't reproduce it every time, so thought I had just missed a step, or hadn't set it correctly. However, it appears from my testing at least, for most of the time it can work depending on how 'Guided Access' has been enabled: 1. Settings > Accessibility > Guided Access Toggle on Then 'Set a Passcode' Open an app Then tap home 3 times Guided access starts with no further interaction Hold power and home button until iPad restarts. On restart the message is displayed 'Guided Access Started' Result = Guided Access still active --------------------------------------------------------------- 2. Settings > Accessibility > Guided Access Toggle on DO NOT 'Set a Passcode' Open app Then tap home 3 times Choose to start Guided Access and enter the required a passcode. Hold power and home button until the iPad restarts Result = Once the iPad starts it asks you to 'Set Passcode' once cancelled Guided Access is no longer active (but is still toggled on in settings). So much for all that... I've just tested the 2nd option again and on the first reboot 'Guided Access' was still active, then only on the next reboot it came up with 'set a passcode' and the option to cancel out... Anyway, I haven't got time to investigate any further and it seems pointless as I now know to reboot first and if that works great, if not it is turn 'single app mode' on and then off. But, if a reboot works then 'Guided Access' will still be toggled on in the settings and only requires a child to 'accidentally' hit the 'Home' button 3 times and enter a passcode... If a reboot doesn't work then the 'single app mode' route also toggles this setting off.