Davit2005
-
Posts
5,320 -
Joined
-
Last visited
Content Type
Forums
News
20th
EduGeek EDIT Conference
Blogs
Everything posted by Davit2005
-
Yeah hard to say but judging by the media report and hesitancy to click any links in txts I'm not about to test it.
-
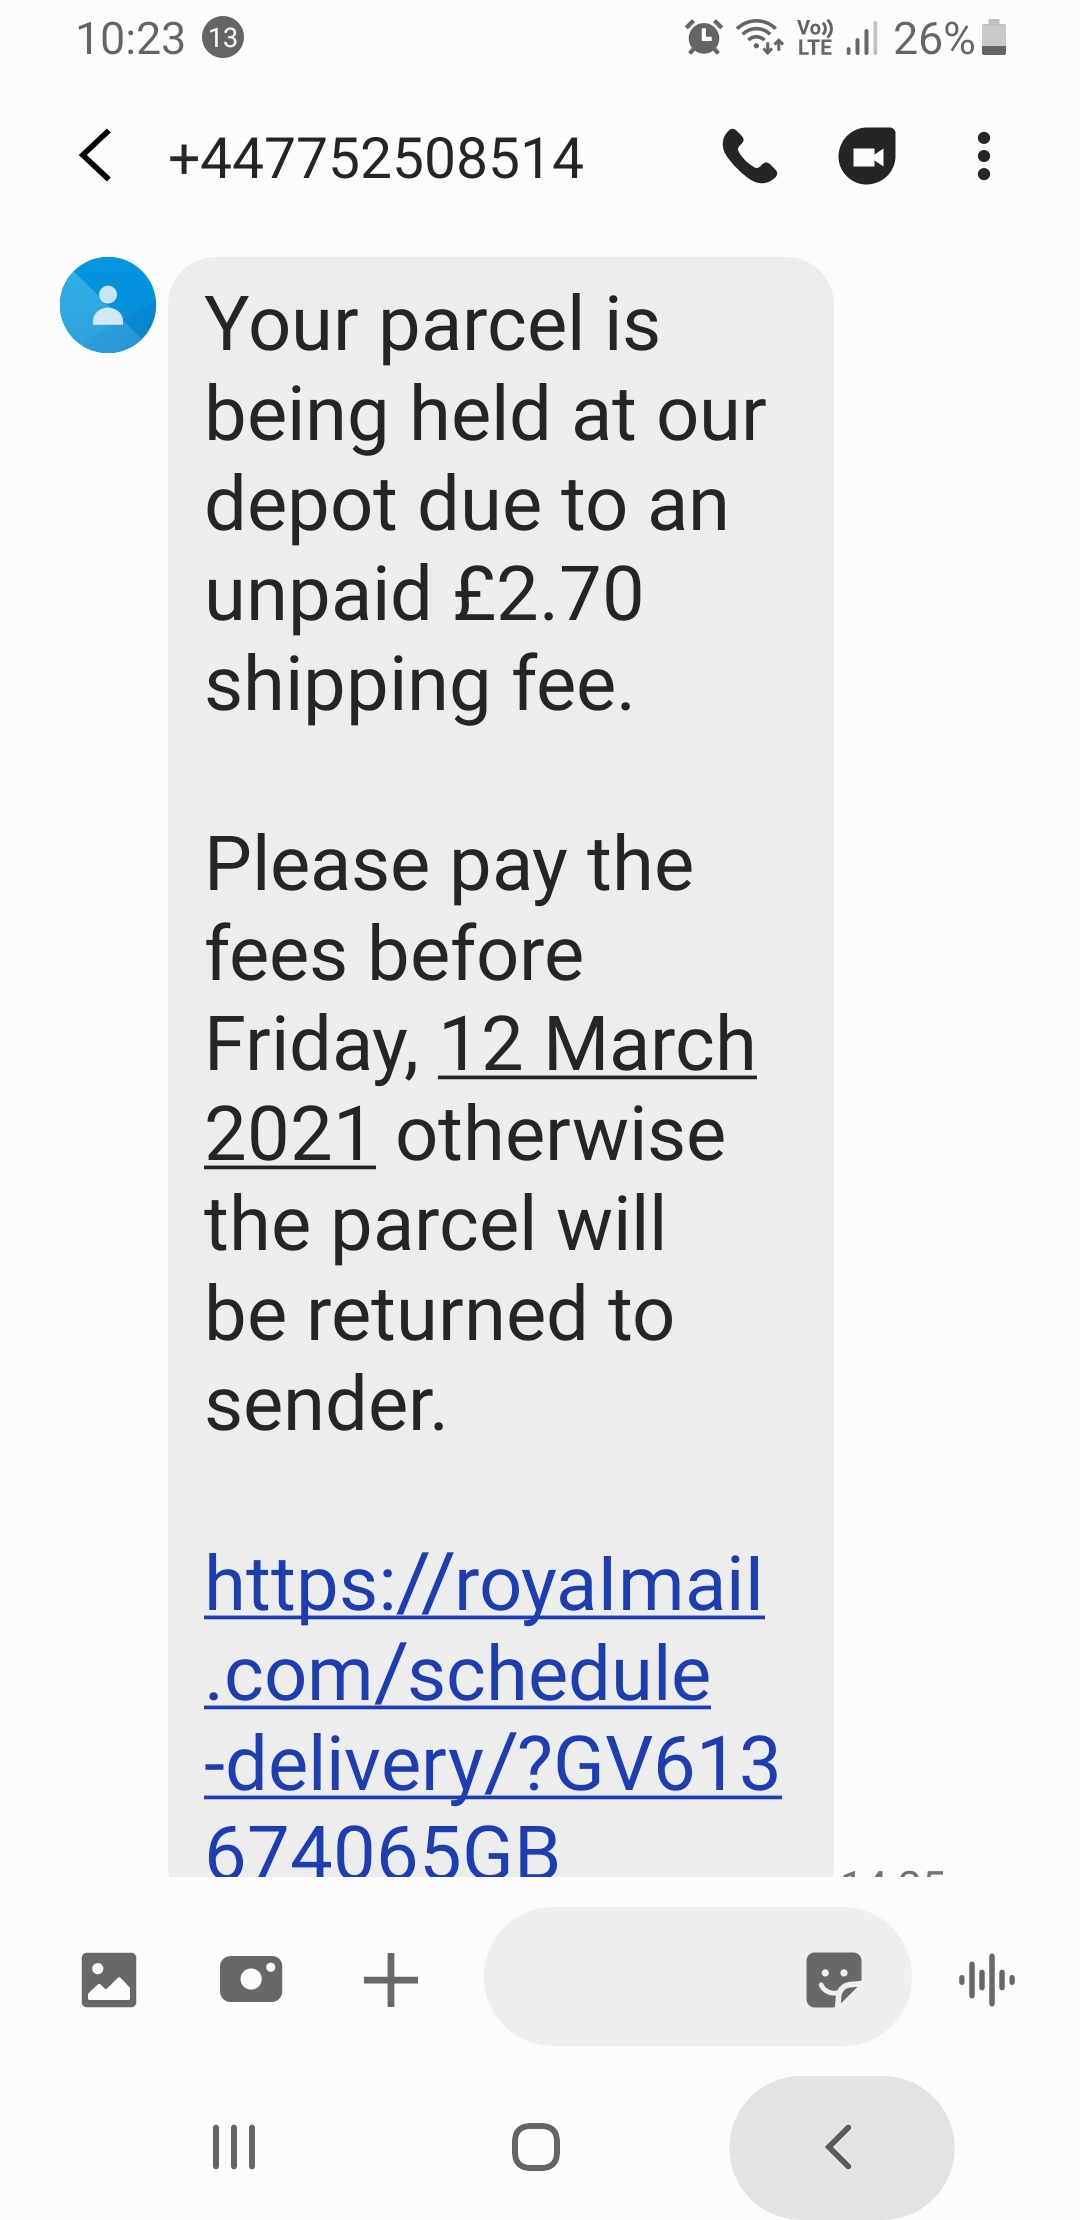
Royal Mail smishing txt?? https://www.express.co.uk/news/uk/1408310/royal-mail-scam-alert-fake-text-message-warning-trading-standards-institute I must say that trying to find contact details for Royal Mail to check validity of the text is proving very difficult.

-
I'm not sure there is a end of sale let alone an end of life the 2930f is a decent switch INMO. https://www.arubanetworks.com/en-gb/support-services/end-of-life/ https://techlibrary.hpe.com/us/en/networking/products/eos/index.aspx#.YEj02_6nxhE There are some pros/cons to both. You cannot stack 2930f with 2930M but you can stack the 6300f with the 6300M . But for instance the 6300f/M does not have device profiling at the moment. You can stack up to 10 switches with the 6300 series I think. But yes the availbility for software updates and the warranty on Aruba is something to bear in mind. We are still getting 15yr old switches replaced. To be honest I prefer having out of band management (i.e. console port) on any switch.
-
We never use the GUI for switches here, it is all done in the CLI over SSH. I've only used the GUI in 2 instances in 5 years, lol. We do have iMC which we use for updating switches and making large batch changes but I'm not sure if I'd recommend it.
-
I cannot give any input about the 1930 but we have installed about 50 x 2930f's in the last 2-3 years or so and have had no issues. Mostly PoE+ 48 port models. We use them as ToR switches in a pair stacked in refurbs where we have 10+ in a comms or as stacked Edge switches connected to 5406R in bigger comms rooms (20+ switches). I've been using a few at home as stacked Core switches for last 2-3 years. We currently do not use Aruba Central for our 750+ switch infrastructure but are looking at it. The 2930f does do Layer3 routing and OSPF, and as you have mentioned stacking which depending on firmware is up to 8 switches.
-
I can just see some of those littered with so much malware and spyware it would be crazy to use them.
-
Sorted, Many thanks, I wondered if this could be done on a org level, maybe I was looking in wrong place, lol.
-
Hi All, I've only ever used the SMS before for my personal MS 365 tenant, but managed to get it to send a number to the MS authenticator app but would like to get it to do a MFA push instead to the authenticator app. Basically just click approve and away it goes rather than typing in the code. I currently have the Premium Business package because I wanted to play with MS Intune and the extras it gave me over my existing cloud email made it worth while at the time.. Can anyone tell me how to do this.
-
I had this at home and just ended up rebuilding the PC. It had been running for a few years and had all sorts of stuff installed and Windows updates.
-
We normally have a Friday no change rule, well some changes but we generally edge on caution for anything service effecting, lol.
-
PBX unable to find some network phones
Davit2005 replied to Twearden's topic in Internet Related/Filtering/Firewall
Quite possible. Without knowing a bit more about the setup i.e. Diagram switch configs, dhcp scopes etc. It is hard be sure. Have a look at how subnetting, masks etc. work. But basically if you had wrong mask say it was 255.255.255.0 following scenario. DHCP scope setup to give out 192.168.0.1 to 192.168.3.254 with subnet mask of 255.255.252.0, client gets IP address 192.168.2.5 and wrong subnet of 255.255.255.0 instead of correct one 255.255.252.0. This means that client will be in wrong logical network and not be able to get to gateway because it is logically on a different network. No access to gateway, no access to Internet or anything outside of the same subnet. -
Yeah I have upgraded quite a few times and it always goes well. Last place they had Veeam 6.0 when I started and over the years took it up to 9.5 before I left without any issues. Quite a bit has changed, they were originally using Backup Exec because of lack of tape support but thankfully managed to ditch Backup Exec just at the right time, lol. We had the Enterprise version and could restore AD users by setting up a SureBackup job which involved starting the DC in an isolated environment and then restoring objects into the live environment then they brought out all the Active Directory Explorer which made it not necessary to do that any more :-) .
-
Many years ago was, yeah they ask to reply with number which is a pain in the rear but I'll do it. Got first phishing email from a bank about 20 years ago, yeah never had account with them either, lol.
-
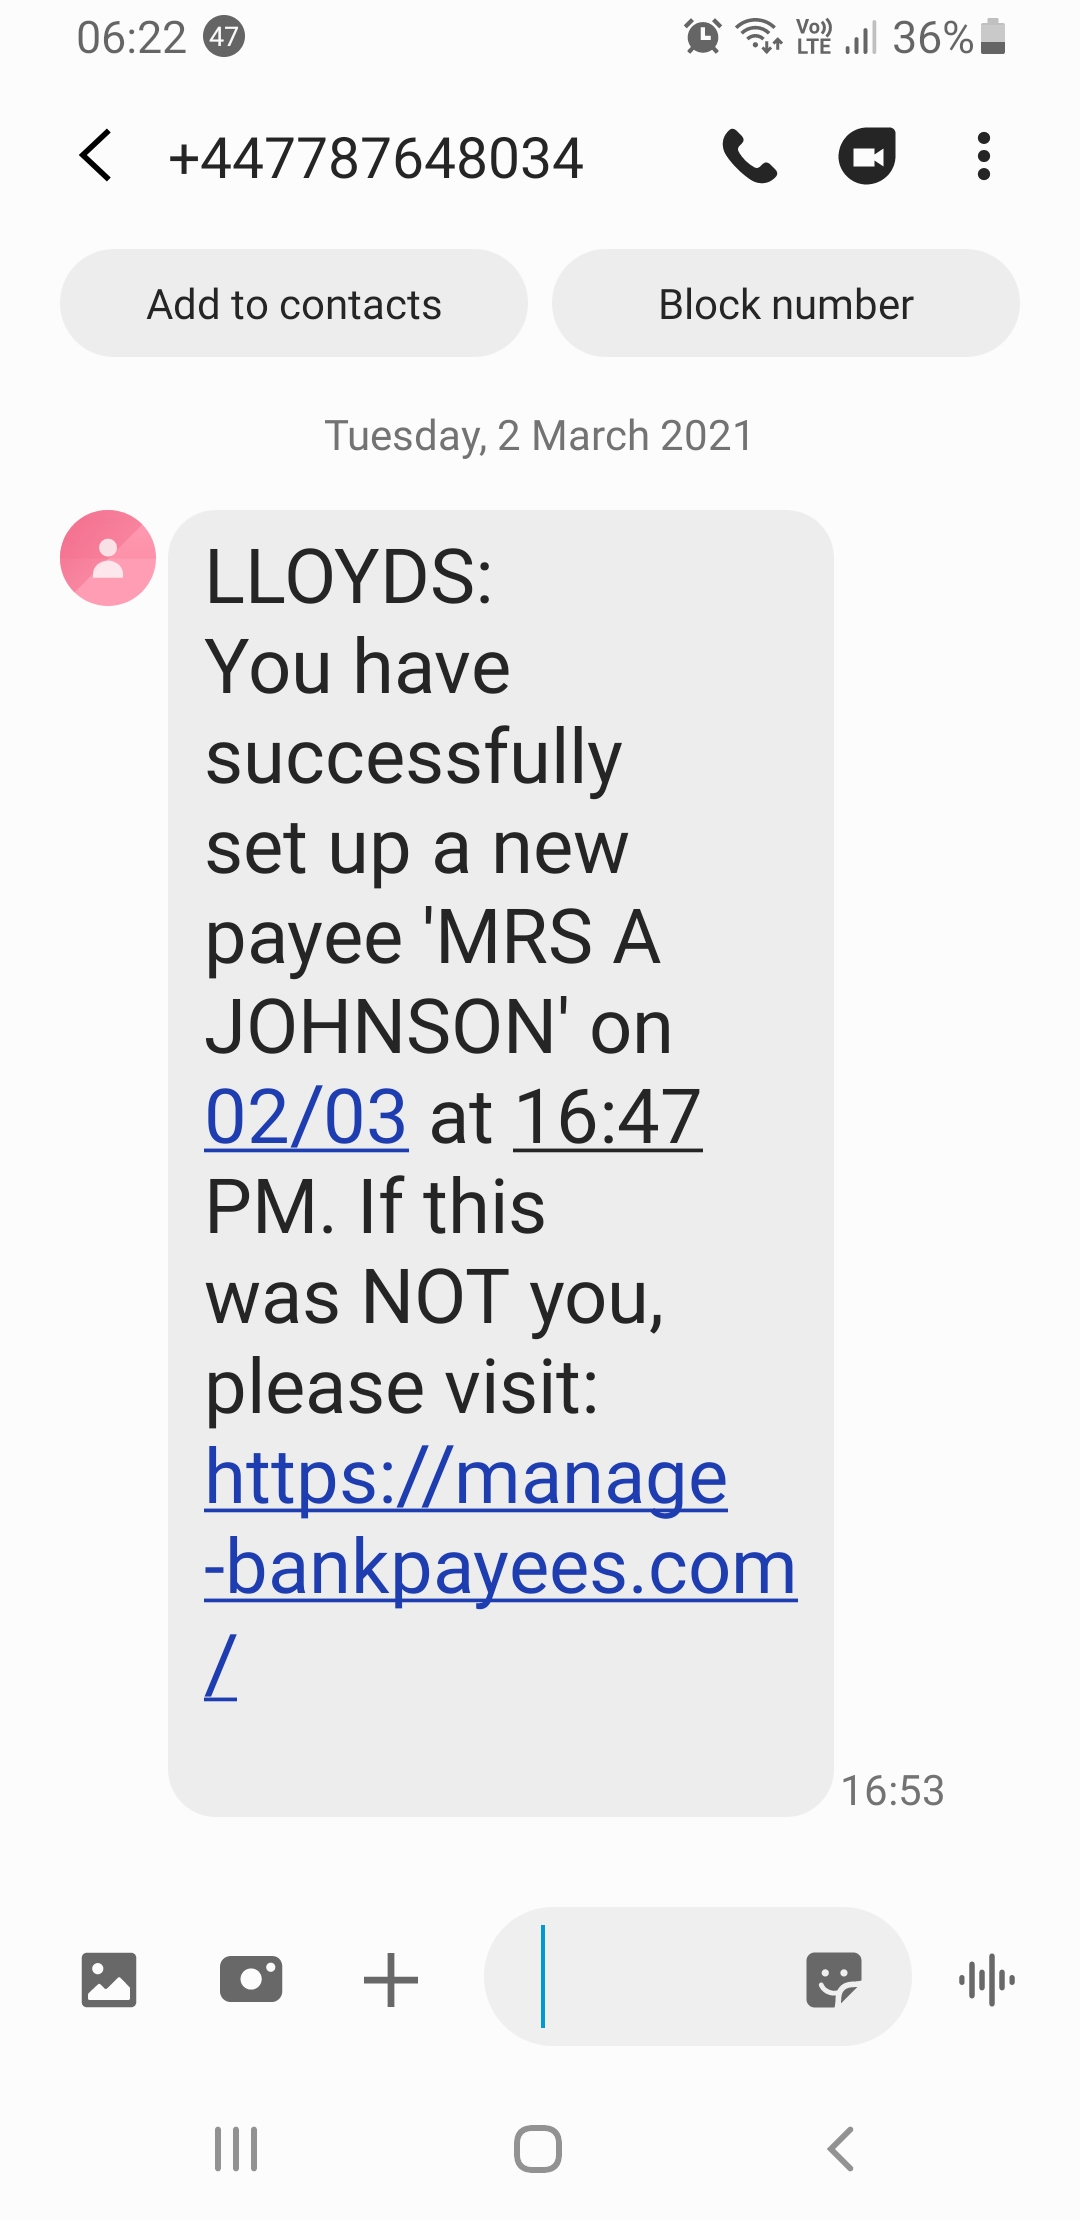
Smishing TXT for LLoyds , forwarded to 7726. Claims new Payee setup.
-
I've just installed the Windows Agent to backup my home video editing/design PC. Just purely for the boot drive as getting everything setup is a royal PITA on the desktop. Editing footage is on seperate internal SSDs then backed up over 10Gb network onto a Synology and then taken offsite on a few external SSDs for safe keeping. Does take a while to do the backup over a 1Gb link to an SMB share even for the small OS 256Gb SSD. I'm considering moving over to the M1 Mac Mini but it will only be for specific (design creative) use, normal daily driver is a Linux PC for last 2-3 months and prob will stay that way.
-
Wonder if they do a free version with this one or if it is on the dev/horizon. I only last month installed Veeam 10,
-
PBX unable to find some network phones
Davit2005 replied to Twearden's topic in Internet Related/Filtering/Firewall
As @Steve21 mentions. Check options, probably tftp options on the DHCP scopes. But could be vendor options such as option 43 depending on PBX. -
I got a teltonika RUT955. It has a lot of features but seems to need rebooting every once in a while. 2 SIM slots, external aerials, WiFi hotspot, 4 ethernet ports one can be configured as WAN backup etc. Support seems flakey. If it weren't for the needed reboot I'd recommend it.
-
Some old HP Optical Mouse and a KLIM Chroma Gaming backlit keyboard. Both are wired as swap between multiple desktops with a HDMI/USB switchbox
-
You could have a look in the security events on your domain controllers for login events then see if you can see any extra info. Are the APs individually added to the NPS server or is just the SonicWall added?
-
On firewalls normally you would use some form of way to map username to IP address. This could be done via some form of agent that the SonicWall can talk back to. I have seen in the past this sort of agent installed on fileservers, windows servers domain joined, but also some able to interrogate active directory directly for login events. If users are authenticating against a Captive Portal that is tied to Radius for authentication I'm surprised you are not able to see the user names in the NPS accounting logs when they log into the captive portal. I've not experienced Captive Portal authentication by radius however.
-
What are you using for RADIUS (Windows NPS, freeradius, etc) , and is this backed to Active Directory authentication??
-
[video] John Noakes Climbing Nelsons Column
Davit2005 replied to caffrey's topic in Jokes/Interweb Things
I think the helmet (or lack of) would be least of my concerns falling from that height, but then again maybe not Yes he did know what he was doing, certainly a lot of trust in his knots :-) -
[video] John Noakes Climbing Nelsons Column
Davit2005 replied to caffrey's topic in Jokes/Interweb Things
I might of been able to get up that ladder but I would never be able to get back down, makes my heart rate increase just looking at it. You wouldn't be able to do it these days due to H&S unless you done it illegally/unofficially, lol. -
You should be able to manage DNS settings in you GoDaddy admin page. How you actually do this step by step will be different between providers. GoDaddy may have a help section to guidde you.