Koldov
-
Posts
5,084 -
Joined
-
Last visited
Content Type
Forums
News
20th
EduGeek EDIT Conference
Blogs
Everything posted by Koldov
-
Checking the permissions on the original file, the security group the user is part of has security permissions as 'Full Control', however in 'Advanced > Auditing' select principal 'user name' (it show here they are the 'owner'), they only have Read & Execute and Read....(What?!)... On the multiple random folders that appear, the permissions are as above, Security = Full Control for Security Group, 'Advanced > Auditing' select principal 'user name', they have Read & Execute, List folder Contents and Read.... Could this explain why they never get 'cleaned up'...?
-
I've asked this before, but got the 'internet forum' equivalent of a blank look (no answers to my thread)... Hopefully the right person will see this thread and know the issue (and have a solution), as I'm sure it can't just be me! Currently about to drop the Headteacher's MacBook from a great height and go 'whoops, you'll just have to use a Windows laptop for now' and then just make sure the new MacBook order never reaches the Finance Department... I am testing as we speak and can confirm the following: Open Word on the Mac Create new Doc Save Doc on server OK so far, can see file saved on server and whilst open can see temp file If we close the file now everything is OK, temp file disappears. I can open and close this file (no changes) as often as I like and the above repeats. However, if I make a change to that document and then save it, this happens... With multiple random folders appearing and random files inside. This happens for every file they create, save, edit and re-save...

-

50,000 users on 2019 hangs but works with 2012R2, any solution?
Koldov replied to coderr's topic in Windows Server 2019
Sorry, I can absolutely NOT help you with your issue, or offer any insights into what is going on but... From your OP these are cloud based VMs and you have no issue spinning up new ones and flattening old ones...? Just a thought out of left-field... could you create your 2012R2 instance and all the users etc. Then in-place upgrade to 2019 (got to admit I'm not sure how easy that is on a cloud server). Also is there any way you could use a modified script to create a much smaller amount of users to test? If it starts with a good amount of users you can at least then export some of the settings/logs/stats/IIS settings/check users firewall/resources/collect memory dumps etc. -
Yeah, I think this was the problem with whoever did the spec for the original server... they didn't put in enough disks for the DATA virtual disks to be anything other than RAID 1 really. I'm sure it's OK for redundancy, but it can't be great for write times (?). Or maybe they just wanted that 1 - 1 data security...? I have to say I cheated a little on the newer server and copied the separate physical disks for OS/DATA idea from that (also because it's what I've been doing in personal machines for years ), but did a bit of research to make sure I had enough disks for a decent level of RAID on the DATA disks. Didn't do enough research on the RAID controller though obviously as the PERC H310 is about as basic an entry level controller as you can get. It doesn't have any cache, so I think that's why it might have been set as 'write-through' (?). It must have come from DELL set up like that though because I only really looked at it much later on and never really got a handle on whether I should change it (still haven't and now I know the H310 has no cache it might be a moot point). So you have: 4 DISKS > RAID 10 = 1 VIRTUAL DISK > 2 partitions (C: & D: ). But you are thinking of: 4 DISKS > RAID 10 = 2 VIRTUAL DISKS > disk 1 partition (C: ) & disk 2 partition (D: ) Unfortunately I can't help you on the benefit (or not) of virtual disks on the same physical disks, I guess there's a lot of factors that come in to play. I can see where you are doubting the setup, but if the issue is writing to the physical disk (even through 2 separate virtual ones) then I'm not sure you can avoid it (?) or that it will make a difference. To separate them out you could go single disk for the OS and the other 3 in RAID 5 for DATA (?)... If you were feeling brave... might be waste if you got 4 big disks though, so I can see the logic of lumping them all together and then dividing them up as you have.
-
This thread prompted me to have an in-depth look at my servers... 'Server 2' was our old original server, it was set up before my time and I always wondered (but now I know) why it was slower than 'Server 1' which I set up and moved most of the important stuff to (SIMS, File Share, etc.), it wasn't slow enough to really be a problem so never really bothered looking at it in any detail, just when working between the two though it was noticeable. I don't have the need to change anything major like adding disks to change RAID levels because it would be a cost (both in time and money) for no real benefit as it doesn't have a heavy workload (it only hosts a couple of VMs, one for secondary DC, one for Print server/WSUS and one for a Windows 10 RD instance). But interesting to see the difference in things like Write/Read and Cache policies and stripe size... Can anyone explain (in basic terms) what the difference is and what's best practise for a basic 'do it all' school server?
-
I'm only just getting started with VEEAM, so forgive my ignorance... But is there an easy way to set the credentials in one place for VEEAM to connect to the servers it's backing up. I've started to change the admin passwords on all the hosts and VMs and I guess I didn't give VEEAM much of a thought, but it failed to run a backup whilst troubleshooting a different problem. Various error messages... requires Veeam integration components to be upgraded. Unable to allocate processing resources. Error: Unable to find Hyper-V hosts where VM is registered: Failed to connect to Hyper-V Integration Service on host, port 6163. ...led me on a bit of wild goose chase through VEEAM forum posts, support docs, knowledgebase articles and general interwebs searches. Finally one of the last messages... connection to the guest could not be established ...said it couldn't connect to the VM and made me remember I had to put in credentials to the backup job, it seems as if there was a couple of places 'credentials' could be entered but once they were all changed it went through fine. I plan to do this fairly regularly (change passwords) and luckily I don't have many, but this must be a pain for admins with lots of VMs... Is it just a manual job, to edit every credential on every job each time they are changed, or is there a better (or best practise) way to do this...?
-
I seem to remember back in the day, we had a VBS script (two actually) for Windows laptops put on the desktop for teachers. One that used to put in the IE proxy settings and the other to remove them!
-
Yes, a waste... I'm sure most of what I've managed to accomplish has been from various posts on here (there might even have been one in 'Pet Peeves/Annoying things')... Unfortunately when they come in with the 'it's happened again' overtone, I've started to reply with a 'because it's a Macbook in a Windows ecosystem' overtone... which I'm sure isn't helping my standing (unless you count my reputation of grumpy IT man)... Thanks @3s-gtech I like the idea of the 'network location profile'... I'm almost sure I can get him to remember how to click on it... dare I say it, sounds like a 1up for Mac OS...
-
Yes, the VM is just a standard Windows 10 instance, joined to the domain and SIMS added like any other desktop. Sorry, I guess I should've added that the user has been (exclusively) added to the Windows VM as an RDP user. RDP is internal (as in the GPO is configured on the Domain Firewall), but I'm not sure what else makes it internal/external. Not sure how I put RDP through the firewall, without putting RDP through the firewall...? The main GPO for RDP access is this: It has the I.P. of my work PC and the VPN range. Then the specific GPO added to the VMs OU which includes the main ones above plus the I.P. of the Macbook: As suggested here: http://www.edugeek.net/forums/windows-server-2019/231472-firewall-cumulative-overwrite-multiple-firewall-gpos.html#post1984048
-
OK, bit of a cryptic title... sorry. The Headteacher has a Macbook, as if that isn't bad enough he wants Outlook, Teams, Office, Windows Server share access and... SIMS (I'm still not entirely certain why he 'needed' a Macbook as he doesn't seem to use or know anything about the actual Mac OS)... Initially I was thinking dual boot/parallels etc. But the quickest (and most fool proof) way I thought of to make this happen was to get a VM running SIMS stood up on the server and the MS Remote Desktop app for Mac. This works OK and has been fine for a while, but I have to punch a hole in the firewall for the I.P. of his Mac. Every so often DHCP changes this and he is blocked... it's only happened a couple of times but now unfortunately he comes to the office saying he can't get on to SIMS with that "it's happened AGAIN" undertone... I showed him how to find his I.P. and it can be quickly sorted once he lets me know, but it's becoming a 'thing' and I don't want it to be a nail in the coffin of my job (I mean it's not that drastic in the grand scheme of things, but it all adds up)... I've looked at setting his I.P. address as static, but then it won't connect to any other network (?). I would look at something like a reservation (?) in DHCP, but DHCP is done on our CISCO switches and that's way over my head (so, difficult to do in the first place and to troubleshoot if it goes wrong). I've also looked at setting the admin wi-fi range of I.P.s in the firewall GPO, but, well RDP... am I right?! This HAS to be locked down if used at all, not opened up further... Any other suggestions (considering I am not a Mac or CISCO expert)...?
-
[ms office - 2016] This file came from another computer...
Koldov replied to Koldov's topic in Office Software
"change Security Settings of Internet Zone in Internet Explorer properties" What?! :doh: -
[ms office - 2016] This file came from another computer...
Koldov replied to Koldov's topic in Office Software
Not sure how I missed that post as I normally keep a close eye on the forum after patch Tuesday... Anyway, that explains it, many thanks! -
[ms office - 2016] This file came from another computer...
Koldov replied to Koldov's topic in Office Software
OK, from a bit of research the following should be happening with a few different factors at play... A downloaded file has ADS (Alternative Data Stream) marking it as downloaded. Office should open this in 'Protected View'... ...but this is not happening for the Teacher's laptops (so this is the main issue). Workarounds I've found (but not tried) are: Turn off 'Protected View' in all Office applications (not something I'd be happy with). Enable “Do not preserve zone information in file attachments” in 'Attachment Manager' (again, not happy with that). Clear Data Stream Files - All the files that you download from the web are tagged with a stream. Your PC determines that the files are from an external source through these streams. If you clear certain data streams that are marked with a zone identifier, all the files on your PC will be unblocked. You can do this using a Microsoft tool called Streams. To clear Data Stream files, you can follow these steps. "Download Streams from Microsoft official website and run it. After opening Stream, go to “Browse and navigate to the affected folder or file directory” and select Scan. After scanning, you will see all the streams in your files. Find “:Zone.Identifier:$DATA” on the scanned result and right-click on it. Click on Delete Selected Streams. Close the file and Restart your PC" Seems pretty extreme and with possibly disastrous consequences... Or unblock whole directories with Powershell (if you're 100% sure all files are 'safe')... dir C:\Downloads -Recurse | Unblock-File It all seems a bit much, I just don't think I should need to do any of that... and still none of this explains why it isn't opening in 'Protected View' (and no error message) for the teachers and why it's just started happening.
-
[ms office - 2016] This file came from another computer...
Koldov replied to Koldov's topic in Office Software
No, Windows 10. Downloaded file warnings have been a thing for a while now so it's not a new feature as such... I'm pretty sure it's been around for along time since at least maybe XP... I'm just not sure why it's decided to kick-off now...? Maybe because I copied all the shares off from the server and back recently, I just don't know as it's not every file! -
[ms office - 2016] This file came from another computer...
Koldov replied to Koldov's topic in Office Software
Got another one this morning! Seems like a file downloaded from the internet as I've checked the file properties and the 'Author' isn't one of our users...
-
Today I had a teacher telling me her laptop was 'broken' and could I fix it in the next 5 minutes because her next lesson was about to start... The killer opening line was... "So, this has been happening for the last few days"... OK, so why didn't you come and tell me a few days ago! Anyway, I did fix it in 5 minutes but the thing is she was double clicking random Word files from either her own desktop or the server share, some had been downloaded from a well known teacher resource site, some had apparently been on the server 'for years'. Nothing happened, no warning, no 'this file is blocked', nothing... just wouldn't open (strangely enough it would open from within Word)... Luckily last week I had a teacher ask why she couldn't open a Powerpoint file she had downloaded (same behaviour).... Right-clicking the file shows in the 'General' tab something like, 'This file was downloaded from another computer and may harm yours, etc'... With a check box to allow it to be opened. Now, I've always known about this feature (but if iirc it was 'this file was downloaded from the internet'?), but it's never been an issue for us as far as I know... and trust me I would have known about it by now if it had been with the amount of resources this lot downloads... I have told her for now to check this box per file as I may be unable (or unwilling ) to change this default 'security' behaviour globally. So, questions... It seems this has only recently (ish) started happening (but who knows with teachers), does anyone know if any extra security settings have been applied in an update lately? Is it a Windows Explorer 'security' function as it seems the file can be opened through Word with no problems? I can't work out the provenance of every file, so how can I tell if it is happening only with files downloaded from the internet or just from 'any other computer'...? It could be that she just happened to pick 3 files that were downloaded... It doesn't seem to happen on my PC, but I have a different Win10 version and a different Office version (plus I don't have a login for the resource website to download files from).
-
BETT 2023 GIVEAWAY - What is your earliest gaming memory?
Koldov replied to VeryPC's topic in Our Advertisers
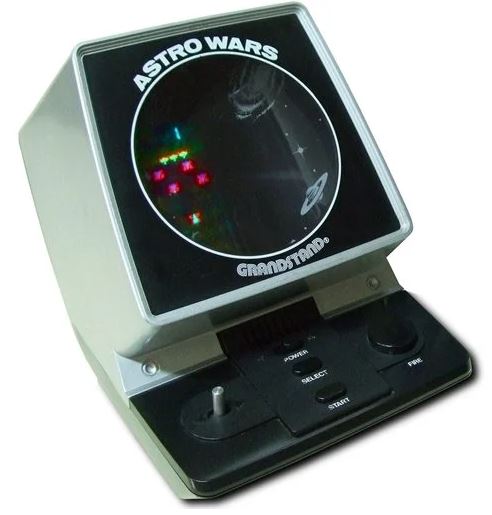
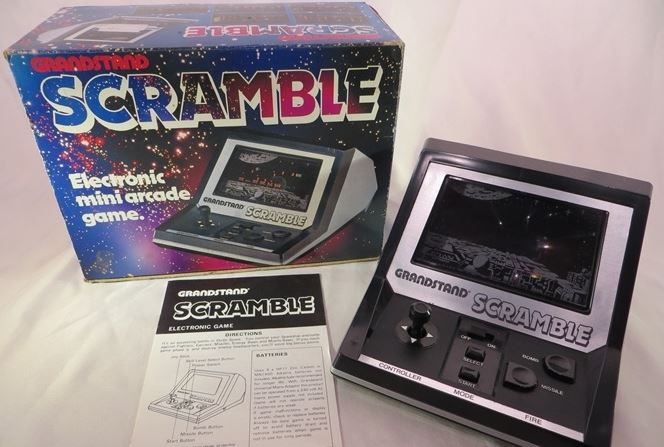
Obviously memories have faded because it was a very, very long time ago, but the earliest...? I seem to remember having these 2 beauties at some point in my childhood! I also have an early memory of being bundled off to Gt. Yarmouth when I was young to stay with my Aunt & Uncle for a Bank Holiday weekend, being given about £20 for the weekend and blowing it all in the arcades on the first day... Then what seems to be a common theme... Commadore64 - apart from the painful loading times of the cassette tapes, there was the ability to write your own 'games' in BASIC from a magazine called INPUT iirc. After typing in what seemed like 1000 lines of code, you'd get a 'SYNTAX ERROR LINE 796' and next month you'd find out it was a printing error, so it should have been a : instead of a ; Anyway retype the whole thing to get a square 'ball' bouncing around the screen... I think this is what put me off coding for the rest of my life... Amiga Playstation 1 Then I got a PC... found Counterstrike (played up to about 1.6 - don't talk to me about any versions after this) Half-Life mod (over a 56k modem - as someone mentioned kids today not knowing the pain of early gaming). Got in a clan, played some tournaments... that took up at least the next 6 years of my life. Anyway, I'd quickly found my 'TIME' computer with AMD Duron CPU, onboard ATi GFX and 64 MB (yes MB) RAM wasn't cutting it (but as it cost me around £1500 I wasn't going to buy a new one)... No AGP slot so after some PCI (not 'express' kids just PCI) GFX cards, I ended up going full motherboard replacement, shiny new ATi 9800pro, new AMD Athlon CPU, new GEIL RAM and this started my tinkering with computers and I.T. in general which lead me to my current glittering career changing toners and turning it off and on again...
-
Time to change my profile pic etc. So I don't end up 'on a list' (well at least not that one anyway)...
-
We do have Junior Librarian, but last I knew the librarian was doing a manual upload from a SIMS output file, so I don't think we've linked that. We do have CPOMS and Groupcall have got back to me saying that is one of the data feeds they have from the school.
-
Thanks, but it does appear that they are shortcut/website links. https://support.google.com/chrome_webstore/answer/3060053?hl=en-GB#:~:text=Add%20a%20shortcut,click%20Create. Whoever thought that was a good idea... still I suppose it might have its uses and keeps the workflow in one place to jump off from. Thing is it's giving him the warning that apps no longer work, but he doesn't have any apps and only uses it for shortcuts. I've told him to edit his 'New Tab' page and put all the shortcuts on there.
-
This is great stuff... I have already found that due to a crossover in communication, we are apparently sending '2Simple software' data for 'Purple Mash' both via 'Groupcall' and 'Wonde'! The Headteacher and Business Manager have the Dashboard for Wonde (as was mentioned it is end-user driven - and why I don't know what is going on) and have apparently agreed to the data sharing, without checking if the data is being transmitted already (which it appears it is - through Groupcall Xporter)...
-
I have 'Microsoft Office LTSC Professional Plus' installed on my work PC and use Outlook to connect to 4 email accounts. 3 of these are 'itsLearning' accounts and one is an 'LGfL' account. I'm not sure what back-end these providers use O365/Exchange online or if indeed it is all the same thing nowadays... I never use saved credentials and so I'm asked to sign in to all the accounts, but only the LGfL one asks me everytime, the itsLearning accounts seem OK for a while and then will randomly ask.... Anyway, the 'itsLearning' accounts come up through Outlook with their own mini browser window (the 'itsLearning' front-end) which is ridiculous as I can't tell which of the 3 accounts it is asking me to sign in to (no saved credentials/username). The main issue is (on the rare occasion I need to re-sign in to the itsLearning email accounts), after signing in to the accounts through Outlook, whenever I open another Office application (Excel/Word/Powerpoint) I have automatically been signed in to these too...
-
Great info, thanks!
-
I have an email from a teacher this morning about Chrome Chrome Apps/Desktop Links, it keeps coming up with the message that it is no 'longer supported' and instead of taking them to the webpage says: "Old versions of Chrome Apps won't open on Windows devices after December 2022. You can check if there's a new version available." As far as I know, this isn't really an 'app' just a shortcut/link to a website... It has only just recently started happening, but the thing is, it isn't really supported by me either... I only really started installing Chrome as a quick fix when grumblings started about IE11 (and Edge wasn't anywhere near ready), we only use Windows 10 and I push out 2 Windows desktop shortcuts for the websites all staff use. Whatever this 'Apps' thing is, the teacher has done by themselves. I don't really 'manage' Chrome apart from the GPOs to restrict/allow certain things, so I don't know much about the extra parts of the browser interface. I don't use this 'feature', my shortcuts appear on my Google 'Home' page, I don't want to waste time holding their hands or changing their workflow. Any way around this (apart from telling them to use the desktop shortcuts I push out and not this 'feature' within Chrome)...?
-
Possibly some crossover here as this is also about software installed on our server... After some scrutiny, we have identified software on our server that collects data from our MIS and transmits it to a third-party. Although I believe legitimate, we have very little documentation (OK, none) about what data is being collected and who it is sending to which is unacceptable. All this was set-up before I started, but it's ringing alarm bells. So far the software identified is: Groupcall (Emerge\Xporter). Wonde. USO autoupdate. Pebble There are also various scheduled tasks which run both within the software and in the server to run these programs. Groupcall - no idea, although I think there may be B2B (which apparently 'might' be a job from the LEA?) and Meritec jobs associated with it. Wonde - possibly something to do with a Learning Platform\Service, maybe Purple Mash. Pebble MISapp - I think this is a finance package... (waiting to hear from the Business Manager)? USO - This I have found out is for LGfL accounts (but we don't use any of LGfL's USO services that I'm aware of, so I'm going to stop/uninstall this anyway).