kennysarmy
-
Posts
6,514 -
Joined
Content Type
Forums
News
20th
EduGeek EDIT Conference
Blogs
Everything posted by kennysarmy
-
Smoothwall Realtime Logs : 304
kennysarmy replied to kennysarmy's topic in Internet Related/Filtering/Firewall
So a 304 error is nothing to worry about? The traffic/request was successful in both directions? -
Hi, Does anyone know why Smoothwall can give 304 errors ?
-
You'll love their latest response! Re: When logged in as 7316 (application opens correctly) ... When logged in as 7305 ON THE SAME PC ( That means your endusers share the same PC now and then. You didn't tell me that on Monday during the session. If that is the case, then the sign in request works as intended. I'm going to contact the development team if they have another idea to solve that. The only solution I know is to edit the registry entry (what you had already done with importing the registry from the working user to the non-working user). I had escalated this as an enhancement request last year since mostly companies work in shift with often 3 users on the same machine. Thank you, Simone Corel Customer Support
-
Useful from COREL 3rd line support! Have you found out the differences between that group where the other user belonged to? He must have had something different compare to the first user. The problem is as I said not related to CorelDRAW but the way how these users are integrated into the system. Thank you, Simone Corel Customer Support Err no - they are all standard student accounts - all exactly the same!!! Must be a bug in your software? It's no bug in our program, but there was something different in the approach to install the program and when the students launched it the first time. Let's say it in that way: I get a lot of those companies with servers and they all manage it. In other words, there must be a way to get this done from a view of IT. Thank you, Simone Corel Customer Support Please can the call be upgraded to second line support? It's not about how they open the program: it's all about what version they got installed (seems to be from the server image), and what profile they use. If they are all users, then it might be the reason that they have limited permissions to add content to the registry. What server do you use? And do you use cloned systems? What your request regarding a second line support concerns, I'm the third and last level and do this job for more than 10 years now. Our support is not about helping in a network environment as these are parts of the company's own department, or as our IT admin used to say when I naively asked him 10 years ago, "how do you deploy", and he said, "boa, Simone, there are so many ways to do it, each IT has got its own way". Everybody who contacts us in such issue "want to deploy", ends on my table and all I need to provide is the information to use a server image. In 99%, I only get a final reply form them, "issue is solved, close the ticket". As I said yesterday, this is what other ITs mentioned: "when the users started with USER accounts, they were not able to avoid the sign in window, we had to change to an Administrator account" Note from my side: I installed from a server image in my VMware into an admin account -> created a USER account -> launched Draw in that USER account and I was not asked to sign in. Conclusion: there must be something different between a corporate USER and my ordinary Windows USER Thank you, Simone Corel Customer Support
-
So my question relates to a thread I started yesterday! http://www.edugeek.net/forums/windows-10/223888-core-draw-issues-ntuser-dat-hkey_current_user-software-corel.html I have installed Corel Draw to numerous PC's and laptops and we're getting more than occasional issues whereby users randomly cannot open Corel Draw and I was trying to understand the process around how values in HKCU are created. Once a user has successfully logged on, is it possible to edit keys in HKCU remotely? I tried to edit some keys for Corel Draw in "HKEY_CURRENT_USER\Software\Corel\CorelDRAW\23.0\IPM_CDGS" which I thought was causing the issue but on launching the program the keys reverted back to how they were before I edited them
-
When a new user to a PC logs on, how does NTUSER.DAT get created - where does the information come from? And secondly when a user GPO is applied does that write updated registry settings back to NTUSER.DAT or are the registry changes applied each time just to the HKEY_CURRENT_USER key? Thanks.
-
Loaded a couple of Reg Hives from two users on the test PC (one working, one not). You can see this part of the registry is different...wonder if this holds the key to the mystery.

-
Just had a remote session with Corel Draw Business Support. I've just sent them a summary of the call which is : Thanks, Simone, for the remote sessions earlier so we could show you the random problems we're getting with Corel Draw not opening correctly for some of our users. I understand from our conversation that other institutions in the past have had similar issues, but that there is not yet a fix from Corel? You explained that you believe the issue is related to the loading of the file C:\Users\Someuser\ntuser.dat into the HKEY_CURRENT_USER part of the registry, specifically the entry which populates into HKEY_CURRENT_USER\Software\Corel\CorelDRAW\23.0\IPM_CDGS I've sent you two registry exports of key IPM_CDGS from HKEY_CURRENT_USER one when logged on as a user where Corel opens fine and one from when the issue occurs. I'm hoping from these two files you will be able to identify which exact line of the registry is missing or corrupt so we can put in a temporary fix. However, a better solution would be for Corel to understand what is happening on the local machine to cause this issue and put a permanent fix in place. I'm still not 100% as to what Corel checks at launch to know whether to open correctly OR to show the logon splash screen (Which it should not do) We've done a server deployment which should mean the software just opens on launch, but for random users they get this splash screen: Clicking Skip just closes the splash screen and nothing happens. Corel believe this is related to the key : HKEY_CURRENT_USER\Software\Corel\CorelDRAW\23.0\IPM_CDGS I understand this is populated from NTUSER.DAT. But my question is how does the correct (or wrong) data regards Corel get in to NTUSER.DAT ? If we delete the local profile for an affected user it will temporarily fix the issue, but it can return!
-
CMS_2kv3 and Hikivision CCTV software
kennysarmy replied to Kitkatninja's topic in Physical Security
https://www.hikvision.com/en/support/download/software/hikcentral-pro-v1-6/ -
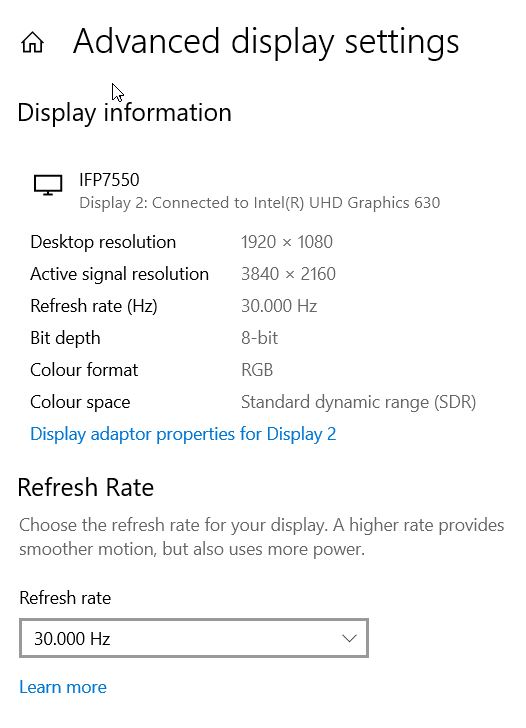
Hi, No the active resolution was always there.
-
We've created a "server image" to roll out our new Site licenced Corel Draw suite. It installs fine and works fine for a while. Then random machines seem to lose their licence, so instead of just opening Corel Draw automatically at shorcut launch we get this screen! This screen should not appear! Some users are able to skip the screen and some when they click Skip the page disappears then nothing happens. If we delete the user profiles for affected users it then starts to work as expected again. Any ideas?
-
CMS_2kv3 and Hikivision CCTV software
kennysarmy replied to Kitkatninja's topic in Physical Security
From their website I believe.... -
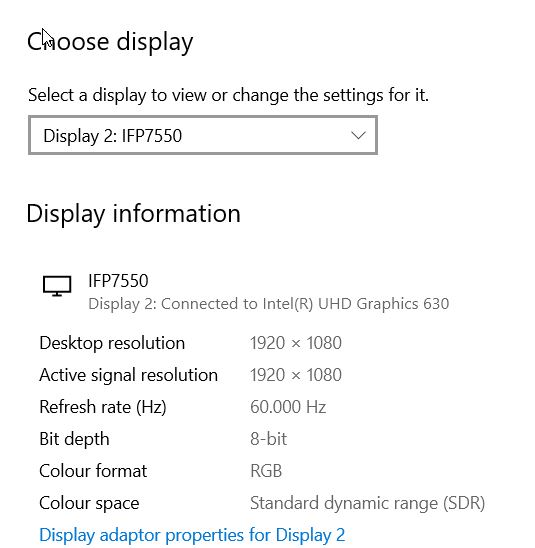
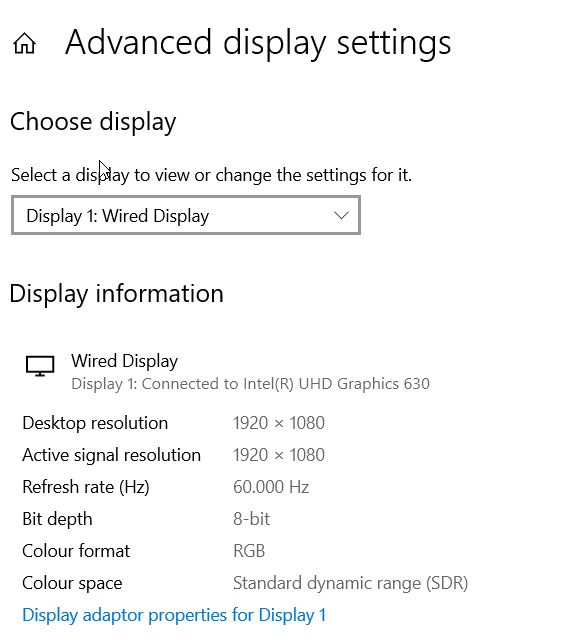
Hi, We've now changed both displays so the resolution and refresh rates match. Previously the panel was set as : We're waiting to see if the issue re-occurs. We've also put a cheap HDMI splitter in one room as that should also fix it!
-
Cabling options for desks in middle of rooms
kennysarmy replied to DrBeaker's topic in How do you do....it?
No way the students left the keyboards and mice so neat -
They look better opened with "Top 40 Mix" written on the label in biro.
-
Interested to know. Is there a solution to the automatic creation of both student and staff accounts in Azure AD from Bromcom, that is fully automated? Data manager adds accounts to Bromcom - and that's it - users are then able to logon! WONDE would handle third party app logons after the sync with Bromcom too.
-
Sophos Phish Training emails being quarantined by Office 365 :(
kennysarmy replied to kennysarmy's topic in Cloud Services
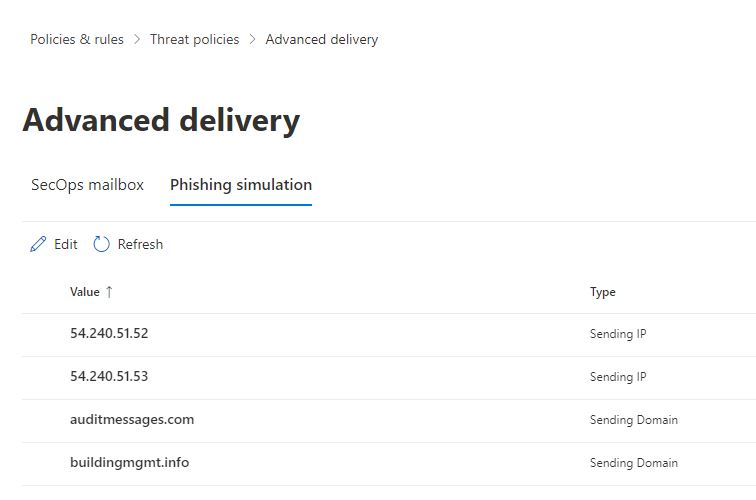
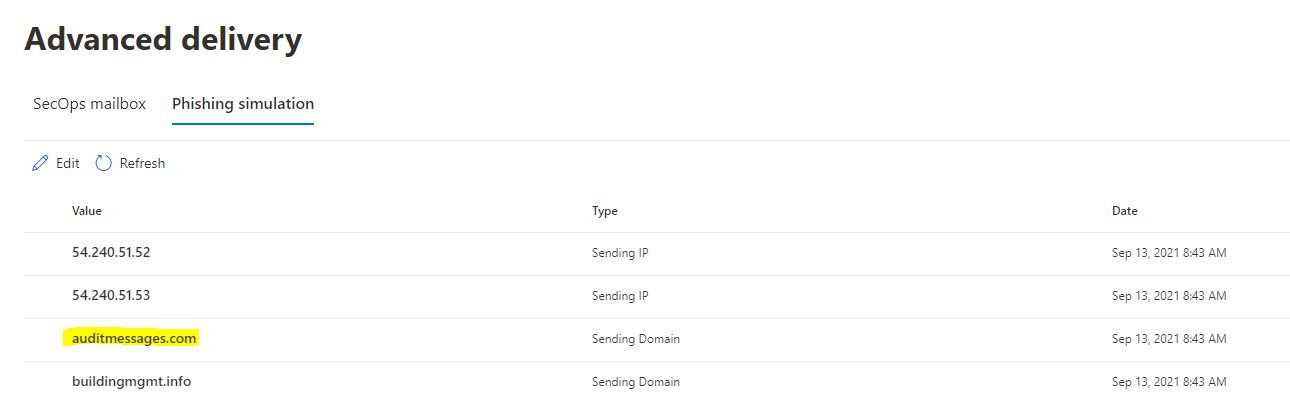
Thanks for your PM and help. Seems this also fixed it for us: in the 'Advanced Delivery' settings. Sending Domain eu-west-1.amazonses.com Sending Domain staysafe.sophos.com Sending IP 54.240.51.52 Sending IP 54.240.51.53 Allowed Simulation URL gmailmsg.com -
Sophos Phish Training emails being quarantined by Office 365 :(
kennysarmy replied to kennysarmy's topic in Cloud Services
Hi, possibly but back in June/July everything was working fine - it's only Microsoft's Improvements that have broken things - - - Updated - - - I've fired another email off to Sophos to ask if they can offer some better advice than just pointing to Microsoft articles! -
Sophos Phish Training emails being quarantined by Office 365 :(
kennysarmy replied to kennysarmy's topic in Cloud Services
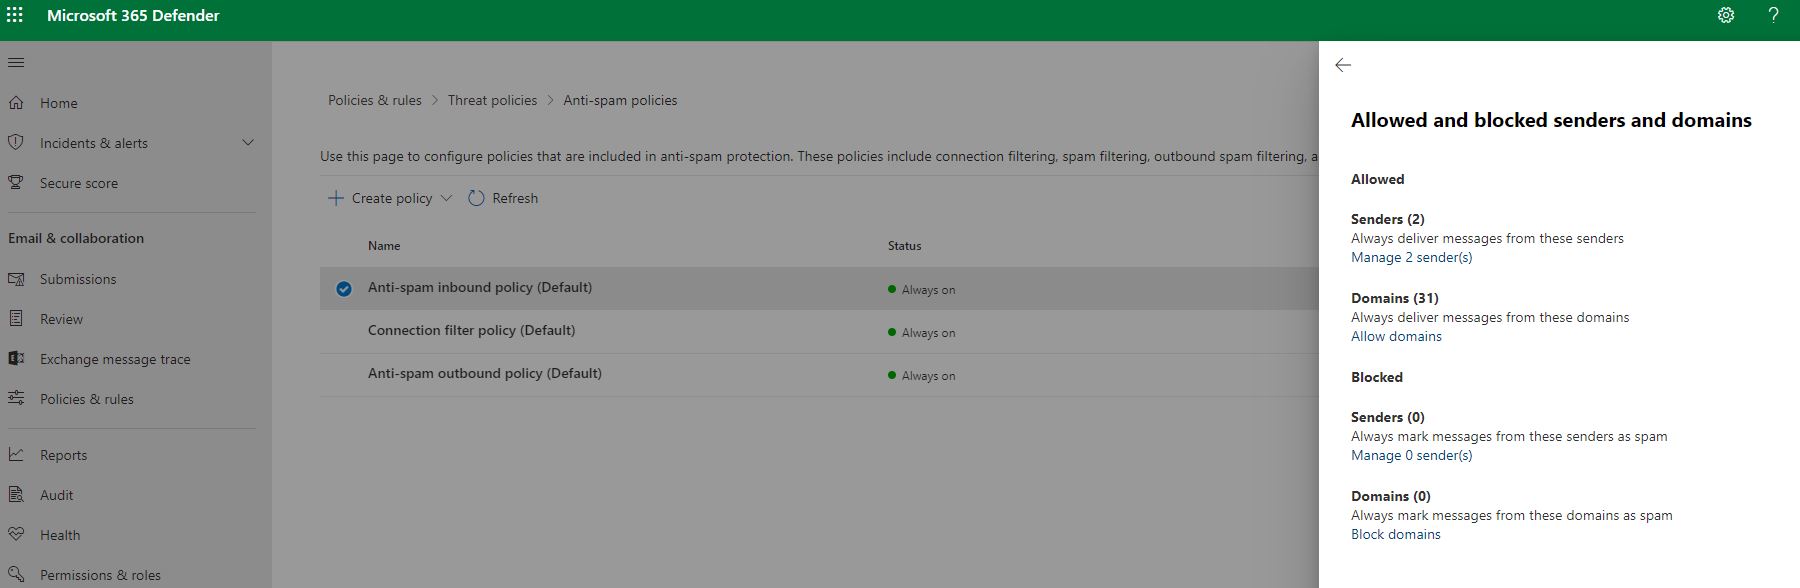
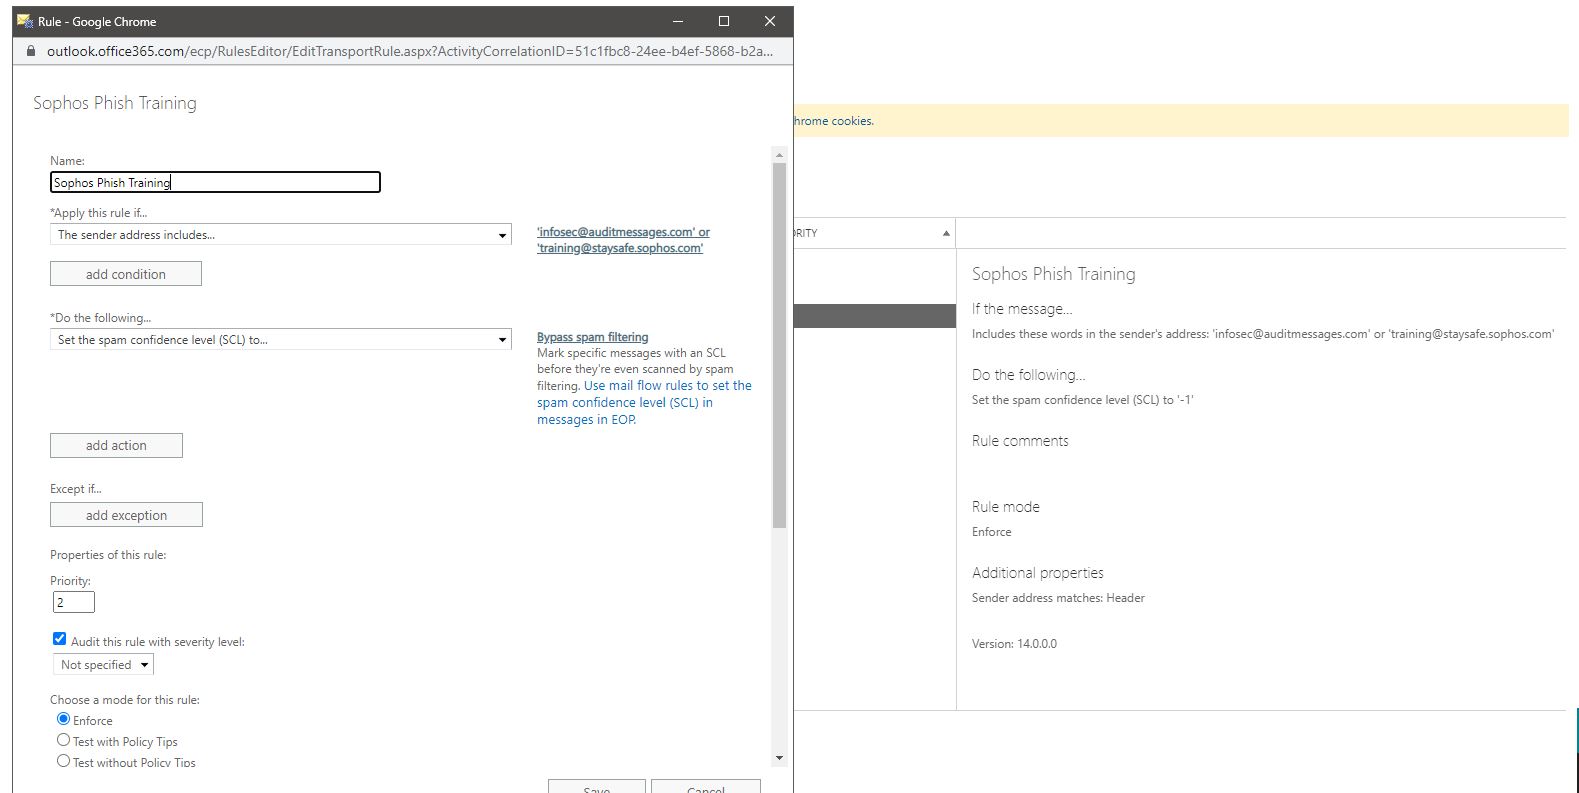
My 3 rules in place to try and allow emails from : [email protected] (one of the Sophos Phish test addresses)
-
Sophos Phish Training emails being quarantined by Office 365 :(
kennysarmy replied to kennysarmy's topic in Cloud Services
If anyone can help analyse the message header I could send one via PM -
Sophos Phish Training emails being quarantined by Office 365 :(
kennysarmy replied to kennysarmy's topic in Cloud Services
>> Also, how do you know which domain a certain campaign is going to be sent from? When you create the campaign there is a section to choose the email address of the sender. I've been doing all my testing with it set to : [email protected] I think I've managed to get it so that the training email address is unfiltered - but I can't see to get the same for the [email protected] emails. YET! -
Sophos Phish Training emails being quarantined by Office 365 :(
kennysarmy replied to kennysarmy's topic in Cloud Services
We tend to do a few weeks of training then a simulated attack. The emails advising of the training come from : [email protected] -
Sophos Phish Training emails being quarantined by Office 365 :(
kennysarmy replied to kennysarmy's topic in Cloud Services
Advanced Delivery set to allow Sophos sending domain : auditmessages.com Still gets trapped
-
Sophos Phish Training emails being quarantined by Office 365 :(
kennysarmy replied to kennysarmy's topic in Cloud Services
I've managed to get to the advanced delivery part of MS Security: https://security.microsoft.com/advanceddelivery?viewid=PhishingSimulation But it only seems to allow a max. of 10 sending domains. Sophos Phish Threat seems to have a lot more than 10 https://support.sophos.com/support/s/article/KB-000037983?language=en_US#anchor3 What to do To ensure successful delivery of Phish Threat emails, include the following IP addresses in the allow list: 54.240.51.52 54.240.51.53 The domains below must also be allowed in your environment to ensure the successful completion of your Phish Threat campaigns. Domain name auditmessages.com bankfraudalerts.com buildingmgmt.info corporate-realty.co court-notices.com e-billinvoices.com e-documentsign.com e-faxsent.com e-receipts.co epromodeals.com fakebookalerts.live global-hr-staff.com gmailmsg.com helpdesk-tech.com hr-benefits.site it-supportdesk.com linkedn.co mail-sender.online myhr-portal.site online-statements.site outlook-mailer.com secure-bank-alerts.com shipping-updates.com tax-official.com toll-citations.com trackshipping.online voicemailbox.online -
Sophos Phish Training emails being quarantined by Office 365 :(
kennysarmy replied to kennysarmy's topic in Cloud Services
Microsoft 365 Defender portal - don't have access to the settings they state. No subscriptions found Before you can start using Microsoft Defender for Endpoint, you need to subscribe to the service SeeMicrosoft Defender for Endpoint product siteor contact your Microsoft account team for information. Already subscribed to a trial or commercial license? Microsoft Defender for Endpoint license settlement can take up to 30 minutes. Please try to log in again later. Need further assistance? Contact support Click here to retry now