Roberto
-
Posts
2,734 -
Joined
-
Last visited
Content Type
Forums
News
20th
EduGeek EDIT Conference
Blogs
Everything posted by Roberto
-
Sage advice, this. Chromebooks are very good at what they do, and not so great at being “a cheap alternative to windows devices” if you’re unwilling or unable to move from windows-centric infrastructure and workflows.
-
> What else? Ensure that the resource can only be accessed by a trusted account using a trusted device. E.G. with Microsoft's conditional access, I'd implement MFA and also require the device to be Azure AD joined or Hybrid Azure-AD joined. If you wish to use mobile devices or (again, staying with the Microsoft nomenclature for now) their laptop is managed in Intune, you can also require the device itself to be compliant with MDM policies.
-
If only there were other options besides "bulled to a shine that any sargeant major would be proud to use as a shaving mirror" and "filthy"...
-
Intune Remove solitaire and casual games and Xbox Applications
Roberto replied to cheekycharly's topic in Cloud Services
Yes. I’ve been really pleased with this approach. Much easier to manage whenever anything changes than the script method. -
Windows batch converted .txt files to .xml
Roberto replied to TeachGeek1's topic in Windows Server 2016
Are you not backing these files up? It seems to me that a quick look at backups from before the files were changed will tell you everything you need to know about their correct format, etc. Not to mention that you can presumably just restore 99% of the files there? -
This post seems a little confused. Firstly, we don't really have "primary" and "secondary" AD domain controllers. You might have two AD DCs that you refer to as "primary" and "secondary" but outside of a few edge cases that don't apply here that distincition doesn't really help technically. Next, as for DHCP. Again, this isn't inherently a part of AD as such, so while it is common in small to medium operations to put the DHCP service on the domain controllers, the fact that they are domain controllers and DHCP servers isn't really relevant. If you have the DHCP server role installed on both ADDCs and need to understand how to make DHCP redundant/failover between the two, I'd reccomend a quick read of the microsoft and server fault links I'm pasting below for you: https://learn.microsoft.com/en-us/previous-versions/windows/it-pro/windows-server-2012-r2-and-2012/dn338978(v=ws.11) https://serverfault.com/a/368517
-
Just be sure you read what’s affected carefully, this is around O365 group creation and a surprising amount of features use O365 groups in the background. We (not edu) ended up having to turn this feature back on but added a suffix to user-created O365 groups to make them manageable l
-
Changing domain FQDN - Has anyone done it?
Roberto replied to NewFormz's topic in How do you do....it?
Did you read the bit in that guide where it says not to do it in prod? -
Andrew Tate and school filtering
Roberto replied to sigma's topic in Internet Related/Filtering/Firewall
Been out of edu for a while now but when I was in, we used to use our service desk for these requests (along with everything else of course). It gave us a method to track requests in the moment as well as a way of reporting on them monthly and reviewing issues when debating changing our filtering platform. -
Microsoft Entra ID - The new name for Azure AD...
Roberto replied to Cat_Jam148's topic in Cloud Services
As I've said elsewhere, this is necessary. Active Directory is a legacy product. While it’s going to be around for a long while yet, it’s effectively deprecated. So there's no need or benefit to associate EntraID with Active Directory. And you don’t need to have all your services in Azure to run idp in AAD/Entra ID, so 'Azure' is unnecessary here. I've been in plenty of meetings when senior IT staff have been confused as to the difference between "AD" and "AAD", and these are not stupid people by a long chalk. This is an intentional attempt to break any link, any idea that AAD is just ’AD in the cloud’. It’s not. It has always been a different product and riding on the coattails of AD via name association no longer. This is part of the journey to on-prem AD being something MS did in the past, not something they have to support in the future. -
Have to remove hikvision from network - any alternatives?
Roberto replied to pooley's topic in Physical Security
Yep. If we're going to panic and boycott everyone who has ever had a security exploit then we might as well give up on computers, issue everyone with an abacus instead and pray no-one with woodworking tools finds out. -
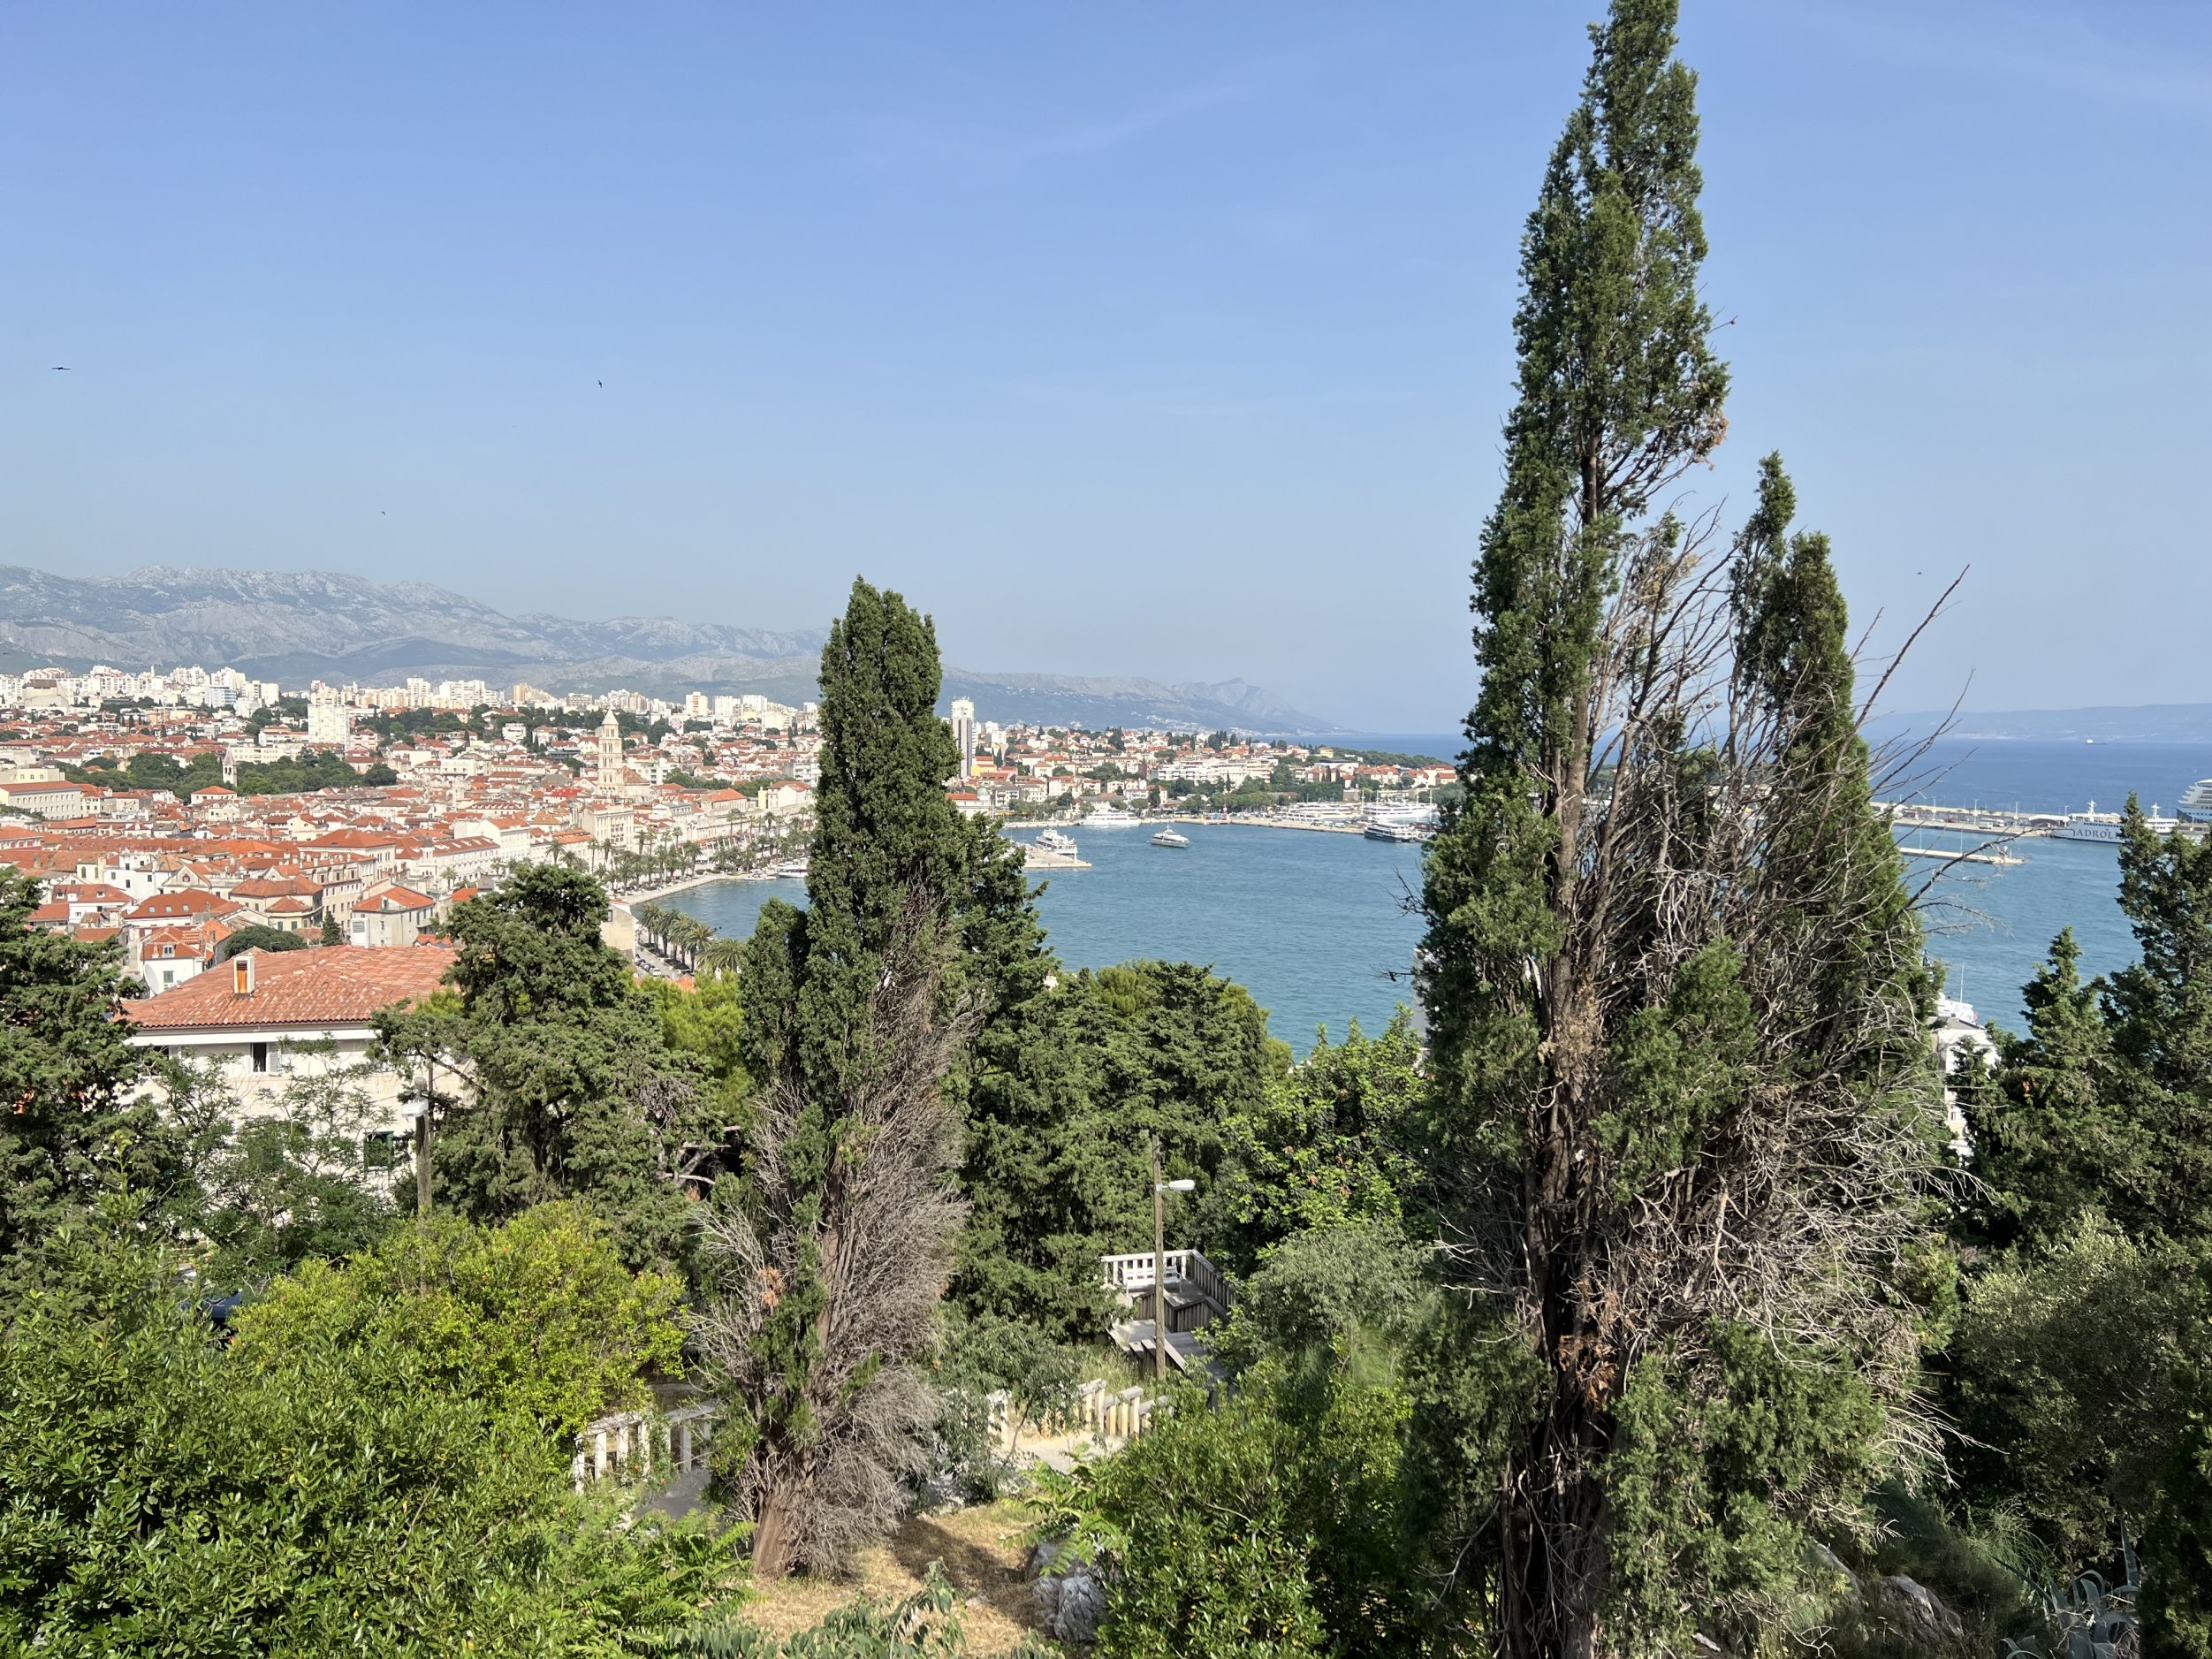
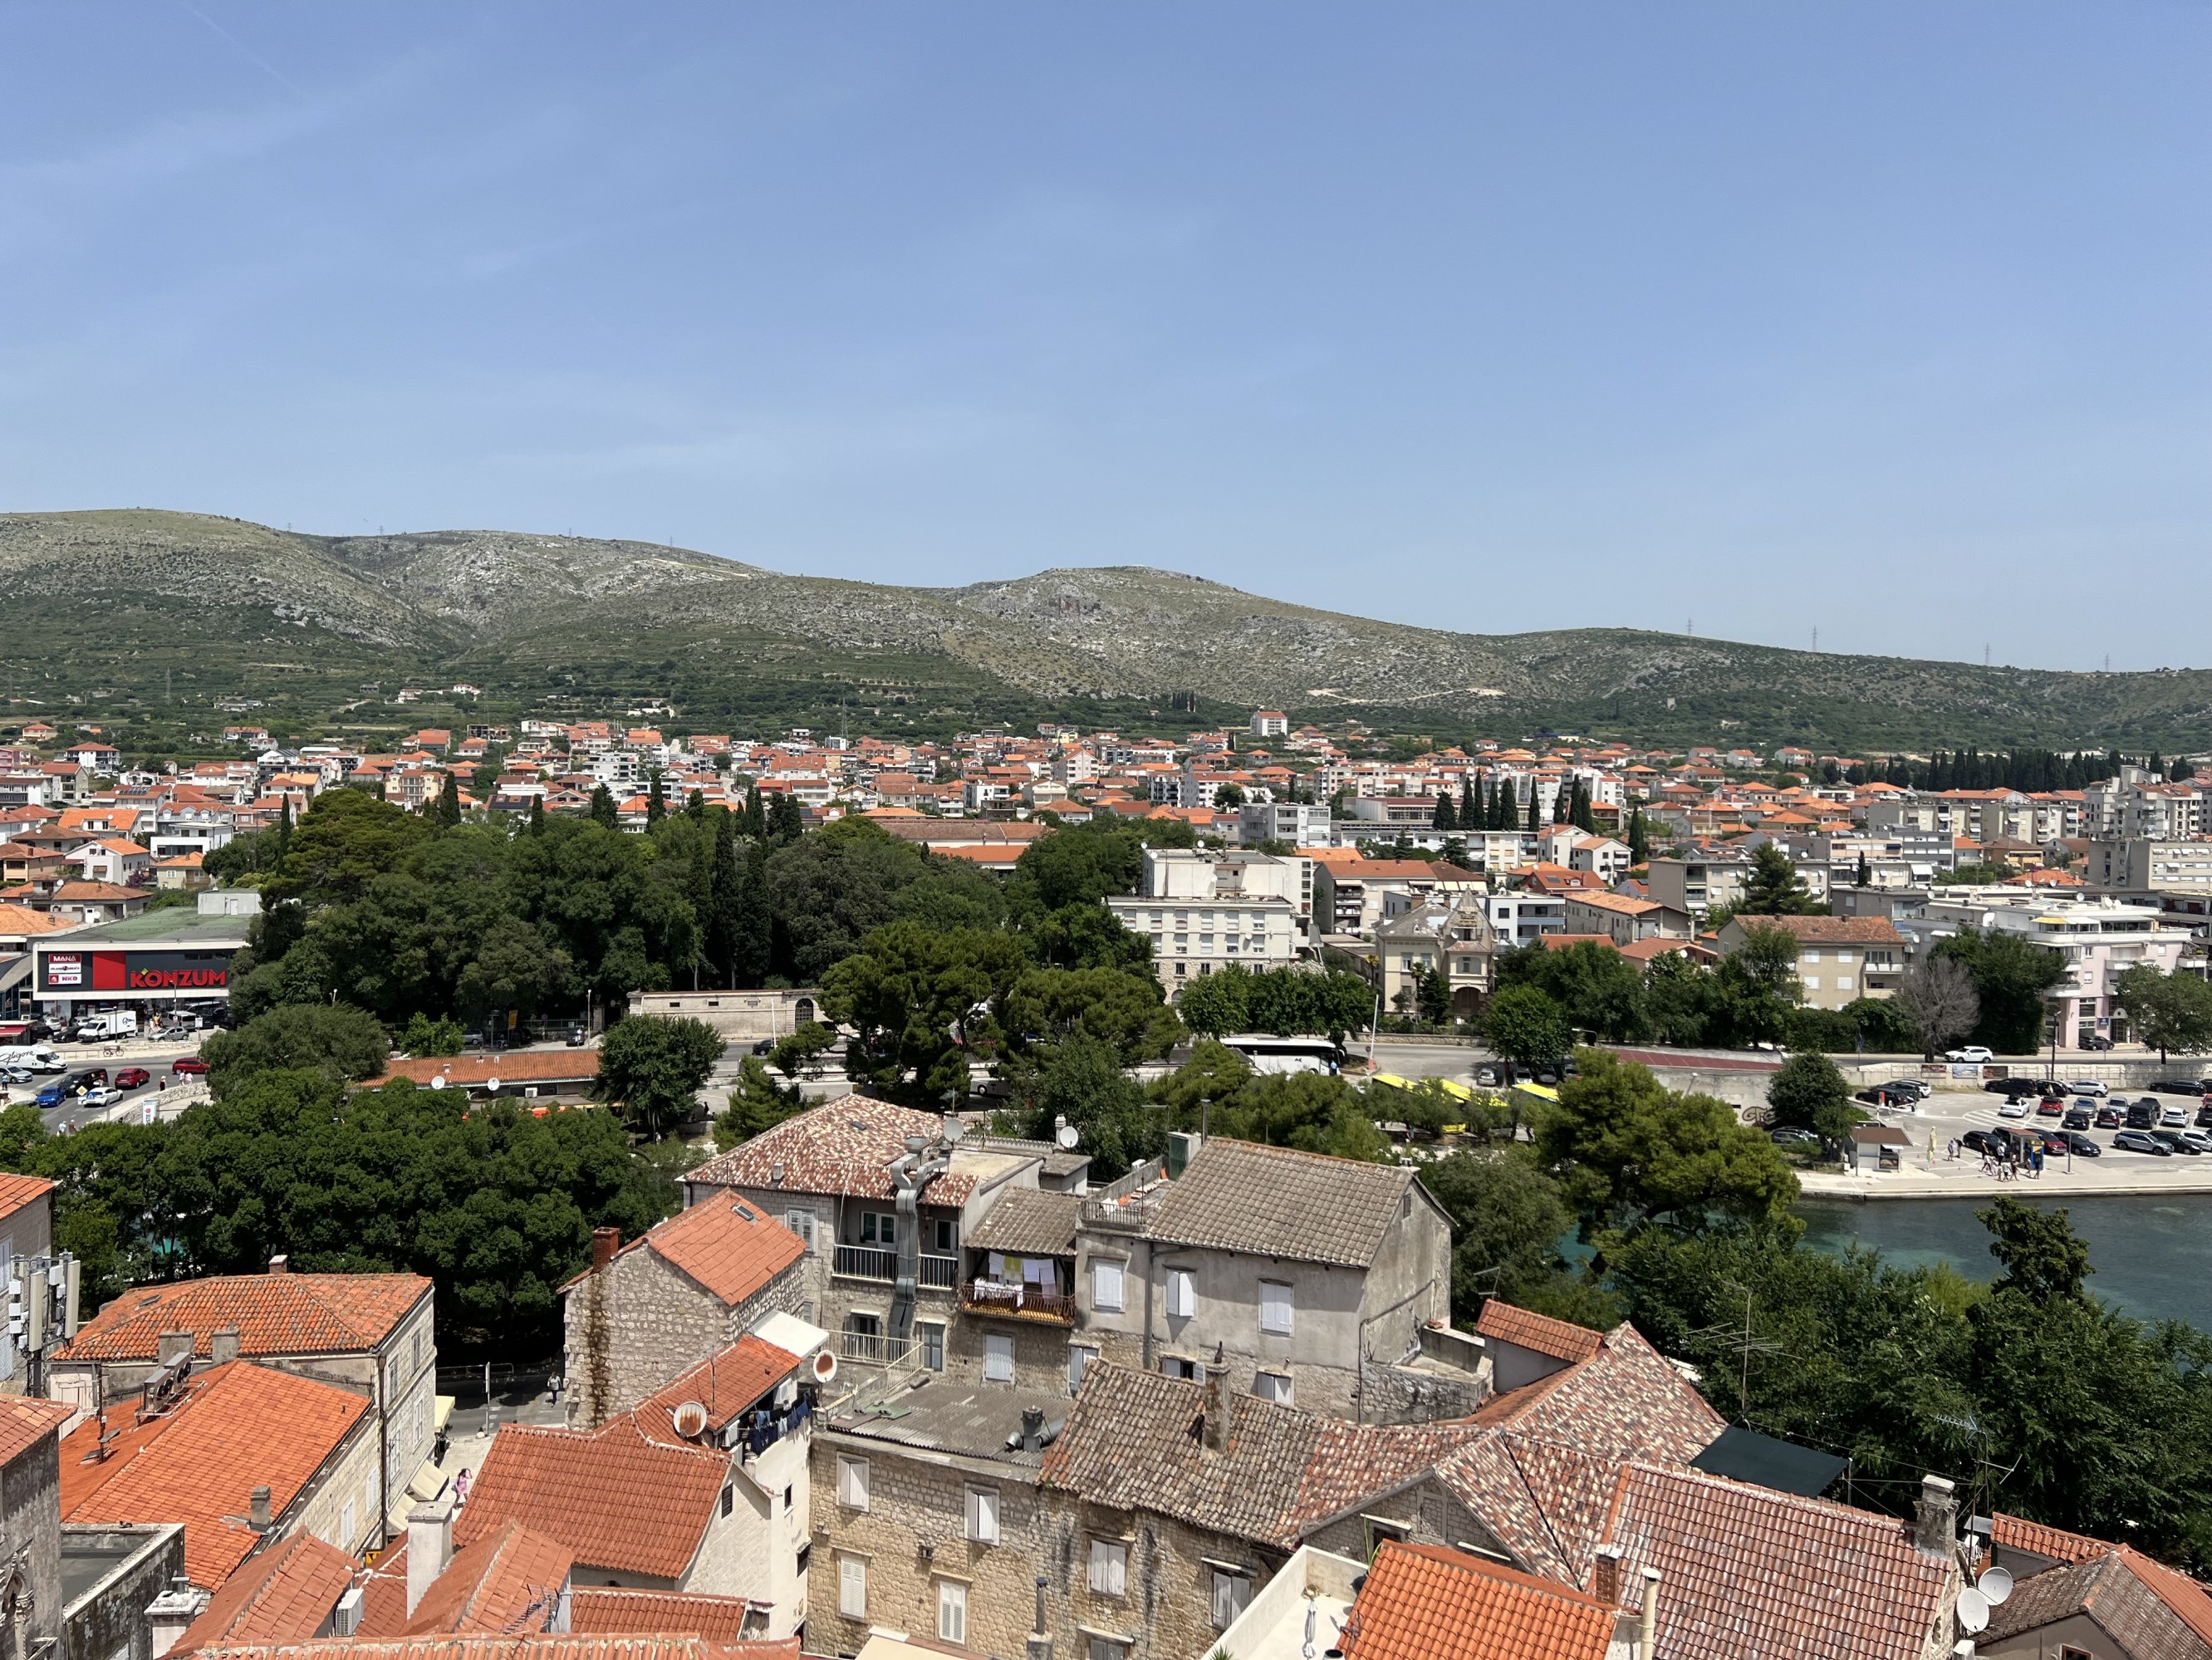
I’m not really a photographer but I’m quite pleased with this view over the harbour in Split. And this view of the mountains from Trogir cathedral clock tower , nearby

-
I wouldn't think it completely outrageous for an A-level film studies course to involve a bit of film watching and critique, nor a course in sports studies to involve watching or playing a bit of sport. As such, it doesn't seem outrageous that an esports lesson might need access to actual esports. I'm old enough to remember the raised eyebrows at the idea of computers in classrooms - my upper school had one in the whole campus and it only rarely featured in our computer science classes. These days there's probably at least one computer in every classroom - besides the phones in pockets and bags, I mean.
-
How much of this is the LEA "holding back teaching and learning" and how much of this is the schools just YOLOing into running the courses with inadequate planning and notification?
-
Mahvc's point is very relevant. The Why matters. How will success be measured? That starts with understanding the why. You've heard about SMART goals for people management right? Project requirements like this could use the same SMART methodology. The 'why' is why generic plans may not be helpful. A MAT looking to reduce captial expenditure on central services shared across all its schools may have a very different set of reasons and success criteria for running a cloud project to a single school looking to reclaim a server room to be a office or something. I'm going to talk about Microsoft services below as those are the ones I'm more familiar with and you mention them yourself, but alternatives are available. You've also hit on a major point in your description so you're doing quite well. "Migrating to the cloud" should mean using appropriate cloud services instead of simply forklifting on-prem servers into Azure or AWS or whatever. Looking at moving file shares to Sharepoint Online/Onedrive rather than a file server that you've set up in an Azure VM, migrating email to Office 365 (vs. installing an exchange server of your own in Azure) is already a good model. And one that passes quite a lot of people by. You're going to need to spend a fair amount of time doing discovery - making sure you know exactly what apps are running on your network and what those apps will and won't work with. Looking at file shares as an example, its easy to imagine a legacy app that wants to write to a file share and won't play nice with a sharepoint document library or whatever. You may be able to work around that with Azure file services or it may be that you end up with a few servers still on-site for legacy apps. You may have some areas (e.g. if you have a class that does video editing) that needs fast storage and won't cope well with the latency inherent in a web connection. These again may need to be an exception. Lastly, don't forget to get "must be compatible with our cloud solution" inserted into any current and future software and services contracts your org has. You can't do much about old legacy stuff that simply won't work with a modern platform but you can make sure you don't buy anything new that won't work for you!
-
YOLOing your way through the signup for Netflix or whatever at home and then being surprsied they won't let you share passwords any more is one thing. And yes, I'm guilty of that myself at times at home when I think the service is trivial- but doing the same for a contract for business broadband is an absolute failure on the part of whoever agreed the deal on behalf of the school. I absolutely read business contracts like this and you should too. And this is why.
-
Would you join a Professional IT Association?
Roberto replied to Kitkatninja's topic in General Chat
All of those are in line with what I would expect experienced IT Professionals to earn. 10 well established engineer/coders, for example; 4 senior engineers/coders; management structure up to CEO level. Nothing "obscene" here imo. -
Would you join a Professional IT Association?
Roberto replied to Kitkatninja's topic in General Chat
Well this is the thing. Quite a lot of organisations (not just edu) don't appreciate the high cost of doing things properly until they've tasted the higher cost of getting it very wrong. Putting aside the question of what such accredation may look like, its not unreasonable. A solicitor may have a number of assistants working for them who are not fully qualified legally, whose work is constrained by guidelines and overseen by the solicitor - a large conveyancing office might have lots of people who are well respected experts at certain aspects of what that office does without being a solicitor. As you allude to, you don't need to be a chartered engineer or architect to mix cement or carry bricks on a building site, etc. What might be interesting is if having some kind of "accredited IT person" in a management role who was able to sign off on various aspects of the org's IT security position might be required for Cyber Essentials Plus, or would get you a reduction on cyber secutiry insurance premiums, etc. You're also right about education not wanting to pay £30 an hour. That's why I left. I would suggest in a larger academy trust, at least, there may be a call to have one or two highly paid experts providing expertise (and a career goal to aspire to?) centrally for the schools and colleges inside the trust. This links back to the discussions in the devaluing of IT jobs thread again of course: WRT certifications/qualifications/accreditation - an arguement could be made that your employer is never going to value you more highly than you value yourself, which is another reason to tick the box on certs etc. whenever you can. Especially if you already have 90% of the criteria ticked by just doing the job you're already doing. -
Would you join a Professional IT Association?
Roberto replied to Kitkatninja's topic in General Chat
CS and ICT are very much different fields and both are necessary. This is an over simplification I know but just because the study of physics is a thing, that doesn't mean we don't need mechanics and electrical engineers who are expert in the applied principles. I'm a BCS CITP fwiw and I do strongly believe in the overall message - I see lots of people who work in IT complaining that the "IT Profession" is not taken seriously. That's a valid criticism but equally there needs to be a will and a way to 'close the circuit' on our end too and I see professional organisations with guidelines, training and standards baked in as a way to do that. A way to raise the level of the IT Profession as a whole, as well as the individuals within the profession. This isn't about saying that people who are not currently in a professional association are not behaving professionally, rather that joining one is a way of underwriting the standards and professionalism you already have. -
What words do you (or someone you know) say incorrectly...?
Roberto replied to Koldov's topic in General Chat
It’s “sequel” to me when spoken, sorry. -
This feels like it might not be a great test. Either the PCs are not used enough for any testing to be statistically significant (how will you ensure 'testing' on these devices will actually cover all your use cases if they're hardly used?) or they're used just enough for people to be really annoyed at the change in user experience between them and other devices, at which point they'll either avoid those devices or complain constantly about the UI being different...
-
I think the share point migration manager can do it for/with you https://learn.microsoft.com/en-us/sharepointmigration/fileshare-to-odsp-migration-guide
- 5 replies
-
- 1
-

-
- microsoft
- microsoft 365
- (and 2 more)
-
'Disappointed' bidder sues MAT after MIS Tender failure
Roberto replied to vikpaw's topic in MIS Systems
Interesting update via LinkedIn. It seems United Learning’s request to appeal was dismissed, and quite emphatically so. https://www.linkedin.com/pulse/follow-up-blog-united-learning-trusts-appeal-langbrook-finance?utm_source=share&utm_medium=member_ios&utm_campaign=share_via Well worth a read if you’re involved in procurement. Reflecting on some of the earlier posts about how terrible Bromcom was for bringing this case, I wonder if attitudes might have changed now that a court has so comprehensively found in their favour. I was a little surprised at the tone of some of the earlier comments - I think complaints about the case being brought against UL have aged badly. The education field ought to have known about procurement regulations and standards for quite some time now - I remember getting some training on this about 15 years ago when working on proposals and quotes for LSFC's new campus for example, and having to go through the OJEU bid process for some parts of that due to the size and complexity of some of our RFPs so the necessity for frameworks and for following them properly really shouldn't be new any more. -
You have some good advice here already. I’d add that you’d want to start with some discovery. Where is their Microsoft tenant located? The answer is probably ‘in Europe’ and that’s fine, but I’d check now and not be embarrassed after the event because you transferred a terabyte of student PII to a tenant that somehow got created in the US. What data is in ‘all the shares’ and how do they need to access it? You would not want to store data in a sharepoint document library if it’s used by some god-awful legacy app that can’t handle that connection. What are the data retention requirements for the data and can (& how will!) you meet those in Sharepoint or Azure files? Will a cleanup of manky 20 year old data from the depths of old file shares need to be part of the process here? How are you ensuring you’re transferring ’clean’ files from a malware perspective? Those are a few of the questions I’d need answers for before firing up the various migration tools…
- 5 replies
-
- 1
-
-
- microsoft
- microsoft 365
- (and 2 more)
-
Have you considered doing this the other way around - MFA enabled for all users with an exception group for accounts you wish to exclude? This is "fail safe" - it doesn't rely on someone remembering to add an account to a group when creating the account, so is imo safer. This is good practice as you can't always control when and how accounts are created. Additionally this gives you a very easy method to audit which accounts are not protected by conditional access/MFA and see if any unexpected accounts are not being protected, or even get an alert when this group is modified - https://janbakker.tech/act-on-group-membership-changes-in-azure-active-directory/