Duke5A
-
Posts
1,598 -
Joined
-
Last visited
Content Type
Forums
News
20th
EduGeek EDIT Conference
Blogs
Everything posted by Duke5A
-
 Hipsters?
-
Youbue video's being blocked
Duke5A replied to nicholab's topic in Internet Related/Filtering/Firewall
@LeMarchand You using Google Apps? They have a neat setup where you can run the students through restricted mode while letting staff browse without restrictions. If a video is not viewable to a student then staff have the option of adding it to a white-list that will make it viewable in restricted mode for your domain. This involves DNS redirection and your staff accounts being members of the approved teachers group in Google Apps. https://support.google.com/a/answer/6214622?hl=en I set it up here a couple years ago and it works great. -
I wouldn't worry about the number of printers in the GPO. I've got 57 in mine and this GPO is attached to the root of our user OU, so it's processed for all students and staff. Verbose processing is turned on, so I can see what Windows is working on through the logon process. Printers is up for only a short period of time, and if the user doesn't qualify for any printers it's just a blip. Number of printers in the list that the user doesn't qualify for doesn't seem to have any bearing on logon time.

-
This might be some help: VB script for creating student drop boxes - Blogs - EduGeek.net It's a blog post I wrote a few years ago concerning drop folders along with a script to do the creation and security settings.
-
Place the GPO on the user OU and use item level targeting on each printer to selectively deploy them - in this case you can specify that the computer the user is logging into must be in a particular OU to receive the printer. The policy runs for all users, but the printer is deployed only if conditions are met. Using a print server? When adding a printer to GPP select 'Shared Printer' and not 'TCP/IP Printer'. The only thing you should need is the share path to the printer, nothing with the port/IP.
-
Bulk remove security groups from users in OU
Duke5A replied to Shadow_Walker's topic in Windows Server 2012
This will remove all security groups from all users contained within a specified OU with the exception of the 'Domain Users' group. Be sure to test this on a few temp users before releasing it into the wild. Import-Module ActiveDirectory $users = Get-ADUser -SearchBase "OU=Students,OU=Users,DC=domain,DC=com" -Filter * foreach($user in $users){ $groups = Get-ADPrincipalGroupMembership $user.SamAccountName | Where-Object {$_.name -NotLike '*Domain*'} foreach($group in $groups){ Remove-ADGroupMember -Identity $group -Members $user } } -
What do you need it to do that the built-in print management console can't? If you're looking for logging that doesn't make your eyes bleed then Papercut offers a free logging app that creates a web accessible log that is easy to read.
-
I think @mrbios was on to something mentioning security rights on the printers. A little while back I experienced this issue with a single print queue that I had altered the rights for - I removed everything except a single user account and administrators. What resulted was the printer would come and go almost at random. I could refresh policy and it would show up again sometimes and disappear the next. User laptop was running Windows 7 with a local profile. After adding 'Everyone' back to the list it stopped disappearing. All of the other printers on the print server have the default security rights setup. I can't recall where I read it now, but on a tech blog there was mention of Windows sometimes using computer credentials when adding printers initially.
-
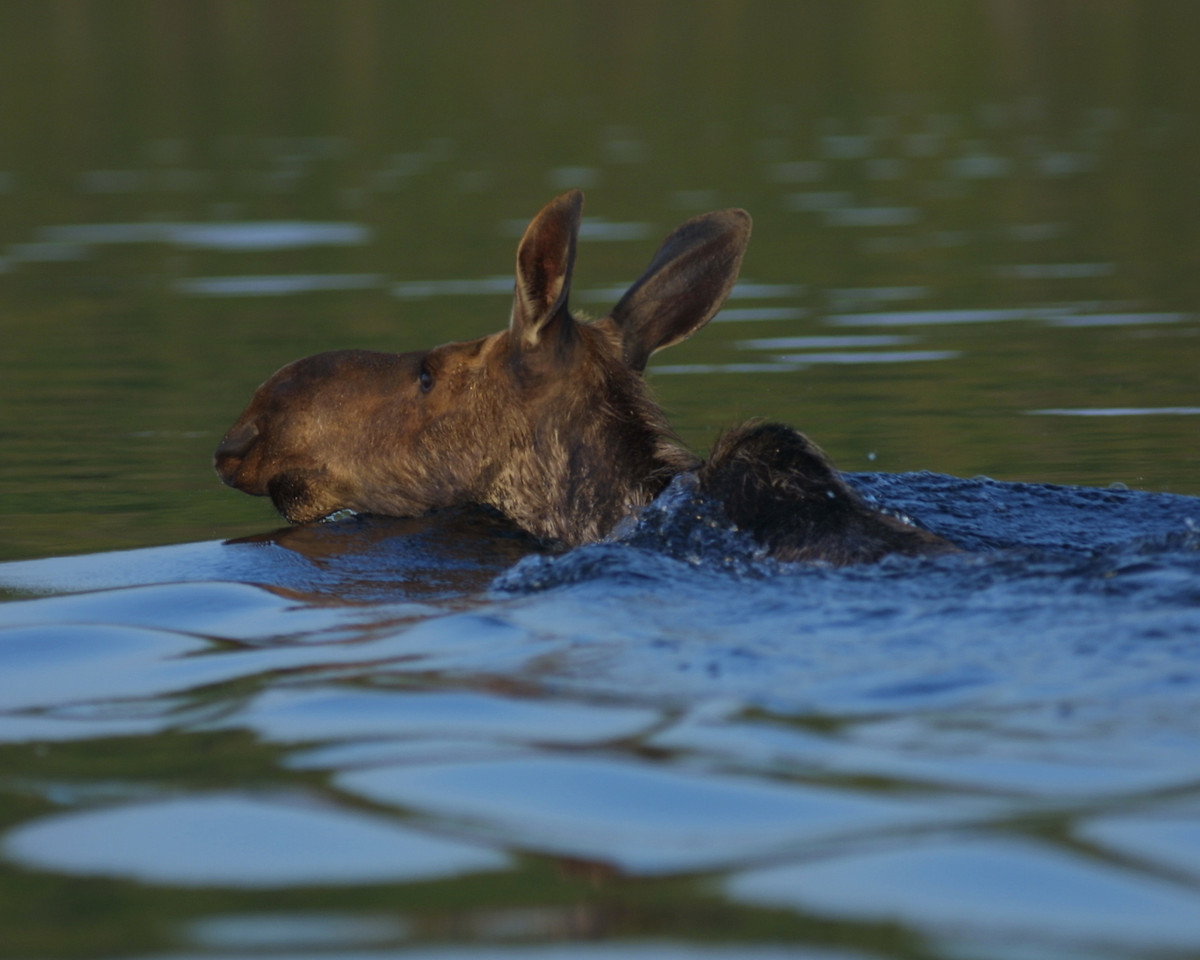
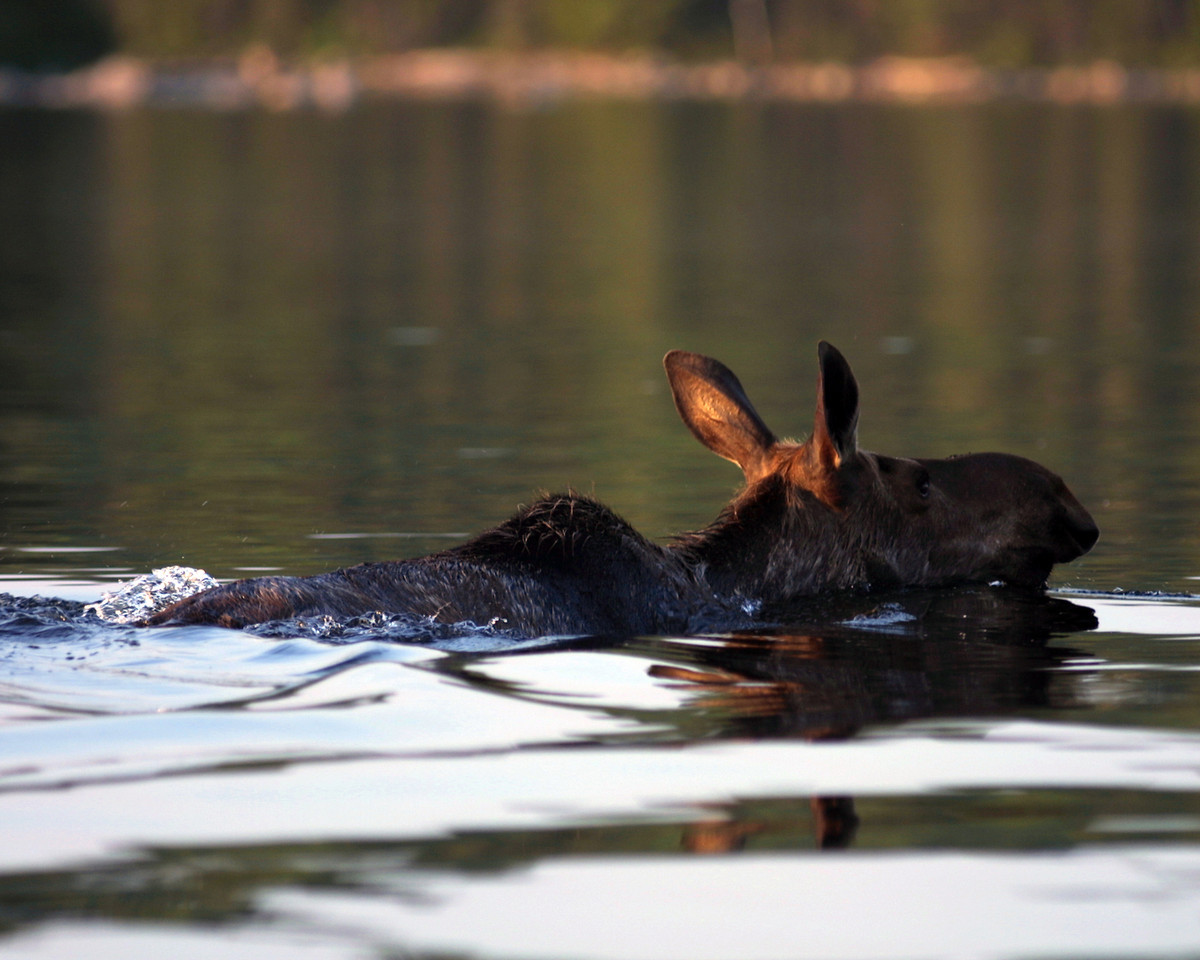
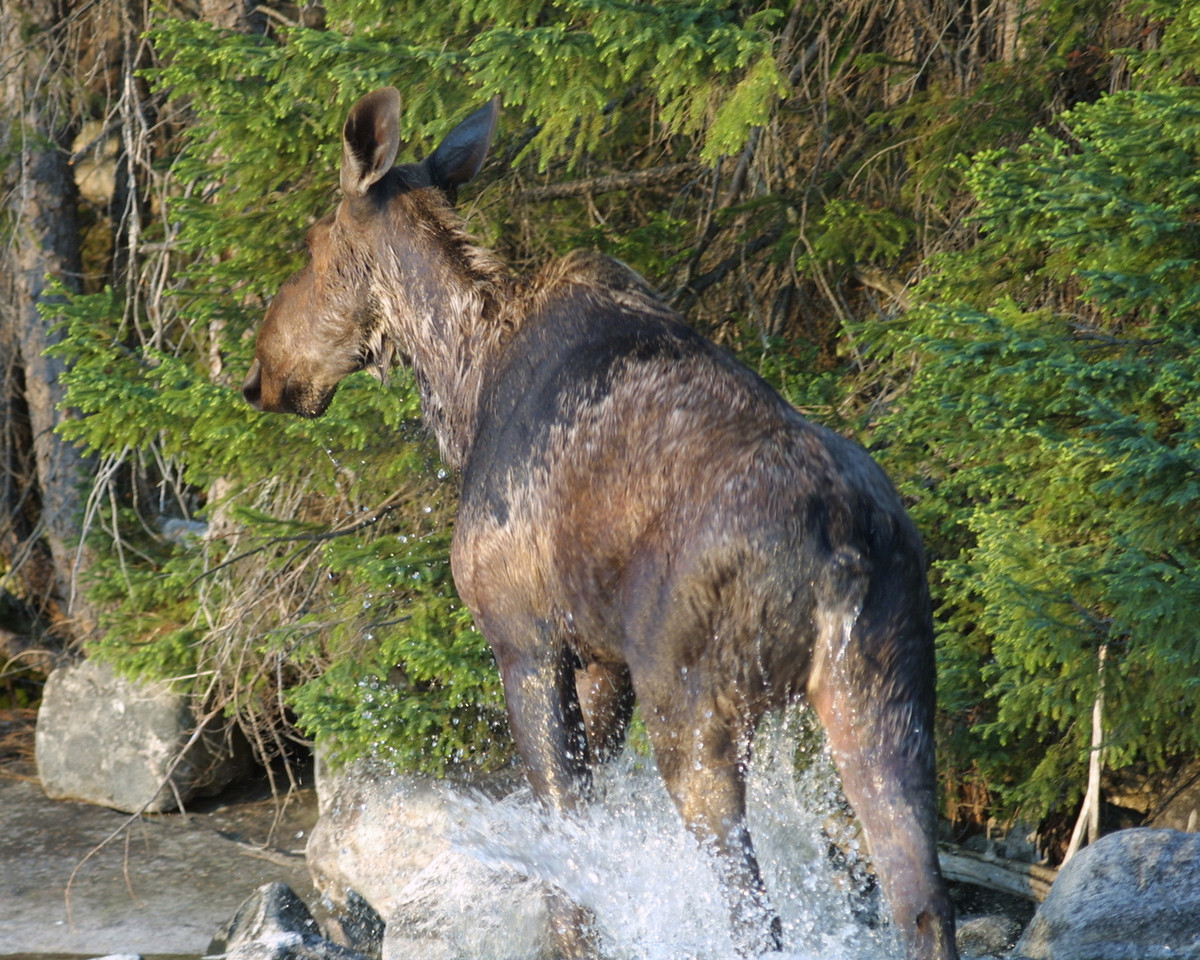
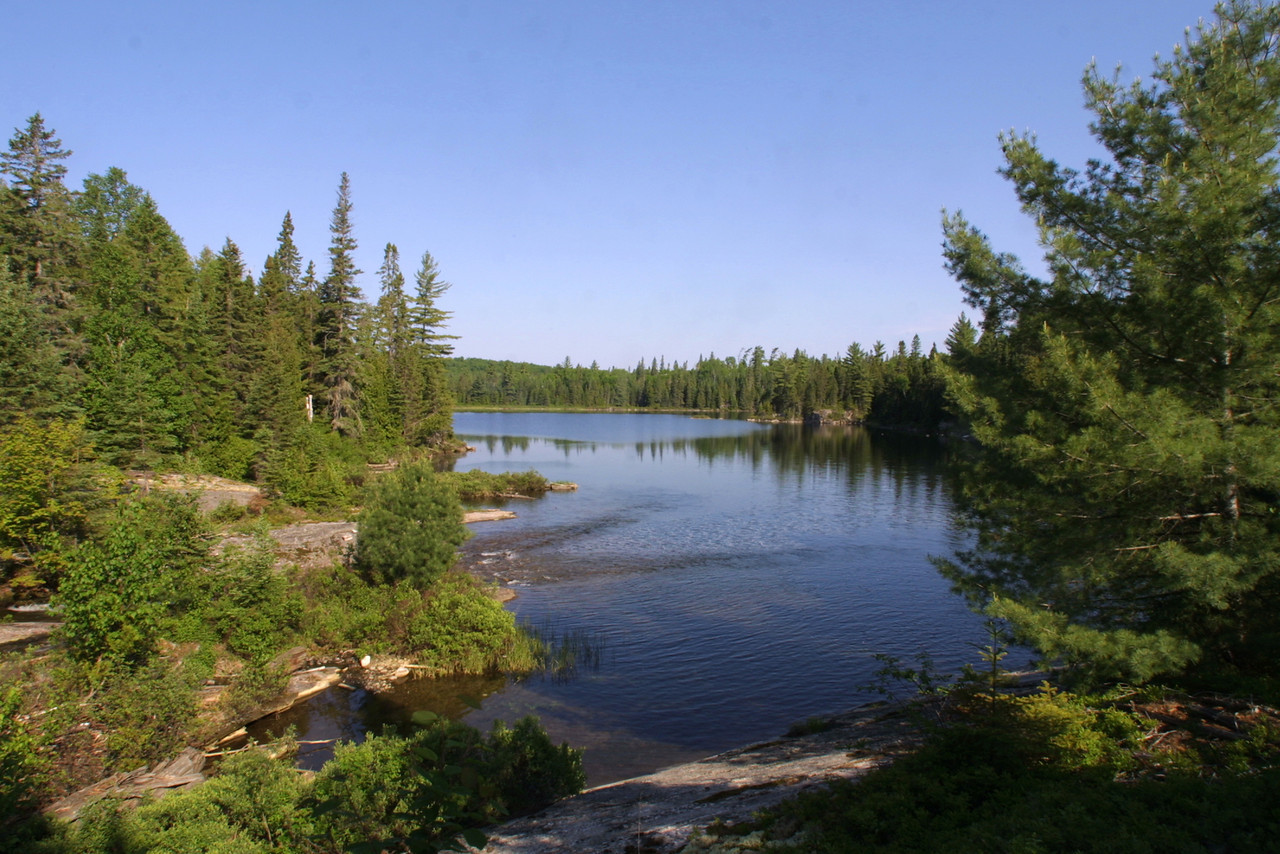
I am in absolute awe of many of the photos here. @jbunoomally and @SteveM555, absolutely stunning work. I need to get out into the world some more. Time is hard to come by with work and family obligations though. I run a side business as a sports photographer, but would love to branch out into stuff like this. Back when I was first getting into the hobby my Dad took me to Quebec on a hunting trip. We stayed at a camp called Camp Coucoushee on the northern tip of Lac Kikwissi. It was run by a second generation proprieter by the name of Serge. The place opened in the 1950s. I don't even know if it's still operating as Serge was in his 70's the last time I was there. https://www.google.com/maps/dir/Syracuse,+New+York/Chemin+de+Maniwaki,+Rouyn-Noranda,+QC+J0Z,+Canada/Unnamed+Road,+Rouyn-Noranda,+QC+J0Z,+Canada/@47.0425389,-78.5649399,1998m/data=!3m1!1e3!4m15!4m14!1m5!1m1!1s0x89d9f39bbf979a0d:0xd50ce2d7ad9545!2m2!1d-76.1474244!2d43.0481221!1m5!1m1!1s0x4d286d43bbf409d1:0xfae5467d663b76d!2m2!1d-78.945647!2d46.7459663!1m0!3e0?hl=en I had a piece of junk Canon D30 that would hold enough of a charge for maybe 30 photos and a 300m F4L lens. We were on our way back from fishing and came across a moose swimming across the lake. I'll never forget this moment.
-
Android Music Player Recommend Me - but with specifics...
Duke5A replied to SpuffMonkey's topic in General Chat
Another Power Amp user here. Never used it on something as big as a tablet though. -
Oh wow, I feel your pain! That is the backbone of my wireless network right there. With no funding in sight I've taken to purchasing 2960S switches and 1142 access points off of eBay. The 4404 controllers will support those access points and it at least gets you 802.11n at 300Mb. How many devices are associated to your access points when things are mind numbingly slow? Anything over 20 and performance drops like a lead sinker after that. If you haven't done so yet, disable all the 802.11b data rates on the controller. This greatly increased speed for us when it was done.
-
Number one is not an issue as Item Level Targeting can be done on OU location of the computer object as well. You really should look at the options available in it. Number two is only an issue the first time a user logs with a printer that has never touched the machine before. Once the driver is installed it's persistent. This is really only an issue if you're utilizing something like Deep Freeze. Even then this is overcome by either pushing the driver out or building it into your images.
-
I've actually never used the feature to deploy printers through the print management snap-in. I tried it and it creates GPO and places the print queue in 'User Config > Windows Settings > Printer Connections'. This is a pretty old way of deploying printers. Create another GPO and move a couple print queues into it using GPP. 'User Config > Preferences > Control Panel Settings > Printers' I currently have 52 printers in this policy and it's attached to the root OU that houses the user accounts. I use Item Level Targeting on each print queue to further whittle down who gets what. I can't begin to since enough praise for this method. Printer deployment is one of those things that just works. GPP is just one of those things that just works. All my Windows 7 and Windows 10 clients get their printers every single time.
-
We're on LTSB 2016 here and I haven't seen this issue. How are you guys deploying printers? GPP? What is the print server running? After the printers disappear try both browsing to the server and adding the queue manually, and refreshing policy with a 'gpupdate /force'. Trying to add the printer by hand should bring up an error window if it fails. If it fails with GPP it will be placed in the Application log under Event Viewer.
-
Do you have students authenticating non-domain joined devices to wireless using their AD accounts? If no, then there is a better way to do this. I had this exact same problem a few years back where students were using their AD accounts to join cell phones and other stuff to the internal wireless. On the student laptops you can specify to use computer account, user account, or both for authentication on the wireless connection. By default it's set to both and when the device boots it uses computer authentication, and after the student has logged on it passes to user authentication. Set it to strictly use computer and take away the students' rights to authenticate to wireless using their accounts at the radius server. Problem solved. If you allow them to use their account to authenticate personal devices, then what I said above goes right out the window. For modifying the Radius connection policy I would most certainly do it using the management snap-in. I wouldn't know where to start doing this at the command line.
-
Are your staff and student wireless networks on their own VLANs? You can place conditions on the connection policy by originating subnet. That will get you what you need. Another option is to take away the student's access rights to authenticate to wireless using their user accounts and only allow computer authentication. This only works though if they're only using domain joined computers. I used this option in my environment.
-
I've got roughly sixty switches in my infrastructure spread across seven buildings with private fiber between each site. Backbone is 1Gb with managed wireless, 180 IP cameras and lots of other fun stuff. Utilization doesn't top 30% on the building links. With the low cost of used equipment I just keep a few spares of each switch model on hand and purchase off of eBay when I need to. Access switches are mainly Cisco 2950 (100Mb ports with 1Gb up-links), wireless switches are 2960S POE (1Gb ports with 1Gb up-links) and the camera switches are 2960 POE (100Mb ports with 1Gb up-links). This stuff is dirt cheap now and I can count on one hand how many switch failures I've had over the ten years of working here. Paying for a continued warranty just isn't worth the cost and capacity isn't an issue at all. I just point whatever budget I get back at client devices.
-
A colleague enabled scavenging here last week and I just discovered it removed the service record for the KMS server. Existing clients were OK since they have the KMS server cached, but newly imaged machines couldn't activate Windows or Office. Something to look at it if you use KMS activation via DNS discovery.
-
Another vote for disabling it. I don't think I've ever seen it actually fix anything.
-
We have accounts for each student, but also generic for the lower grades. The lowers still tend to use the generic accounts because it's a lot easier to get a class of 30 screaming eight year olds logged on. I have a friend that works a couple districts over and they maintain a list of student accounts and passwords that is available to staff while disabling the option for pupils to change passwords. Their district has a student population of almost 9,000 kids. This may work for you.
-
[1703, cu] AppLocker - Lock, log Off, Shutdown etc not working
Duke5A replied to robyholmes's topic in Windows 10
Last I knew there wasn't any GPO control of what is displayed in the Settings App. My info might be out of date though... -
Chrome is pretty much the gold standard for web developers to test against right now. I've seen too many things break in Edge and IE11 gets goofy with needing compatibility mode on a lot of things. Disable both, Install Chrome and manage it with the GPO templates. If it's a kiosk you could probably even leave the auto-updater turned on. Of all the headache inducing software I have to support, Chrome isn't one of them.
-
[1703, cu] AppLocker - Lock, log Off, Shutdown etc not working
Duke5A replied to robyholmes's topic in Windows 10
I remember having a similar problem when building a Win10 Pro image last year where after messing with App Locker policies the start menu was no longer working correctly. My memory is hazy, but after making these changes to the policy it started working again: Ended up denying access to the store and the new control panel and allowing all other signed apps.
-
Since this post back in March we've moved on to LTSB and it doesn't even include the Windows Store, so I can't confirm if this works on later builds of Windows 10, but here is what the GPO looked like:
-
Just throwing this out there for future reference... Mobility Print works awesome on Chromebooks, but if you're using a proxy then you absolutely have to add this to the bypass list: *rpc.pc-printer-discovery*