-
Posts
577 -
Joined
-
Last visited
Content Type
Forums
News
20th
EduGeek EDIT Conference
Blogs
Everything posted by 5tu
-
Same here in Bucks :-(
-

OOB Update released for Domain Controller LSASS memory leaks
5tu replied to 5tu's topic in Windows Server 2016
Server 2019 - https://support.microsoft.com/en-gb/topic/march-25-2024-kb5037425-os-build-17763-5579-out-of-band-fa8fb7fa-8185-408f-bdd6-ea575ce2fcb5 -
OOB Update released for Domain Controller LSASS memory leaks
5tu replied to 5tu's topic in Windows Server 2016
Apparently not....
-
Out of band updates have been released to resolve the LSASS memory leaks issue on domain controllers introduced by the March 2024 cumulative updates. Server 2022 - https://support.microsoft.com/en-gb/topic/march-22-2024-kb5037422-os-build-20348-2342-out-of-band-e8f5bf56-c7cb-4051-bd5c-cc35963b18f3 Server 2016 - https://support.microsoft.com/en-gb/topic/march-22-2024-kb5037423-os-build-14393-6799-out-of-band-1775cda2-4bb6-43a9-9fd4-ddc3528d3408 Server 2012R2 - https://support.microsoft.com/en-gb/topic/kb5037426-update-to-address-a-known-issue-that-affects-lsass-in-windows-server-2012-r2-eda1002a-4b4d-4c99-8383-b0e2bab5c1d0 From Microsoft: We strongly recommend you do not apply the March 2024 security update on DCs and install the Resolved KBs listed above instead. As this is a cumulative update, you do not need to apply any previous update before installing the Resolved KBs listed above.
-
We're in the process of moving to Microsoft Entra Private Access for this very reason.
-
Yep - doesn't affect performance though.... ....and our devices are talking out to that address.
-
Yes you can as the accounts are being opened in separate tax years. The tax year runs from 6 April to 5 April. Reference: https://www.gov.uk/individual-savings-accounts/how-isas-work
-
What solutions are people using for authenticating pure Azure/Intune managed devices on SSIDs with 802.1x?
-
Also… and I hate to say it, the policies that you realised were incorrectly targeting “All Devices” - what were the settings doing? Not all Intune policy settings get removed from client devices when policies are removed. Same as GPOs. Either a policy to undo settings is required or machines need to be rebuilt.
-
We have the same hybrid management set up and don’t experience the behaviour you’re seeing. The Intune Management Extension on the clients checking in with Intune shouldn’t grind your internet to a halt. What level of traffic are you seeing on your smoothwall when things go south? How are the different workloads set in SCCM? Which ones have been passed over to Intune? How many hybrid clients do you have? Are you deploying apps from Intune to hybrid clients? If so are any failing? Are you using WuFB for updates? Any issues there? Are your certificates on the SCCM/Intune connection valid?
-
Out of interest @localzuk, what are you using for your core now?
-
S2D Failover Cluster - Storage Pool IO Error
5tu replied to robyholmes's topic in Windows Server 2022
I saw a couple of people post in the Patch Tuesday Megathread on Reddit about the Jan 2024 cumulative server updates causing I/O errors on failover clusters. In response, I skipped these updates but have since applied the Feb 2024 ones without any issues. -
Smoothwall not filtering gamepluto.com
5tu replied to 5tu's topic in Internet Related/Filtering/Firewall
@CSmith - I was advised by 2nd line support not to deploy both the "Remove QUIC Header" modification rule and the firewall rule dropping UDP 80/443 traffic. In a remote session the support engineer disabled the content modification rule. Should this be re-enabled? Following recreation of the firewall rule, I am evaluating student access to the gaming websites identified. Due to pressure from school leadership I had to employ other solutions to block access to known sites, so now need to remove these in order to observe the behaviour with just Smoothwall filtering in place. -
[ms office - o365] Old version of Teams with Office 365
5tu replied to mitchell1981's topic in Office Software
Same issue here -
Smoothwall not filtering gamepluto.com
5tu replied to 5tu's topic in Internet Related/Filtering/Firewall
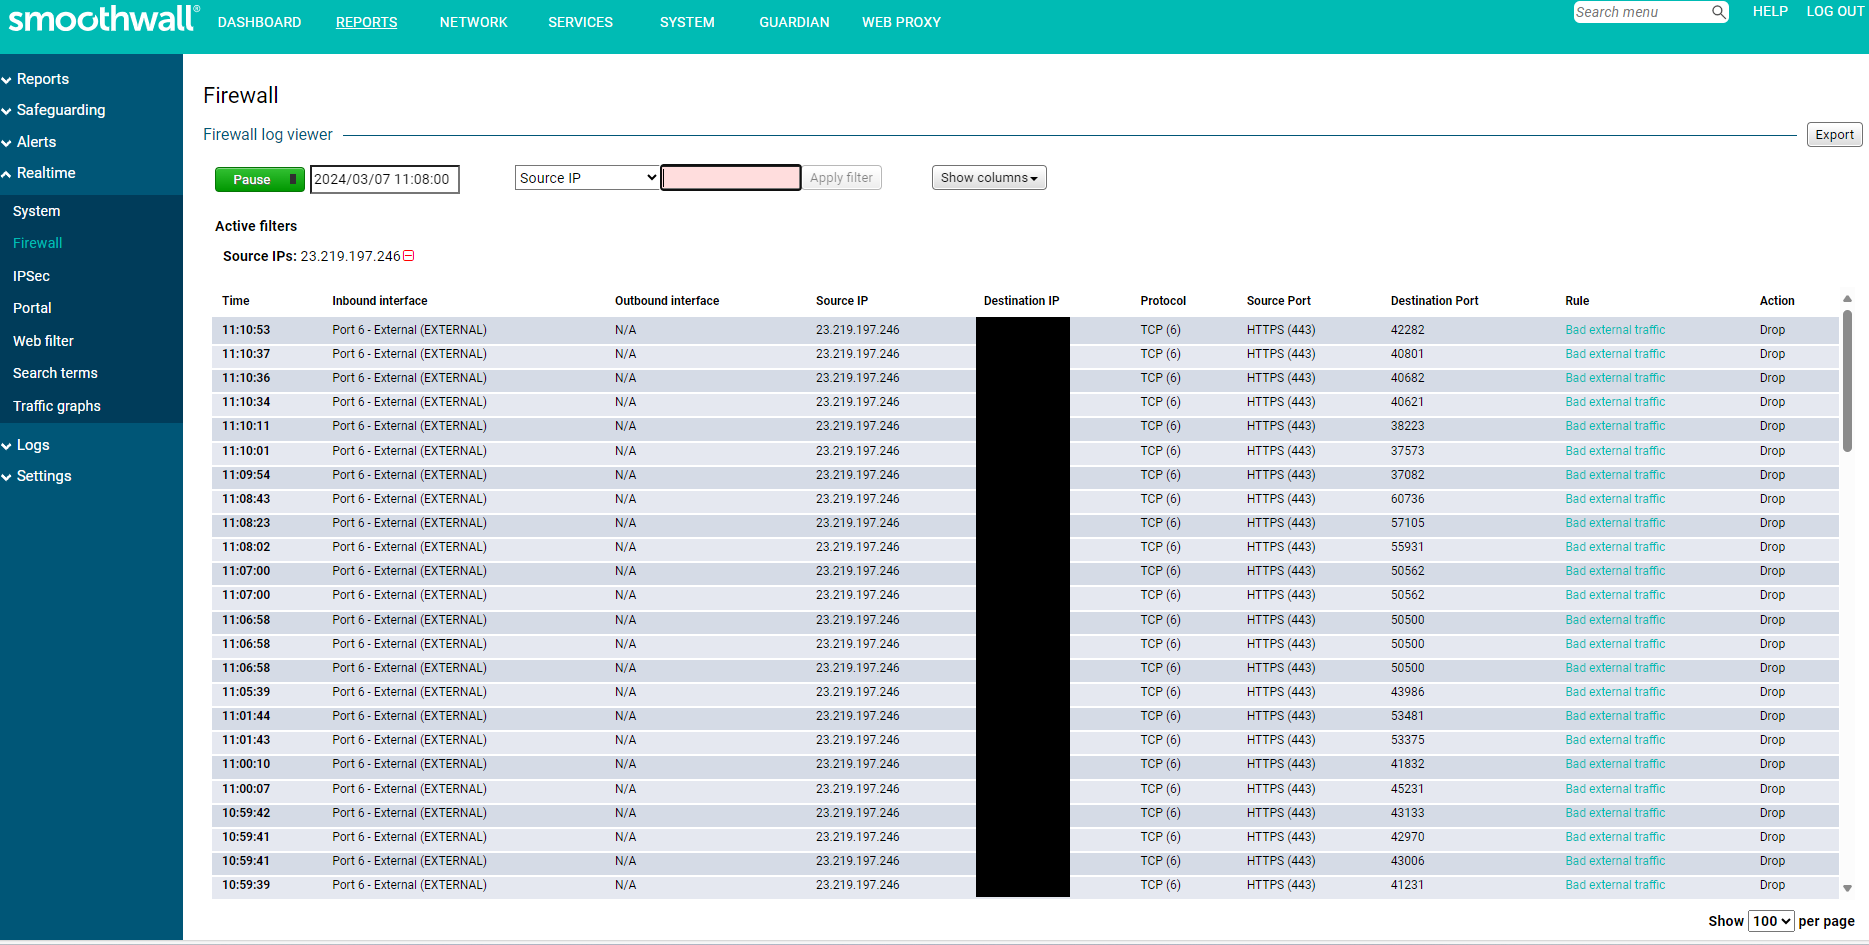
Plot thickens..... I recreated my firewall rule which drops QUIC exactly as it was before (same settings and same rule position, 1) and now I can see it taking the appropriate action in the realtime firewall logs. I even took before and after screenshots of my firewall rule to double check everything. More testing needed but we're maybe making progress (and I'm thinking I need a better firewall). -
Smoothwall not filtering gamepluto.com
5tu replied to 5tu's topic in Internet Related/Filtering/Firewall
Thanks for the suggestion. I've just manually disabled QUIC in Chrome on my own PC and now I do see the Smoothwall mitm certificate being applied on google searches. My understanding was that dropping UTP 80 & 443 at the firewall and/or applying the "Remove QUIC Header" content modification rule was all that was needed to avoid this problem? That is also the understanding of Smoothwall support (so far...) @tom_newton - thoughts? -
Smoothwall not filtering gamepluto.com
5tu replied to 5tu's topic in Internet Related/Filtering/Firewall
We do have Impero but have removed it from a test machine and the issue remains unfortunately. -
Smoothwall not filtering gamepluto.com
5tu replied to 5tu's topic in Internet Related/Filtering/Firewall
Thanks for the post - Doesn't seem to make a difference. Visiting google.co.uk and/or google.com and checking the site's cert shows that the mitm certificate isn't being applied. -
Smoothwall not filtering gamepluto.com
5tu replied to 5tu's topic in Internet Related/Filtering/Firewall
Yep - first thing we checked -
Smoothwall not filtering gamepluto.com
5tu replied to 5tu's topic in Internet Related/Filtering/Firewall
So... just had an hour long session with 2nd line support and we've found that Google Search isn't being https inspected, despite there being no policies in place exempting Google from inspection. Other search engines are being inspected correctly. Escalated to 3rd line.... Edit: I don't understand why users are able to access sites which should be blocked via Google Search results. Maybe that's another issue. Glad to have (finally) made it through to 3rd line. -
Enforced 2FA: Conditional Access solution in schools
5tu replied to AnimatedCarrots's topic in Windows
MS knew what they were doing when they got schools onboarded to 365 with free A1 Plus licences. I think we all knew free wouldn't last forever and we now quickly find ourselves needing ever increasing licence subscriptions to get the functionality we require. Edit: We bit the bullet a couple of years ago and opted for A3 / P2 licensing. -
Enforced 2FA: Conditional Access solution in schools
5tu replied to AnimatedCarrots's topic in Windows
You can exclude your students from the policy requiring users to enrol in MFA. Entra Admin Center > Identity > Protection > Identity Protection > Multifactor authentication registration policy However, I feel this is just kicking the can down the road. It's 2024 and we need to get all users protected with MFA... but the challenges of doing this in a school environment are significant - not all kids have phones, kids would lose physical tokens etc etc. -
Smoothwall not filtering gamepluto.com
5tu replied to 5tu's topic in Internet Related/Filtering/Firewall
Just had a remote session with Smoothwall support and demonstrated the issue - web filter logs show sites are blocked when they aren't. Smoothwall not sure why at this point and further investigation required. Will update this post when I hear back. -
Smoothwall not filtering gamepluto.com
5tu replied to 5tu's topic in Internet Related/Filtering/Firewall
Thanks @CSmith. I think I'd rather share it via my open ticket - ref #490104. I'll upload it now. -
Smoothwall not filtering gamepluto.com
5tu replied to 5tu's topic in Internet Related/Filtering/Firewall
The only possible "google" item I can find being excluded from authentication is "Connect for Chromebooks" in the "Authentication exceptions" Category group. Would someone mind please checking their config to see if this is standard or not?