IrritableTech
-
Posts
1,738 -
Joined
Content Type
Forums
News
20th
EduGeek EDIT Conference
Blogs
Everything posted by IrritableTech
-
I have suspected that YouTube for schools was nearing end of life. We tried to sign up with a generic account back in September and got the error message. We are using it successfully, but using a code attached to my work email which I signed up for probably over a year ago - not ideal but working. I'll be interested to see the Lightspeed solution and see if it is a workable solution - presumably the other big names will follow quickly if it is.
-

Article: BETT 2015 - The EduGeek Stand
IrritableTech replied to Dos_Box's topic in Legacy CMS Comments
Only trouble is I'll need the socks well before I get to excel - station platforms up north at 6am bring a particular chill to the ankles! See you Friday! -
Capita Sims InTouch is available as an SIMS addin and will do this. Otherwise there are all kinds of programs that will interrogate the sims database outside of sims and achieve the same.
-
I was worried to start with that it was going to be a cheesy. In the end, I thought it was very very well done. Yes the messenger app text was a little unrealistic, the voice was a slight stretch, but it was needed to make the programme easier to watch (text and one person talking would not have been as enthralling). However those aside I found Cyberbully very powerful. Ratting (using malware to take over a 'slave' pc and accessing the webcam) is a known issue. It seems to be on the increase and techniques are getting more advanced. Ratters have techniques to turn off the LED on many webcam models and have and do take stills and videos of their victims and share between themselves and the wider world. Most would not inform their victim they were doing such a thing though, and quietly collect footage. A very concerning trend. Watching the program I could see a number of cases over the last year or two which they had used for inspiration. They covered a great deal of eSafety topics in such a short time I think this could be a very useful program for schools. The issue of some language and themes is a difficult one. We all know that most of the pupils in high school have unfortunately heard (if not used) the level of language used in the programme - and worse. Without some language, the programme would not have seemed as realistic as it did to me. The themes included have actually happen to real young people in this country and abroad. There's no getting away from that fact. Cyberbullying, anonymous trolling, self harm, suicide, self-trolling, naked selfies, revenge porn are real issues happening to young people in this country (thankfully still fairly rare) and I for one think children and young people need to think about how their actions affect others. What age is Cyberbully suitable for? The million dollar question. It's likely that one class of year nines may be more mature than another class of year ten. I don't think we should necessarily suggest one age or another. Parents and teachers know their pupils best. I'd be interested to get senior leader backing and then ask for parental feedback as to whether they'd be happy for the school to show the programme within PHSE or a longer course around eSafety. Cyberbully was full of important themes which could help safeguard young people.
-
Is it ok to store everything on the cloud?
IrritableTech replied to abillybob's topic in Cloud Services
Unless things have changed (I'd love to please see a link if it has) I don't think Google guarantee where your data will be held. They do however encypt everything now, are on the Safe Harbor list and have completed an exercise to show adequate data safeguards - enough so the DFE have published the self assessment. If your school is happy with all of that, and you ensure your ICO entry states that data may be kept outside of the EEA, then it should be ok. Your school must go through the risk assessment, and shouldn't just take all of the above as approval. After the legal side - bandwidth and resilience would be the main stumbling block. Then you need to think about the usability of using such a service over local file management. Google self assessment regarding Data Protection - https://www.gov.uk/government/publications/cloud-software-services-and-the-data-protection-act -
Sounds like an IP address, VLAN or gateway address issue to me. Anything changed there? Are you seeing AP's requesting a DHCP lease? Looking at the zone director, are the APs static, and what should there address be? Is it in the same subnet as everything else? If not, have you done anything with VLANs on the switches?
-
Free basic "print report" for primary school
IrritableTech replied to burgemaster's topic in Windows
I think papercut still do the basic reporting software for free? It logs to a csv file, you could manually create so stats in excel. [edit] Actually it's even better these days... http://www.papercut.com/products/free_software/print_logger/ -
IrritableTech -> Friday
-
Edugeek - IrritableTech Twitter - MrAdamWelch Attending all day Friday.
-
I've just moved to an iPhone 6. Even in my fairly large hands using it one handed can be a stretch for my thumb to reach the top left corner. I'd suggest the 6+ is a two handed phone (or phablet). For me it was the right decision to buy the 6 rather than the 6+.
-
I guess my question should have been Why do people need to print emails? Leave it as bits and bytes and it's searchable, backed up, traceable etc. etc.
-
Who prints emails? Trying my best to go completely paperless this year, but I can honestly say it's been a very, very long time since I last printed an email.
-
Pay as you Go - Limit calls + texts to a select group of numbers
IrritableTech replied to chris_uk's topic in General Chat
See what you are saying about the idea, but I've found a bit of trust and an open conversation can go a long way. You can restrict apps like safari as I explained in my earlier post.
-
Pay as you Go - Limit calls + texts to a select group of numbers
IrritableTech replied to chris_uk's topic in General Chat
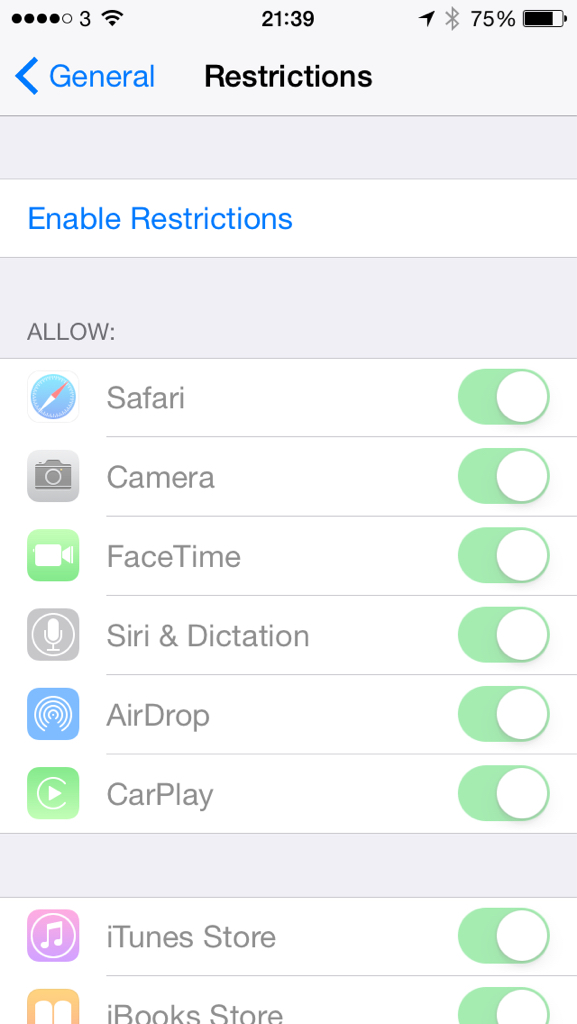
Our daughter has an iPhone, but doesn't have an iTunes account. Any apps are put on there by us. There doesn't seem to have been any suggestion why the girl can only contact five people, the girls age or any further info. Phones are not inherently bad! The most important thing here are some simple, but reasonable ground rules with the device, and a long conversation about the reasons for the rules. You can set rules on which apps can be run without a parental pin. So you can stop access to safari for instance - as well as pretty much everything else. Trust will go a long way, and when the rules are pushed a little, new rules or sanctions can be set in place. -
Google Apps for Education for authentication only
IrritableTech replied to CyberDrac's topic in Cloud Services
Yep - but the password sync only sends changed passwords if I remember correctly - so you'd need to force a change on your AD passwords to get it to work. -
Google Apps for Education for authentication only
IrritableTech replied to CyberDrac's topic in Cloud Services
@fiza is correct you can do that. This approach probably works best if you are synchronizing your though. Otherwise users may get confused with the same username being used in two places with potentially different passwords. -
Google Moving to SSL Searches
IrritableTech replied to Boredguy's topic in Internet Related/Filtering/Firewall
I've decided to post some further info in a forum which is for registered users only - it contains some potentially important advice for those who aren't doing HTTPS inspections. http://www.edugeek.net/forums/security/146987-google-safe-search.html -
Google Moving to SSL Searches
IrritableTech replied to Boredguy's topic in Internet Related/Filtering/Firewall
Nope - still ways around that, but you can sit smug in the knowledge that you've already done what we will probably need to do very soon! :-) -
Google Moving to SSL Searches
IrritableTech replied to Boredguy's topic in Internet Related/Filtering/Firewall
Cracked it... for now. Thanks all. -
Google Moving to SSL Searches
IrritableTech replied to Boredguy's topic in Internet Related/Filtering/Firewall
Me too. I think that is the issue. My ISPs DNS server are set to 216.239.38.120. They've done it as an IP rather than a CNAME and the IP has changed... I think. -
Google Moving to SSL Searches
IrritableTech replied to Boredguy's topic in Internet Related/Filtering/Firewall
Those who aren't getting SSL google, can you do me a favour? Can you tell me what IP address nosslsearch.google.com comes back with please? -
Google Moving to SSL Searches
IrritableTech replied to Boredguy's topic in Internet Related/Filtering/Firewall
I'm not with RM and haven't installed the certificate - should have added that. That page should fail for me! -
Google Moving to SSL Searches
IrritableTech replied to Boredguy's topic in Internet Related/Filtering/Firewall
Well you've got impero which sounds like it is helping. I've written a blog about the potential safeguarding issues. It's not perfect, but may explain my concern. http://irte.eu/q6 -
Google Moving to SSL Searches
IrritableTech replied to Boredguy's topic in Internet Related/Filtering/Firewall
Failed for me when I tested it. -
Google Moving to SSL Searches
IrritableTech replied to Boredguy's topic in Internet Related/Filtering/Firewall
Are you still searching without SSL on google then @localzuk ? We were, until this morning - and I don't think my supplier has changed anything - we've still got the DNS hack in place.