jthompson
-
Posts
5,685 -
Joined
-
Last visited
Content Type
Forums
News
20th
EduGeek EDIT Conference
Blogs
Everything posted by jthompson
-

Teacher access to students' Google Drives
jthompson replied to BlueSkies's topic in ChromeOS & Cloud Based OS
Admins would need to use gam or Google Vault to search for files and content in users' Drive accounts, but you almost certainly don't want to be making either of those available to regular staff. What you're after is a Google Drive equivalent of Gmail's delegated access feature, but no such thing exists. -
Windows 10 LTSC 2019. Supported until end of 2028. Or LTSC 2021, which is supported until end of 2026. YMMV in terms of keeping applications up to date on that. For instance, the latest release of Affinity apps requires a version of .NET that isn't supported on LTSC 2019.
-
It might just be that you've browsed a public post from that group (whilst signed in to Google) when browsing the web researching some problem or other.
-
New ISP - Yealink phones losing connectivity
jthompson replied to mikkydoos's topic in Internet Related/Filtering/Firewall
The former. For reference, we use Yealink handsets with a service hosted by Telavox, so after referring to their firewall support article (https://support.telavox.com/en_US/network/firewall-and-network) we added into our Smoothwall exceptions list 80.83.208.0/20 (i.e. the telavox network) and the two IPs listed there for Yealink. We did also add in the LAN IP addresses of our phones. I don't know if that's needed (probably?) but certainly just the LAN IPs wasn't sufficient to solve our problem. -
New ISP - Yealink phones losing connectivity
jthompson replied to mikkydoos's topic in Internet Related/Filtering/Firewall
Further to my post, here is a list of IPs used by Yealink handsets for provisioning, etc. regardless (I think) of which VOIP provider you're using them with. IIRC we have the IPs listed here for "Redirection provisioning service" included in our Smoothwall HTTPS inspection exception list. https://support.yealink.com/en/portal/knowledge/show?id=6476e6806a27da76bd06a8d2 (the breadcrumbs in that page will link to IPs used in regions other than Europe). Again, I don't know if that helps but it might give you some more stuff to try. -
New ISP - Yealink phones losing connectivity
jthompson replied to mikkydoos's topic in Internet Related/Filtering/Firewall
Can't quite follow all the details in your original post, but we recently switched to Smoothwall and had some intermittent issues with calls not connecting to certain phone handsets. It felt like certain Yealink models were more affected than others. Our solution was to add our VOIP service provider's IP range into "Smoothwall > Guardian > Web Filter > Exceptions > Manage source exceptions". This was because Smoothwall's HTTPS inspection was occasionally breaking stuff, and including the phones' IP addresses in that list wasn't sufficient. I don't know if that helps at all. -
I think that used to be the case, but GCDS was updated recently to make this a bit easier. It still doesn't used a GUID to link AD groups to Google groups (as it does for users). If you update the AD group's mail attribute, and then manually update the Google group's email attribute (either in Google Admin or in Google Groups) to match exactly, and then run GCDS with the flush cache option, it should behave and sync the group as required, without creating a new one. When you change the group address in Google Admin/Groups, the old address is added as an alias (similar to how it would when changing a user's primary email address), so if you definitely don't want the old group address to hang around you'll want to remove it from there as well.
-
Allowlisted here, so users can't install whatever they like. We would check for GDPR stuff, and a general smell test for how established/stable the app looks. We tend to err on the side of not allowing things, since your users may end up with resources that rely on a thrid-party app which may end up abandoned, sold or switched to a differnet pricing structure. We knocked up a Google Form that we use to record the details of any third-party stuff that we allowlist, so that we can record app IDs, who requested it, why, when, etc. That's helpful when periodically reviewing things.
-
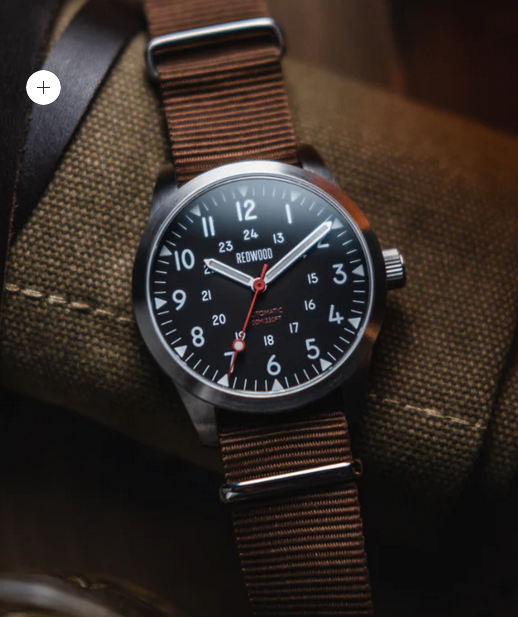
That Baltany is certainly pretty. I'm getting after-dinner mint vibes, too. The watch I've been contemplating the most of late is the Redwood Kilroy, a solar field watch that looks nice and hardy. If it had a date window I'd be even more sold. I like the look of pretty much all of their watches. https://www.redwoodwatches.com/

-
I seem to have recently developed a taste for looking at pretty watches on the Internet in recent months. Most days now there is some watch or other spending time loitering in my brain's shopping basket. I've traced it back to being left by my OH waiting in front of the watch cabinets in a department store. A cabinet full of Mondaine watches stole my heart. I've been wearing an Omega Seamaster (mid-size, quartz, "Peter Blake") pretty much every day for 20 years, and in all of that time only two people have ever said "Is that a Seamaster?!" and asked for a closer look, so it's quite clear to me that pretty much nobody cares/notices what watch you wear. I recently bought a Wenger chronograph on clearance from TK Maxx just because I really liked the look of it, but that's tought me a few of things: 1: a 30-minute chronograph is almost useless to me. No use for timing parking or cooking, really. 2: a chronograph can look pretty in pictures with the hands at 10:08:40, but when the main second hand spends most of the time parked at 12, a chronograph can look a bit 'dead'. 3: NATO straps FTW! I'm enjoying getting more familiar with watch terminology. One thing that really puzzles me though is why G-Shock watches seems to enjoy near universal acclaim amongst watch people, despite appearing to have such a naff design language. I like the idea of an indestructable solar atomic watch with 5 vibration alarms and 10 countdown timers, but I'd rather it not look like a tractor tyre with a cheapo LCD display in the middle.
-
Canva and Affinity: Any way to pre-link?
jthompson replied to NegativeKillDeath's topic in Cloud Services
I don't think so. I've not found any reg options or command line parameters that affect the launch behaviour so as to display the "Login with Canva" option off the bat. I've also tried copying the URL that the "Login with Canva" button takes you to, to see if that can be generalised so as to be able to launch one of the desktop apps from the web browser, but no joy. Maybe someone else can make more sense of the URL to see if generalisation is possible?- 1 reply
-
- 1
-

-
In a similar vein to Duck.ai, Proton have now launched Lumo, their privacy-focussed AI chatbot. Where Duck.ai is just a proxy to OpenAI, Claude, etc, Lumo appears to be being run on Proton's own servers, using open-source models. I'm not much of a judge of AI tools, but I like an AI product has finally assumed cat form.
-
No, I'm not seeing that. Even for users with existing keys (i.e. the ones with a secuity shield badge against their name in the list of users).
-
Instead of making The Naked Gun again, Seth McFarlane should try making Ted again, because that film was really bad.
-
In my experience, the licenses have always just been named "Chrome Enterprise Upgrade" and have been a one-off puchase for the life of a device (of around £20-30). Looking in my Workspace Admin now, I can see that that has now maybe changed to a new model. Our existing licenses are now listed unter a heading of "Chrome Enterprise/Education Upgrade (Standalone, perpetual)", which is the first time I've seen 'Education' in the naming of them. There also now appears to be another section alongside that named "Chrome Enterprise upgrade (Standalone, fixed-term renewable plan)", which could be the new way of selling licenses now? Your quoted price of £3.33 per device per month (£40 per device per year) tallies with https://chromeos.google/intl/en_uk/products/device-management/#action-quadrant-os-device-management which I'm assuming would be for that type. The perpetual option on that page might just be exactly what we've always been buying, but I can't tell just from that page whether or not there's some new mechanism at play there. From Google's perspective, future price increases would apply to pre-existing licenses in a way that the perpetual licenses wouldn't, so super for them 😐
-
It took all of a week, but Grok sees your reasonable boundary and looks to burn it down. https://techcrunch.com/2025/07/15/of-course-groks-ai-companions-want-to-have-sex-and-burn-down-schools/
-
Have been wanting to move on from SIMS for years, and we're finally in the process of doing so. I don't really care what we move to, tbh: as long as it gives us an API, I'm sold!
-
I got about a billion announcements about upcmoing changes to MFA, but my problems weren't with MFA, it was just basic user admin. I guess I dismissed things too readily. The site shows a notification about changes to admin when hitting the CPOMS dashboard page, but not when hitting the CPOMS admin page, which is what I had bookmarked as it's pretty much the only area of CPOMS that I use.
-
Awesome, thank you. I'm sure I navigated in there originally but perhaps is was broken when I tried. Yeah, I'm going to say that it was broken when I originally tried
-
Just joining in the communal rant here. CPOMS support has fallen off a cliff. Not able to adjust any user privileges or manage user accounts at all. It's been that way for a couple of weeks with absolutely nothing back from CPOMS support. Thanks @Scifigirl for the link to the status page. I'll be bookmarking that.
-
Presumably it will be Chromium-based. I'd expect it to be more of a threat to Edge, tbh.
-
I can't remember how these differ between W10 and W11, but take a look at the quick toggles (in the same panel as the volume slider) and decide whether you want to prevent your end users from toggling Flight mode and Mobile hotspot. Defunctioning the Flight mode toggle is done by using Group Policy to set the Radio Management Service Windows service to disabled. Defunctioning the Mobile hotspot toggle is done in Group Policy using Computer Configuration -> Policies -> Administrative Templates -> Network -> Network Connections -> Prohibit use of Internet Connection Sharing on your DNS domain network.
-
Good spot. I hadn't noticed that before, but then we have no groups that externals can send to. Worth noting that whilst there's no banner on the incoming group message, I'm testing it here and seeing a yellow warning banner when composing a reply. "Be cautious about sharing sensitive information. [email protected] is outside your organisation and isn't in your contacts." Whether that banner is a result of the same option in Admin, and whether it would be shown if the sender was in my contacts, IDK yet. I suspect the address in the To field of the reply would by underlined in yellow regardless, but that's quite a subtle visual cue just on it's own.
-
The banner is useful, yes, but it also means that if John Doe emails a couple of colleagues (either by honest mistake or indisciplne) from his Hotmail account, then if said colleages start replying, the Hotmail recipient will be highlighted in the recipeints field as a nudge to remove it and replace it with an org address.
-
Looking forward to seeing it at some point, although Steve McQueen's Le Mans is my benchmark for motorsport movies, closely followed by Rush. Ford V Ferrari was good, but the Le Mans scenes were noticebly filmed elsewhere (Road Atlanta?), so it lacked something essential.