

-
Posts
13 -
Joined
-
Last visited
Content Type
Forums
News
20th
EduGeek EDIT Conference
Blogs
Everything posted by EduGeek
-
 The Department for Education has made another round of amendments to its Meeting digital and technology standards in schools and colleges manual, with the latest changes published on 25 August. Taken together, this year's updates focus on three areas: generative AI in filtering and monitoring, the new Cyber Essentials 2026 requirements, and Wi-Fi 7. They are worth working through before the first safeguarding and IT review of term. What has changed in 2026 Generative AI and filtering (25 August and 10 June). The filtering and monitoring core standard now directs schools to the DfE's Generative AI: product safety standards whenever they introduce a specific AI product. Your annual review should now cover where AI tools are used across web and in-app products, and whether your filtering and monitoring solution can actually handle real-time, dynamic, personalised and AI-generated content. Rolling out a new generative AI tool is also listed as a trigger for reviewing provision outside the annual cycle. Cyber Essentials 2026 (24 June). The cyber security core standard has been revised to reflect the new technical requirements the NCSC introduced in Cyber Essentials 2026. If you hold or are working towards certification, compare your current controls against the updated requirements. Wi-Fi 7 (17 April). The wireless network standard now includes Wi-Fi 7 requirements. Importantly, the DfE clarifies that schools only need to upgrade when their existing wireless network no longer meets their needs, so this is not a mandated refresh. Security updates (7 April). The cyber security standard now makes clear that fixing a vulnerability can involve changes beyond applying a software patch, which is relevant to how you evidence remediation. Report Fraud (12 February). References to Action Fraud have been updated to its new name, Report Fraud. Check your incident response plans and staff guidance still point to the right place. Filtering clarifications (January and February). The DfE added further detail on filtering solutions to the technical requirements and clarified timing: schools and colleges should already be meeting the filtering and monitoring standard now. Worth rechecking this term The filtering and monitoring standard is one of six core standards, and the DfE expects all six to be met by 2030. The current text is explicit on several points IT teams should verify: IWF and CTIRU blocklists must be in place and must not be possible to disable or override by anyone, including system administrators at school, trust or local authority level; any temporary filtering exceptions must be approved and documented by the responsible SLT member; and monitoring plans should include weekly incident reports, immediate alerts for high-risk incidents, and a documented process for recording what action was taken. Source: Department for Education · Read the update (NOTE: This has been abbreviated by AI so double check things)
-
We are very please to announce our real-world conference for 2026 once more! Following the decision to pivot EDIT 2026 to an online event in May due to global events, we are finally back on the road in October! Join us on Tuesday the 27th of October at the Museum of Making in Derby for the free EduGeek EdSec Conference, for a day of EdTech security focussed talks, networking, and an evening social. Once again, we have a raft of top EdTech industry speakers for this conference with the following already booked and confirmed, with more to come (we’ll keep you posted as and when they confirm): Sophos Smoothwall Nellcote Heimdal Others TBA On top of that, we have the expo as well, and are very much looking forwards to welcoming the following companies to join us (more to come): Salamandersoft Smoothwall ICT Direct Net-Ctrl LGfL Wave9 Schools Broadband Heimdal Door Entry Sign (Osbourne Technologies) Nellcote Others TBA Location and Timings: EduGeek EdSec 2026 will be held on Tuesday the 27th of October 2026 at the Museum of Making in Derby. Address: Museum of Making, Silk Mill Lane, Derby, DE1 3AF For more details about parking see:
-
Post any questions below or email events(AT)edugeek.net Location and Timings: EduGeek EdSec 2026 will be held on Tuesday the 27th of October 2026 at the Museum of Making in Derby. Doors will be open at 09:00 for drinks and snacks and the conference will kick off with the keynote talk at 10:00 The conf is scheduled to finish at 16:00. Address: Museum of Making, Silk Mill Lane, Derby, DE1 3AF After Conf Social: For all of you staying overnight, we are please to announce that LGfL will be hosting you all in the evening for a meal and lots of socialising and geek based chat Travel: The Museum of Making is easily accessible by car or public transport. It's a mere 15 min walk from Derby Railway Station and goes through a park by the River Derwent (it really is quite lovely), and there are plenty of car parks a few mins walk to the venue nearby (sadly no on-site parking is available). Hotels: There is a Premier Inn (Derby City Centre) a mere 3 mins walk away with others very close by. Premier Inn link: https://www.premierinn.com/gb/en/hotels/england/derbyshire/derby/derby-city-centre-cathedral-quarter.html
-
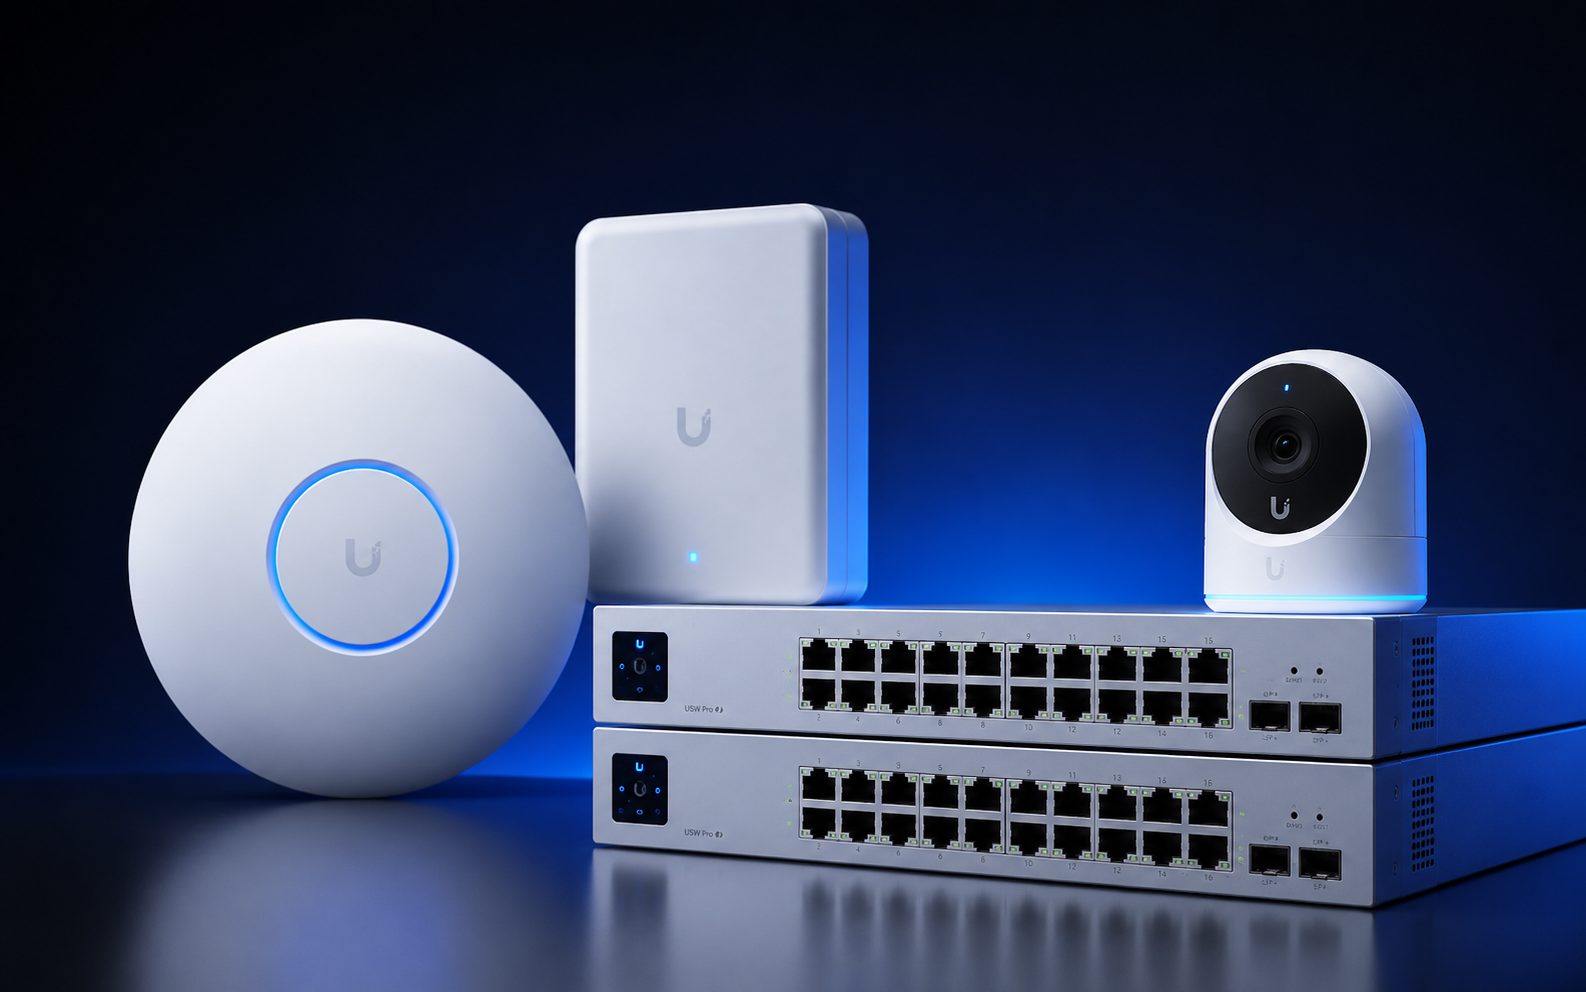 If you manage any UniFi kit, it is time to schedule a maintenance window right away. Ubiquiti’s Security Advisory Bulletin 067 is a massive patch drop fixing 22 vulnerabilities across the stack, including three separate unauthenticated CVSS 10.0 flaws hitting UniFi Protect, UniFi OS, and UniFi Talk. The Heavy Hitters Having three simultaneous maximum-severity vulnerabilities in a single release is rare. None of them require existing credentials or user interaction, which makes them prime targets for anyone scanning your subnets. The first big issue is CVE-2026-77537, a command injection bug in UniFi Protect that lets network attackers execute arbitrary commands directly on the host appliance. The second, CVE-2026-77550, is a CRLF injection flaw in UniFi OS that allows attackers to completely bypass authentication across Cloud Keys, Dream Machines, and UNVRs. The third, CVE-2026-77554, delivers another remote command injection vector inside the UniFi Talk VoIP suite. The rest of the bulletin fixes 19 other issues ranging from CVSS 8.2 to 9.9. These cover privilege escalation, exposed debug endpoints, and secondary injection bugs across UniFi Network, Access, and Connect. Component Issue Type Affected Fixed In UniFi OS Server Auth bypass / Priv escalation ≤\le≤ 5.1.21 5.1.37+ UniFi OS Consoles (UDM, UNVR, Cloud Key) Auth bypass / Priv escalation ≤\le≤ 5.1.26 5.1.31 / 5.1.32+ UniFi OS Express Auth bypass ≤\le≤ 4.0.16 4.0.17+ UniFi Protect Remote command injection ≤\le≤ 7.1.87 7.2.105+ UniFi Talk Remote command injection ≤\le≤ 5.2.7 5.3.2+ UniFi Network Priv escalation / Command injection ≤\le≤ 10.4.57 10.5.67+ UniFi Access Priv escalation / Command injection ≤\le≤ 4.3.3 4.3.5+ UniFi Connect Priv escalation ≤\le≤ 3.24.20 3.24.22+ UID Enterprise Agent Command injection ≤\le≤ 1.61.8 1.62.1+ Protect AI Key Priv escalation ≤\le≤ 2.1.3 2.2.6+ More details: https://community.ui.com/releases/Security-Advisory-Bulletin-067/fc4a3488-7c43-4628-8bab-f715e96dbfc9
-
 If you have a PaperCut application server sitting on the public internet, stop what you are doing and restrict network access immediately. PaperCut Software has issued an urgent advisory warning of active, in-the-wild exploitation targeting both PaperCut NG and PaperCut MF, accompanied by out-of-band emergency security patches.papercut Active Exploitation and Flaws Security teams at PaperCut, Huntress, and watchTowr confirmed that attackers are actively chaining two newly disclosed vulnerabilities to compromise print servers. The attack vector allows an unauthenticated adversary to bypass access controls and achieve remote code execution under the context of the PaperCut server process. CVE Severity Vulnerability Type Impact CVE-2026-81578 CVSS 8.8 (High) Authentication Bypass (CWE-306) Permits unauthenticated remote attackers to invoke administrative routines and alter system configurations CVE-2026-82078 CVSS 9.4 (Critical) Unsafe Class Loading (CWE-470) Allows execution of arbitrary Java bytecode via dynamic database connector instantiation When chained together, an unauthenticated attacker can manipulate database driver configurations remotely, instantiate malicious Java classes residing on the application classpath, and execute arbitrary operating system commands.papercut What Attackers Are Doing Telemetry and forensic data from affected environments reveal a consistent post-compromise routine once attackers pop the pc-app.exe server process.papercut The PaperCut process spawns cmd.exe to run early reconnaissance commands such as whoami & ver, tasklist, and nltest /dclist:.papercut Attackers pull secondary payloads to C:\ProgramData, including temporary execution binaries.papercut Persistence is established via rogue remote access tools, specifically installing a Windows service called "Remote Access Service" (a SimpleHelp agent running SimpleService.exe) or staging AnyDesk.papercut Log tampering is common, including deleted, missing, or unexpectedly truncated server.log files.papercut Indicators of Compromise Administrators should inspect their application servers for specific file and log artifacts.papercut Look in server.log for strings matching jdbc:derby:memory:pwn;create=true, VALUES CAST(X'cafebabe', or DB Driver: <5-char random name>.papercut Check for temporary files on disk matching <install>\server\lib\<5-char-name>.class or scripts inside <install>\server\data\content\.papercut Audit Windows services for unexpected entries running SimpleService.exe under LocalSystem.papercut Query EDR and SIEM tools for any child processes spawned directly by pc-app.exe or pc-app.papercut Emergency Patching and Remediation Because this is an active zero-day campaign, PaperCut bypassed its standard release cycle to publish hotfixes across versions 24, 25, and 26. If you find you have any indication of compromise its recommended to isolate the server, wipe and rebuild. Details: https://www.papercut.com/kb/Main/security-bulletin-27-aug-2026-urgent-security-advisory
-
 Free Webinars: Building an Engaging Intranet with Cloud Design Box Sign up for the free Cloud Design Box webinars here Join Cloud Design Box and Thinking Schools Academy Trust for a series of free webinars. Learn how to centralise resources, and build an engaging intranet for your Multi-Academy Trust or school. Go beyond standard Microsoft Teams and SharePoint approaches to streamline communication and enhance engagement for staff and students: How Thinking Schools Academy Trust launched an Intranet for 26 Schools: Listen to TSAT talk about their journey to create a SharePoint Intranet that boosts communication and engagement. Click here to sign up. Onboarding schools made easy: See how Cloud Design Box’s Staff Directory and News Centre simplify MAT onboarding for new schools and staff. Click here to sign up. Work Smarter in Class Teams: Learn expert techniques and tools for saving teachers time by centralising resources and reducing file duplication. Click here to sign up. Cloud Design Box helps MATs create an Intranet to post news and information about central services to wide audiences with features such as a staff directory and site templates. Create spaces for central team collaboration and bring schools together through automation and onboarding. Cloud Design Box extend Teams and SharePoint to make it a full virtual learning environment, with features such as Teams/SharePoint automation, Class Teams connections to centralised resources, assignment analytics, student assignment search, class teams cover, Viva cards and SharePoint web parts. Get great usage with our User Adoption and Training programme for teachers and non-teaching staff. If you want to find out more or arrange a personalised demonstration, contact the Cloud Design Box team: Email: [email protected] Phone: 01482 688890 Website: https://www.clouddesignbox.co.uk/contact
-
 Groupcall has been dedicated to developing software to help educational organisations for over 15 years. Our products reduce administration, improve parental communication and help schools get the most from their data. In addition to developing resources and running nationwide training sessions to help schools prepare for the GDPR, Groupcall has partnered with GDPRiS to offer schools a cost-effective, complete GDPR management solution. Contact Information: Via EduGeek PM: KLayer || Greed Web: www.groupcall.com E-mail: [email protected] Telephone: 020 8506 6100 GDPRiS is a low-cost solution designed specifically to offer schools simple, intuitive data protection processes and management. GDPRiS will: • Deliver clarity on the complexities of GDPR • Drastically reduce workload surrounding 3rd party due diligence and by offering instant data mapping • Encourage a whole-school approach to data protection • Provide evidence-based accountability Our team of education professionals have more than 40 years experience working in and with schools including data management, communications, online payments, compliance frameworks and data protection. We are here to advise, support and work with schools not only in the months leading up to the enforcement of GDPR in May 2018 but far beyond. Contact Information: Via EduGeek PM: MatureLady Web: www.gdpr.school Email: [email protected] Telephone: 0203 256 2018

-
- 1
-


